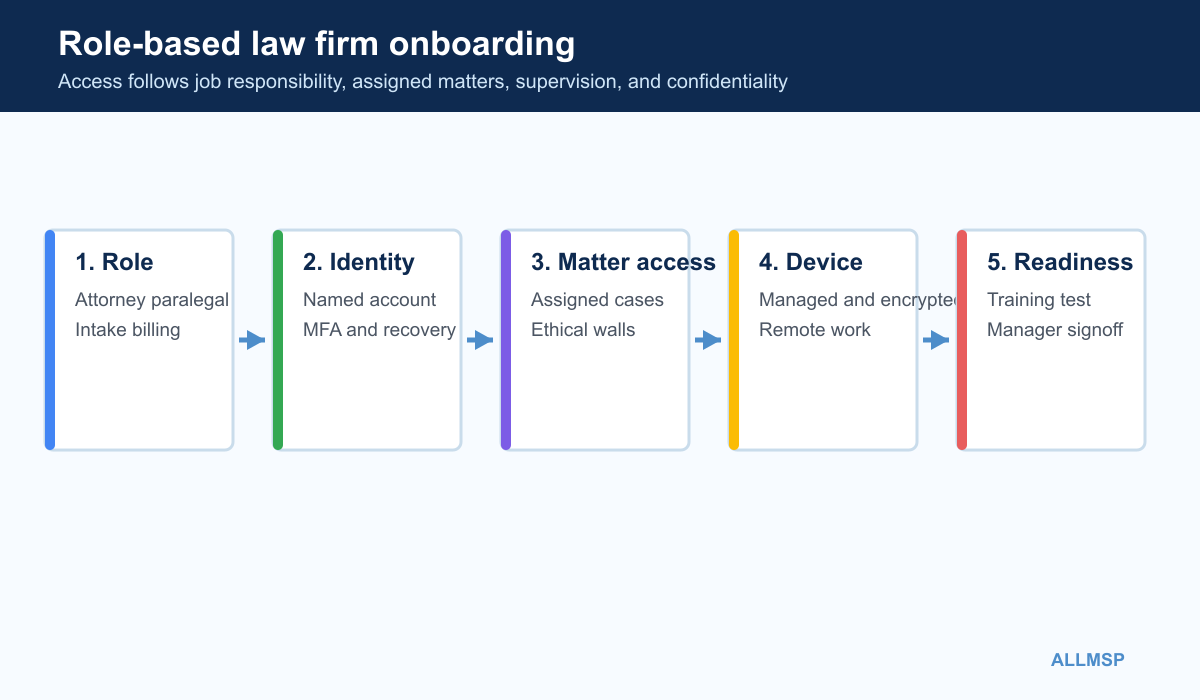
A law firm employee workflow should begin with the person’s role and assigned matters, not a copy of another user’s accounts. Attorneys, paralegals, intake, billing, administrators, interns, temporary staff, and contractors need different systems, matter scope, supervision, devices, training, and departure steps.
Managers, responsible lawyers, HR, and IT should agree on approvals and records before access is issued. Employment law, professional responsibility, privacy, records, client requirements, and contractual decisions remain with the firm. Technology controls should implement those decisions consistently and preserve evidence.
What a dependable law firm employee lifecycle setup should accomplish
A dependable employee lifecycle provides a named identity, role-based systems, matter-specific access, secure equipment, tested business applications, confidentiality and technology training, coverage for deadlines and client work, and an offboarding plan prepared before the first day.
- The role, supervisor, responsible lawyer, start date, location, employment type, assigned matters, systems, device, and exceptions are approved.
- Accounts are named, protected with MFA, connected to managed devices, and issued through role groups rather than copied manually.
- Matter access and ethical-wall decisions are documented separately from broad job-title access.
- Confidentiality, secure communication, remote work, phishing, AI use, records, deadlines, and incident reporting are tested by role.
- Leave, reassignment, supervision, and urgent coverage protect matters and deadlines when an employee is unavailable.
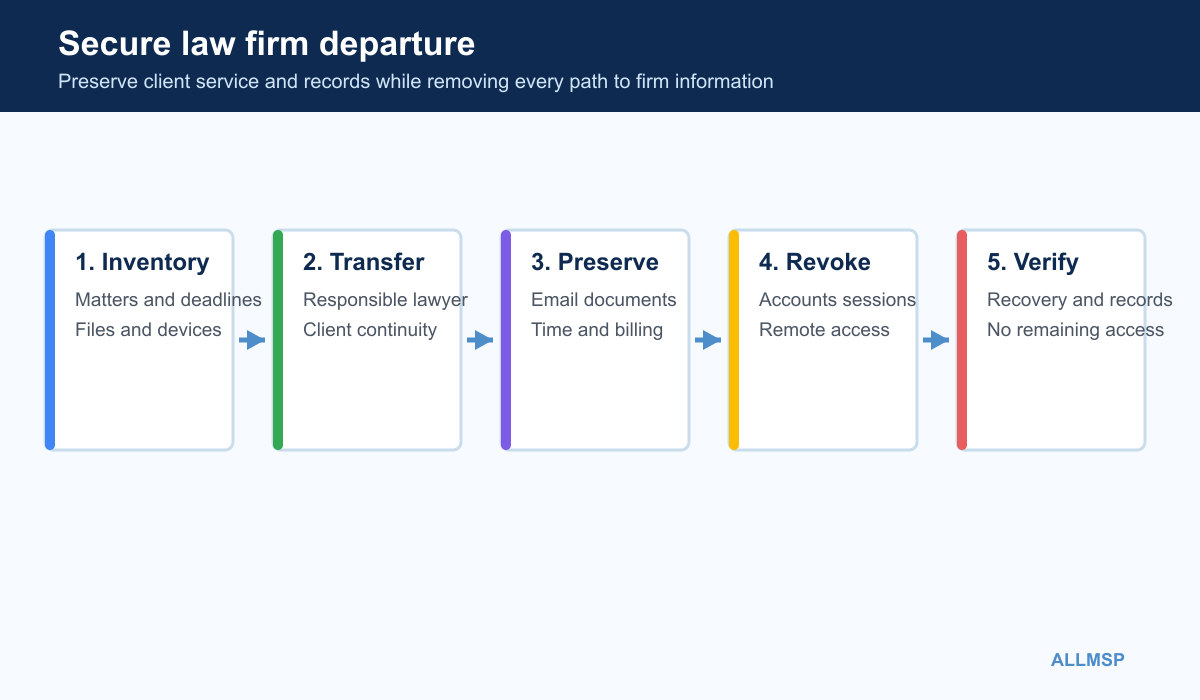
- Departure transfers matters and records before accounts, sessions, devices, recovery, vendors, and physical access are closed.
Define the role, matters, supervision, and approvals
1. Create the role and responsibility record
List the work the person will perform, client and financial information involved, systems required, matters or practice groups, supervision, approvals, physical access, mobile needs, and temporary exceptions. Do not use another employee as the access template without review.
Where to work: Approved job description, supervisor, responsible lawyers, department, office or remote status, employment type, and start date
Verification: The manager, responsible lawyer, HR, and IT can explain why each requested system and privilege supports a real duty.
2. Separate role access from matter access
Use the role to grant baseline systems, then assign matters from approved teams. Define restricted matters, conflicts, ethical walls, emergency access, temporary coverage, and who can change the team. Avoid giving every attorney or assistant access to every client by default.
Where to work: Role matrix, practice management, document groups, email spaces, billing, e-discovery, ethical walls, and matter-opening process
Verification: A pilot account reaches baseline tools and assigned matters but cannot find or open a restricted matter through search, links, groups, or integrations.
3. Create named identity and recovery
Create an individual account, require MFA, enroll approved recovery, prohibit shared passwords, and separate privileged administration. Use consistent naming and manager records so accounts can be identified during access and departure reviews.
Where to work: Identity provider, email, practice tools, password manager, MFA, administrator portal, and emergency access
Verification: The employee signs in and recovers through approved methods, while the manager cannot use or request the employee’s password.
Prepare identity, devices, systems, and training
1. Prepare managed devices and remote work
Assign and record equipment, enroll management, escrow encryption recovery, deploy approved software, remove routine local administration, and configure secure remote access. Address confidential calls, screens, printing, household sharing, lost devices, and public networks.
Where to work: Device inventory, encryption, endpoint protection, patching, local privilege, VPN or secure access, office network, home workflow, mobile policy, and remote support
Verification: The employee completes the expected office and remote workflow on managed equipment without personal email, consumer storage, or shared household devices.
2. Assign practice, document, communication, and billing tools
Assign the lowest role that supports the person’s tasks. Configure templates, default save locations, signatures, phone routing, calendars, time categories, and integrations. Separate billing and trust functions according to approved responsibilities.
Where to work: Practice management, document repository, email, calendar, Teams or collaboration, phone, e-signature, research, time entry, billing, and accounting
Verification: The employee can open a test matter, create and locate a document, communicate securely, record time where required, and cannot reach unauthorized financial functions.
3. Deliver role-based confidentiality and security training
Use scenarios from the employee’s work. Have the person identify unsafe recipients, suspicious payment changes, confidential information in an AI prompt, a lost device, an exposed document, a restricted matter, and an urgent deadline. Include how to obtain help without hiding mistakes.
Where to work: Firm policies, client requirements, secure communication, phishing exercises, matter access, remote work, records, devices, AI rules, and incident reporting
Verification: The employee completes a scored exercise and demonstrates when to verify, stop, report, use a secure channel, or ask the responsible lawyer.
4. Test the first-day matter workflow
Use a realistic low-risk training matter that requires the person’s actual tools and handoffs. Include a permission denial, incorrect recipient, suspicious message, and support need so readiness is measured beyond successful login.
Where to work: Training matter, intake or assignment, document template, email, calendar, deadline, task, time entry, secure share, and support ticket
Verification: The employee completes the workflow, protects client information, handles the exceptions, and reaches support with useful evidence.
Verify daily work, coverage, and support
1. Prepare supervision, leave, and deadline coverage
Define who reviews work, receives alerts, covers calls and matters, reassigns deadlines, approves access, and responds when the employee is unavailable. Ensure active work can be found without using the employee’s password.
Where to work: Supervisor review, responsible-lawyer assignments, shared calendar, task coverage, absence procedure, delegation, and escalation
Verification: Run a one-day absence scenario and transfer a client message, task, document, and deadline to an authorized backup with full context.
2. Manage temporary staff and contractors
Give time-bound named access only to required systems and matters. Record the internal sponsor and supervising lawyer, prohibit credential sharing, define storage and AI use, and schedule removal before access is issued.
Where to work: Engagement approval, sponsor, start and end dates, assigned matters, device, remote access, vendor account, confidentiality, supervision, and data return
Verification: The worker can complete the approved task and loses access automatically or through a confirmed process at the end date without losing work product.
3. Build departure into the onboarding record
Record what must be transferred, preserved, returned, revoked, reviewed, and securely disposed when the person changes role or leaves. Include immediate and planned departures, client continuity, deadlines, personal devices where allowed, and access outside the main identity tenant.
Where to work: Matter responsibility, email and calendar, documents, time and billing, devices, mobile apps, remote tools, physical access, vendors, records, and recovery
Verification: A tabletop departure identifies every active matter, deadline, record, device, credential, integration, physical key, and responsible recipient before access removal.
Test role changes, leave, and secure departure
Use edge-case employees in the pilot, including a partner, remote associate, paralegal with many matters, intake user, billing role, temporary worker, and someone assigned to a restricted matter. Friendly test accounts rarely reveal supervision, mobile, inherited access, calendar, and handoff problems that later reach the help desk.
- Role and matter access: Sign in as the new employee and test assigned, unassigned, restricted, and closed matters. Pass: Required work succeeds and unauthorized matter paths remain blocked.
- Office and remote workflow: Complete the same representative legal task in the office and approved remote environment. Pass: Identity, device, communication, documents, security, and support work without personal tools.
- Confidentiality decision: Present an incorrect recipient, unsafe share, AI prompt, and overheard-call scenario. Pass: The employee identifies the risk and uses the approved alternative or escalation.
- Deadline coverage: Make the employee unavailable and transfer an active matter task and deadline. Pass: The backup receives source, context, authority, reminders, and completion evidence.
- Support path: Create an access, device, suspicious-message, and application issue. Pass: The employee submits useful evidence to the correct path without bypassing controls.
- Departure: Run the documented role-change or departure checklist with a test identity and matter. Pass: Work transfers first, then accounts, sessions, devices, records, and outside access close completely.
Frequently Asked Questions
What information should a law firm collect before onboarding an employee?
Create the role and responsibility record should be handled in approved job description, supervisor, responsible lawyers, department, office or remote status, employment type, and start date. The firm should list the work the person will perform, client and financial information involved, systems required, matters or practice groups, supervision, approvals, physical access, mobile needs, and temporary exceptions, Do not use another employee as the access template without review, then retain a test record showing that the manager, responsible lawyer, HR, and IT can explain why each requested system and privilege supports a real duty.
Why should law firms separate job-role access from matter access?
Separate role access from matter access should be handled in role matrix, practice management, document groups, email spaces, billing, e-discovery, ethical walls, and matter-opening process. The firm should use the role to grant baseline systems, then assign matters from approved teams, Define restricted matters, conflicts, ethical walls, emergency access, temporary coverage, and who can change the team, Avoid giving every attorney or assistant access to every client by default, then retain a test record showing that a pilot account reaches baseline tools and assigned matters but cannot find or open a restricted matter through search, links, groups, or integrations.
How should a new law firm employee's accounts be secured?
Create named identity and recovery should be handled in identity provider, email, practice tools, password manager, MFA, administrator portal, and emergency access. The firm should create an individual account, require MFA, enroll approved recovery, prohibit shared passwords, and separate privileged administration, Use consistent naming and manager records so accounts can be identified during access and departure reviews, then retain a test record showing that the employee signs in and recovers through approved methods, while the manager cannot use or request the employee’s password.
What should be configured on a law firm employee's computer before the first day?
Prepare managed devices and remote work should be handled in device inventory, encryption, endpoint protection, patching, local privilege, VPN or secure access, office network, home workflow, mobile policy, and remote support. The firm should assign and record equipment, enroll management, escrow encryption recovery, deploy approved software, remove routine local administration, and configure secure remote access, Address confidential calls, screens, printing, household sharing, lost devices, and public networks, then retain a test record showing that the employee completes the expected office and remote workflow on managed equipment without personal email, consumer storage, or shared household devices.
Which law firm systems should be tested during onboarding?
Assign practice, document, communication, and billing tools should be handled in practice management, document repository, email, calendar, Teams or collaboration, phone, e-signature, research, time entry, billing, and accounting. The firm should assign the lowest role that supports the person’s tasks, Configure templates, default save locations, signatures, phone routing, calendars, time categories, and integrations, Separate billing and trust functions according to approved responsibilities, then retain a test record showing that the employee can open a test matter, create and locate a document, communicate securely, record time where required, and cannot reach unauthorized financial functions.
What technology training should law firm employees receive?
Deliver role-based confidentiality and security training should be handled in firm policies, client requirements, secure communication, phishing exercises, matter access, remote work, records, devices, AI rules, and incident reporting. The firm should use scenarios from the employee’s work, Have the person identify unsafe recipients, suspicious payment changes, confidential information in an AI prompt, a lost device, an exposed document, a restricted matter, and an urgent deadline, Include how to obtain help without hiding mistakes, then retain a test record showing that the employee completes a scored exercise and demonstrates when to verify, stop, report, use a secure channel, or ask the responsible lawyer.
How can a law firm verify that onboarding is complete?
Test the first-day matter workflow should be handled in training matter, intake or assignment, document template, email, calendar, deadline, task, time entry, secure share, and support ticket. The firm should use a realistic low-risk training matter that requires the person’s actual tools and handoffs, Include a permission denial, incorrect recipient, suspicious message, and support need so readiness is measured beyond successful login, then retain a test record showing that the employee completes the workflow, protects client information, handles the exceptions, and reaches support with useful evidence.
How should law firms prepare technology coverage for employee leave?
Prepare supervision, leave, and deadline coverage should be handled in supervisor review, responsible-lawyer assignments, shared calendar, task coverage, absence procedure, delegation, and escalation. The firm should define who reviews work, receives alerts, covers calls and matters, reassigns deadlines, approves access, and responds when the employee is unavailable, Ensure active work can be found without using the employee’s password, then retain a test record showing that run a one-day absence scenario and transfer a client message, task, document, and deadline to an authorized backup with full context.
How should a law firm control temporary and contractor access?
Manage temporary staff and contractors should be handled in engagement approval, sponsor, start and end dates, assigned matters, device, remote access, vendor account, confidentiality, supervision, and data return. The firm should give time-bound named access only to required systems and matters, Record the internal sponsor and supervising lawyer, prohibit credential sharing, define storage and AI use, and schedule removal before access is issued, then retain a test record showing that the worker can complete the approved task and loses access automatically or through a confirmed process at the end date without losing work product.
Why should a law firm define offboarding during onboarding?
Build departure into the onboarding record should be handled in matter responsibility, email and calendar, documents, time and billing, devices, mobile apps, remote tools, physical access, vendors, records, and recovery. The firm should record what must be transferred, preserved, returned, revoked, reviewed, and securely disposed when the person changes role or leaves, Include immediate and planned departures, client continuity, deadlines, personal devices where allowed, and access outside the main identity tenant, then retain a test record showing that a tabletop departure identifies every active matter, deadline, record, device, credential, integration, physical key, and responsible recipient before access removal.