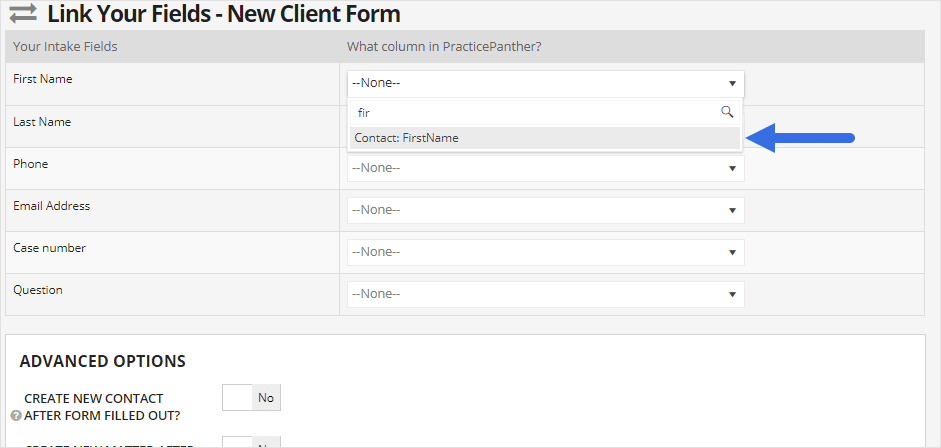
PracticePanther’s published access-level example separates controls for a user’s assigned contacts from controls for all contacts. This older documented layout illustrates the distinction; verify the actual role and test matter, document, billing and report access in your firm’s current system.[4]
Start a law firm’s IT setup with named account ownership, matter-level access, deadline coverage and a tested matter restore. Map one inquiry through conflict review, engagement, matter work, billing and closure before choosing tools. Use the worked matter-access test below to record what succeeds and what stays blocked.
The firm must evaluate controlling law, court rules, client requirements, engagement terms, insurance conditions and current Georgia Rules of Professional Conduct. Technical configuration supports those decisions; it does not replace the responsible lawyer’s judgment.[1]
What a dependable law firm IT operations setup should accomplish
A dependable environment gives each person a named identity, access to only the matters and systems required, secure communication options, managed devices, reliable deadlines, protected billing data, tested recovery, and clear support. The firm can continue active representation when an employee, vendor, device, or cloud service becomes unavailable.
- Intake, conflicts, engagement, matter, document, email, calendar, billing, trust, research, e-filing, signature, and archive systems have named owners.
- Accounts use MFA, least privilege, protected administration, matter-level access, and documented ethical-wall procedures where required.
- Client documents and communications use approved storage, sharing, encryption, retention, and deletion paths.
- Managed office and remote devices receive security, patches, backup, remote support, and loss-response controls.
- Court dates, statutes, hearings, filings, client commitments, and task dependencies have accountable calendaring and backup review.
- Backup and incident plans are tested against matter restoration, business communications, deadlines, billing, and client-service priorities.
Map the complete matter lifecycle and system ownership
1. Map the matter lifecycle before choosing controls
Document each stage, required data, responsible lawyer, supporting staff, approval, system of record, handoff, exception, and retention rule. Include calls and forms that never become matters so prospective-client information is not overlooked.
Where to work: Prospective-client intake, conflict search, engagement, matter opening, legal work, deadlines, billing, closing, and retention procedures
Verification: A new inquiry can be followed from first contact through conflict decision, engagement, open matter, work product, billing, and closure without an undocumented spreadsheet or personal inbox.
2. Create the system and data inventory
Record tenant and account IDs, purpose, data handled, primary and backup owners, privileged users, integrations, billing, support, export, retention, recovery, and contract exit. Identify client data stored outside the intended matter record.
Where to work: Microsoft 365 or Google Workspace, practice management, document management, accounting, trust, e-signature, research, e-discovery, e-filing, phone, website, backup, and vendors
Verification: A backup administrator can locate every production system and explain where a matter’s intake, communications, documents, deadlines, time, costs, and final records live.
3. Establish named identity and protected administration
Use individual accounts, MFA, separate privileged administration, controlled recovery, and role-based groups. Remove routine local administrator rights and shared passwords. Keep at least two authorized recovery paths without giving every administrator access to every matter.
Where to work: Identity provider, email tenant, practice applications, local devices, remote tools, password manager, and administrator accounts
Verification: A backup administrator can recover the tenant while a normal employee cannot enter privileged settings or another user’s matter without authorization.
Protect identity, client information, and remote work
1. Design matter access and ethical-wall procedures
Assign access from the approved matter team and role. Define who can authorize additions, temporary access, emergency access, conflicts restrictions, and ethical walls. Review inherited groups and integrations that can bypass matter-level restrictions.
Check application roles and matter restrictions separately. PracticePanther’s documented access-level example distinguishes actions for assigned contacts from actions for all contacts. That 2019 interface example is useful for discussing scope, but it does not establish an ethical wall or prove the current account’s matter permissions. Test the actual product and configuration.[4]
Where to work: Practice management, document repository, email groups, Teams or shared spaces, time and billing, e-discovery, and matter-opening form
Verification: Test a normal matter, restricted matter, temporary team member, reassignment, and closed matter. Each user sees only the approved information and every exception is attributable.
2. Configure secure client communication and sharing
Choose communication methods according to information sensitivity, client instruction, agreement, and risk. Protect email accounts, provide secure sharing for sensitive files, verify recipients, control public links, and document when additional safeguards are required.
Where to work: Email security, client portal, approved file transfer, encryption, e-signature, voicemail, SMS policy, and client-specific requirements
Verification: Send test messages and files through ordinary and high-sensitivity workflows. Confirm recipient identity, access expiration, revocation, audit evidence, and the client’s ability to use the approved method.
3. Manage endpoints and virtual practice
Enroll firm devices, escrow encryption recovery, deploy endpoint protection, patch supported software, and control remote support. Address household sharing, overheard calls, exposed screens, local printouts, lost devices, public networks, and confidential disposal for remote work.
Where to work: Device management, endpoint protection, encryption, patching, local privilege, remote access, VPN where required, home networks, printing, and physical privacy
Verification: An attorney and staff member complete the same approved matter workflow in the office and remotely without personal email, unmanaged storage, shared computers, or disabled security.
4. Protect calendaring and deadline operations
Define who enters, verifies, modifies, and closes each deadline. Use redundant awareness for critical dates, record the source and responsible lawyer, reconcile notices, and require coverage during leave or departure. Do not rely on one person’s personal calendar.
Where to work: Practice calendar, individual calendars, court and e-filing notices, rules-based date calculation, task management, and backup review
Verification: Test a filing deadline from notice through calculation, attorney review, reminders, completion, evidence, and reassignment when the original owner is unavailable.
Connect deadlines, billing, vendors, backup, and support
1. Separate billing and trust authority
Separate matter work, invoice approval, write-offs, refunds, payment changes, trust activity, reconciliation, and accounting administration according to firm policy. Protect payment changes from email impersonation and document integrations that move client or financial data.[3]
Where to work: Time entry, billing, accounting, payment processing, trust accounting where applicable, bank access, reconciliation, and exports
Verification: Run a controlled invoice and payment workflow, then confirm roles, approvals, records, bank-change verification, and the backup person who can complete a period close.
2. Build backup, restore, and continuity around matters
Identify what each vendor backs up, what remains the firm’s responsibility, recovery time, retention, encryption, immutability, and export limits. Prioritize active matter documents, deadlines, contacts, communications, billing, and critical configuration.
Where to work: Cloud and server backup, Microsoft 365 or Workspace backup where used, practice platform exports, document repositories, accounting, configuration, and recovery plan
Verification: Restore a representative active matter, a deleted message or file, a key configuration, and the information needed to meet a deadline during a primary-system outage.
3. Prepare incident response and communication
Define how staff report suspicious events, who contains systems, preserves evidence, assesses affected client information, restores operations, obtains legal and insurance guidance, and decides notifications. Include ransomware, stolen devices, account takeover, wire fraud, vendor breach, and unavailable cloud systems.
Where to work: Incident plan, security monitoring, cyber-insurance notice, outside counsel decisions, client communication, law-enforcement considerations, vendor contacts, and continuity procedures
Verification: Run a tabletop exercise that begins with a realistic alert and requires the team to protect deadlines, client service, evidence, communication, recovery, and documented decisions.
Test real legal workflows and outage recovery
Work one matter-access test before rollout
Use synthetic records and test identities. These are proposed acceptance checks, not a claim that a named platform or firm has already passed. Record the responsible lawyer’s authorization separately from the technical result.[2]
| Test identity or event | Exercise | Evidence to retain |
|---|---|---|
| Authorized matter team | Open approved matter documents, communications, billing views, shared links and relevant connected applications. | Expected work succeeds; document which role and membership allow it. |
| User outside the matter team | Try the same records through direct links, search, inherited groups and connected applications. | Denied paths stay denied; hiding a menu is insufficient. |
| Reassigned or removed team member | Retest after approved membership changes and session handling. | Former access follows the approved restriction; exceptions have an owner. |
| Isolated matter restore | Restore documents, communications and required supporting records into an isolated location. | Complete, readable records and correct access meet the firm's recovery-time requirement before release. |
For product-specific work, use the PracticePanther intake and matter setup guide to test record destinations, or the Clio permissions and offboarding guide when that is the firm’s platform. ALLMSP’s software support can help implement the firm’s approved workflow.
Pilot the environment with a partner, associate, paralegal, intake employee, billing user, remote worker, and temporary or contract role where used. Include a restricted matter, large document exchange, court deadline, client portal, invoice, lost-device scenario, deleted file, and primary-system outage. A passing setup supports the work and preserves the firm’s decisions and evidence.
- Prospective client to matter: Run a labeled inquiry through intake, conflicts, engagement, opening, assignment, and document creation. Pass: The record moves through approved systems without exposing information to an unauthorized person.
- Remote legal work: Complete a representative client call, document review, filing preparation, and secure share away from the office. Pass: The workflow uses managed identity and devices without confidential workarounds.
- Deadline continuity: Reassign a critical date while the original lawyer and assistant are unavailable. Pass: A responsible backup receives the source, calculation, reminders, task, and evidence of completion.
- Security incident: Run a tabletop account-takeover or ransomware scenario with an active client deadline. Pass: The team contains, preserves evidence, maintains representation, assesses impact, restores, and documents communication decisions.
Frequently Asked Questions
Which workflows should be mapped before a law firm's IT setup?
Map prospective-client intake, conflict review, engagement, matter opening, work, deadlines, billing, closure and retention. Give each handoff an owner and an authoritative record. Walk one fictional inquiry through the whole route, including a prospect the firm declines, so sensitive intake information does not disappear into an unowned mailbox.
What belongs in a law firm technology inventory?
Record each service’s firm-controlled owner, administrator and recovery contact, the client information it holds, its integrations, export options and recovery limits. Include court portals, accounting and personal-device copies as well as the practice platform. A second authorized administrator should be able to locate the records without borrowing an absent employee’s password.
How should administrator access be structured in a law firm?
Use named accounts, MFA, separate administrative identities and documented emergency recovery. Keep ordinary staff out of privileged settings and assign a second authorized recovery owner. Test an administrator’s absence and an employee’s departure separately: recovering the tenant must not automatically give that person unrestricted access to every client matter.
How can a law firm manage matter-level access and ethical walls?
Approve access by matter and role, then test both allowed and denied accounts against documents, search, shared links, communications and connected applications. Retest after reassignment and closure. A contact-visibility setting or a hidden navigation item alone does not establish an ethical wall; the responsible lawyer must approve the restriction and its exceptions.
When should a law firm use a secure client portal instead of ordinary email?
The responsible lawyer should choose safeguards based on sensitivity, client instructions and applicable duties. An approved portal or protected transfer is useful when the firm needs recipient-specific access, expiration or revocation. Ordinary email is not automatically prohibited, but an unrestricted attachment should not be the default for material needing stronger protection.
What controls should a law firm use for secure remote work?
Use firm-approved devices and accounts, supported software, disk encryption, endpoint protection and controlled remote access. Test a real workflow away from the office, including confidential calls and printing. A successful VPN connection is insufficient if the user then saves client documents to a personal account or exposes them on a shared household computer.
How should legal deadlines be protected from a single point of failure?
Assign an entry owner, a separate verification step and backup coverage for each critical date. Keep the source notice, calculation, responsible lawyer, reminders and completion evidence in the approved record. Test reassignment while the original lawyer and assistant are unavailable; reminders in one person’s calendar do not demonstrate continuity.
Which billing and payment permissions should a law firm separate?
Separate preparation, approval, release, reconciliation and system administration according to the firm’s approved accounting and trust procedures. Confirm bank-detail changes through an established independent contact rather than the requesting email. Test a fictional change to ensure one compromised mailbox or administrator cannot silently authorize a payment; technology does not determine the firm’s trust-account obligations.
What should a law firm include in backup and recovery testing?
Restore a representative active matter to an isolated location and check readable documents, communications, relevant dates and access restrictions. Identify records a cloud export or backup omits. Measure the exercise against the firm’s deadline and recovery needs, and retain the result; a successful backup job is not evidence that a complete usable matter can be restored.
What should a law firm incident-response exercise test?
Use a fictional account takeover or ransomware alert during an active deadline. Have named people isolate the problem, preserve evidence, find affected matters and maintain priority work. Record recovery and communication decisions. The firm’s authorized legal and insurance advisers should determine any notification obligations; a technical exercise cannot settle them automatically.