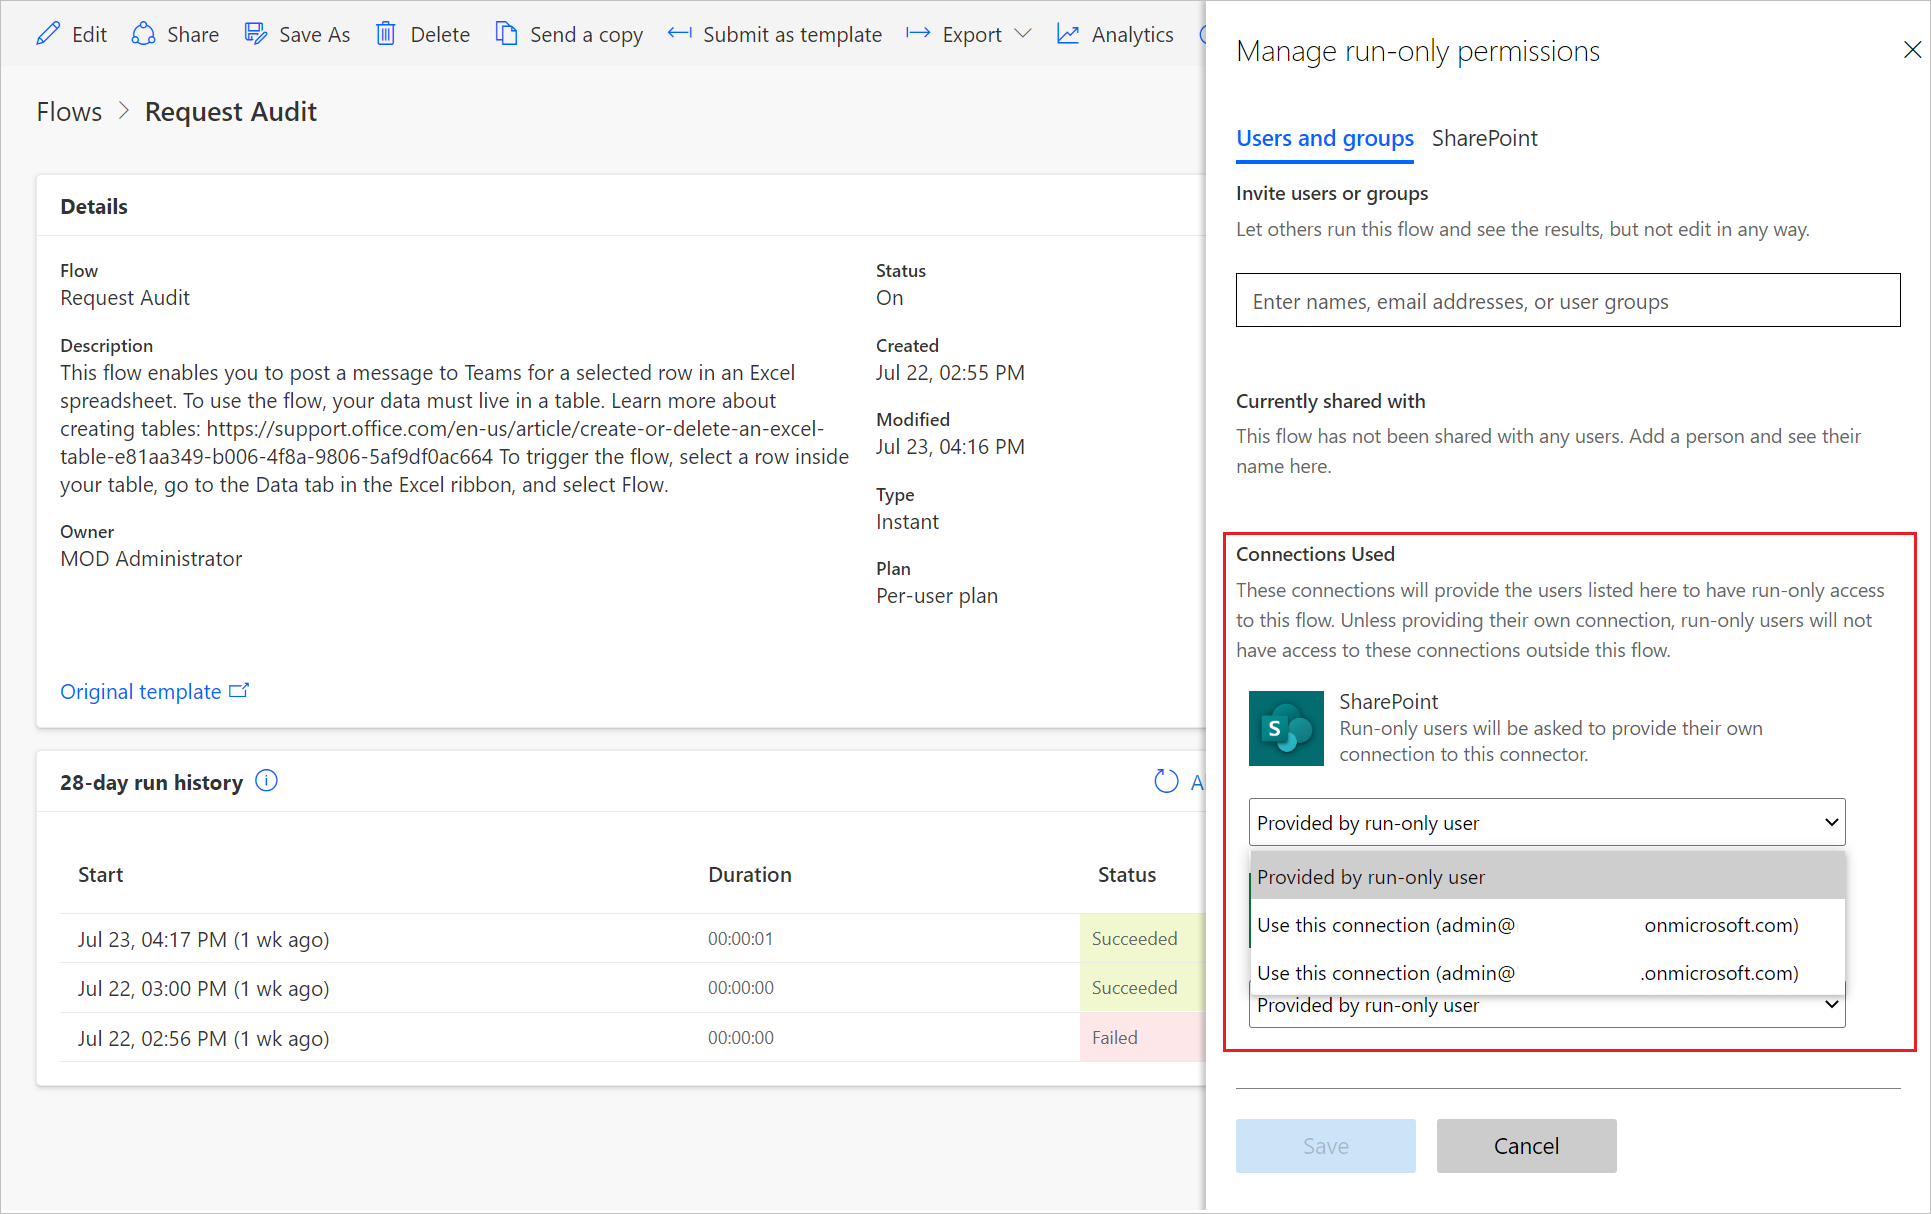
Microsoft’s documented “Request Audit” instant-flow example separates run-only access from the connection used. Before removing a departing account, inspect and replace its connection through the supported process, then safely retest approved ownership and outputs. This screen does not show an ownership transfer or a completed client-workflow test.[6]
CPA and financial firm technology cleanup should remove uncertainty without disrupting client work. Old accounts may own portal folders, scheduled reports, tax applications, automations, bank connections, or recovery methods. Client files may be duplicated across email, desktops, personal storage, and former systems. Begin with dependency evidence and replacement ownership.
Do not delete users, files, applications, integrations, devices, or vendor accounts until required records and ownership are preserved. Coordinate changes around filing, payroll, reporting, audit, close, and client-delivery deadlines. Confirm retention, notification, and regulatory decisions with the responsible firm leadership and advisers.
IRS Publication 4557 addresses taxpayer-data safeguards for tax professionals. Confirm the firm’s actual services and legal scope. The FTC guide explains coverage and risk-based safeguards for entities within its jurisdiction; it is not a universal requirement for every business called a financial firm. [1] [2]
How to choose the right CPA and financial firm IT improvements
A successful cleanup leaves one accountable inventory for systems, data, identities, devices, vendors, integrations, backups, deadlines, and exceptions. Stale access and unsafe copies are removed, client workflows use approved paths, recovery is proven, and support can diagnose problems from reliable evidence.
- Former or seasonal workers, old providers, shared accounts, and unknown service identities retain access.
- Client documents are scattered across mailboxes, desktops, downloads, consumer storage, and inactive portals.
- Tax, accounting, payroll, reporting, or payment workflows depend on one person’s account or undocumented automation.
- Devices are missing from management, encryption, protection, patching, or inventory.
- Backup dashboards report success, but representative client records and configurations have not been restored.
- The written plan and vendor list no longer match actual systems, services, remote work, AI use, or breach contacts.
Find identity, client-data, device, and vendor dependencies
Unknown and excessive privileged access
Diagnosis: Export administrators, recovery contacts, service identities, delegated access, vendor accounts, local administrators, and high-impact roles across every material platform. Match each identity to a current person, system, purpose, last use, and approving owner.
CPA and Financial Firms IT improvement: Add tested company recovery, separate administration, reduce roles, close unknown access, rotate affected credentials, remove standing vendor access, and monitor privileged changes. Preserve application ownership before removal.
Measurement: Track known privileged identities, MFA coverage, stale access removed, emergency recovery tests, vendor-session control, and exceptions with current approval.
Client information outside approved systems
Diagnosis: Search approved locations and sample mailboxes, local folders, downloads, personal cloud accounts, browser storage, scanner destinations, public links, old portals, and removable media for client and taxpayer records.
CPA and Financial Firms IT improvement: Move required records into the approved client repository, preserve context and retention, correct upload and sharing procedures, close public access, remove redundant copies through an approved process, and coach the users who created the workaround.
Measurement: Track unsafe locations found, records migrated, public links closed, recurring exceptions, client workflow completion, and follow-up sample results.
Broad or stale client access
Diagnosis: Compare the client roster and engagement assignments with portal, workpaper, tax, accounting, payroll, collaboration, and archive permissions. Include seasonal, temporary, transferred, inactive, and former workers.
CPA and Financial Firms IT improvement: Assign access from current role and engagement, remove inherited and stale groups, document restricted clients, expire temporary access, and create recurring manager review tied to staffing and client changes.
Measurement: Track mismatches corrected, inactive access removed, restricted-client tests, temporary access expired, review completion, and access-related support tickets.
Correct access, file placement, integrations, and support paths
Unmanaged or unhealthy devices
Diagnosis: Reconcile procurement, user, device-management, endpoint-security, encryption, network, remote-support, and disposal records. Identify unsupported operating systems, missing agents, stale devices, local administrators, and unknown remote tools.
CPA and Financial Firms IT improvement: Enroll, patch, encrypt, protect, replace, quarantine, or retire each device according to risk. Remove unauthorized remote access and local privilege, recover firm data, and document secure disposal and inventory ownership.
Measurement: Track inventory reconciliation, encryption, patch and protection coverage, unsupported devices, local administrators, unknown remote tools, and last-seen exceptions.
Employee-owned integrations and automations
Diagnosis: List APIs, connectors, scheduled exports, email rules, scripts, browser extensions, workflow tools, reporting links, and service accounts. Identify dependencies on employee credentials, personal billing, unmonitored secrets, or unsupported data transfer.
CPA and Financial Firms IT improvement: Transfer ownership to managed identities where supported, reduce scopes, rotate secrets, document inputs and outputs, add failure monitoring, remove abandoned connections, and create a manual continuity path for critical automation.
Microsoft 365 documents blocking access and preserving/handing over data as distinct offboarding steps. Apply the supported sequence for the actual platform. [3]
Measurement: Track known integrations, managed ownership, excessive scopes removed, secrets rotated, failures detected, duplicate processes retired, and continuity tests.
Weak portal and document-request experience
Diagnosis: Test invitation, MFA, upload, folder selection, mobile use, notifications, duplicate files, expiration, client support, and staff retrieval with novice and heavy-use test clients. Review why users fall back to email.
CPA and Financial Firms IT improvement: Simplify instructions and folder structure, correct permissions and notification content, create a supported exception process, train staff, and monitor failed invitations and unsafe fallback behavior.
Measurement: Track invitation success, secure upload completion, support requests, email attachments containing sensitive records, duplicate documents, and time from request to usable file.
Email and financial-change controls do not match workflow
Diagnosis: Review phishing events, forwarding, mailbox rules, delegated access, payment or payroll changes, client verification, after-hours requests, and incidents. Interview the people who approve high-impact changes.
CPA and Financial Firms IT improvement: Strengthen email protection and reporting, require independent verification for sensitive changes, document escalation, remove unsafe forwarding, rehearse common fraud scenarios, and monitor repeated exceptions.
FBI guidance recommends independent verification of payment/account-number changes using a known contact route. [4]
Measurement: Track suspicious messages reported, verification completion, malicious rules found, external forwarding, blocked impersonation, fraud attempts, and time to containment.
Improve monitoring, backup, continuity, and incident evidence
Monitoring creates noise instead of action
Diagnosis: Compare identity, email, endpoint, cloud, application, firewall, backup, and support alerts with tickets and incident records. Identify duplicate noise, blind spots, missed ownership, and recurring warnings that never receive root-cause correction.
CPA and Financial Firms IT improvement: Route meaningful events to accountable queues, define severity and timing, tune only with evidence, automate safe context collection, create after-hours escalation, and review repeated alerts for permanent correction.
Measurement: Track critical coverage, alert-to-ticket linkage, acknowledgment and containment time, false positives, recurring events, missed escalations, and verified corrective work.
Backup success has not been proven
Diagnosis: Map client repositories, tax and accounting applications, payroll, email, configurations, integrations, local data, and vendor exports to backup coverage. Inspect job history, immutability, retention, permissions, and recent restore evidence.
CPA and Financial Firms IT improvement: Add missing scope, isolate administration, correct failures, protect exports, run representative clean restores, document timing and dependencies, and repeat tests around peak deadlines and major platform changes.
CISA recommends protected backups and regular recovery testing, including attention to cloud responsibility. [5]
Measurement: Track protected critical data, successful clean restores, restore time, recovery-point gap, failed jobs corrected, application-export currency, and unresolved dependencies.
Written plans and support procedures are stale
Diagnosis: Compare the written information security plan, incident plan, continuity procedures, vendor list, user guides, contact tree, and escalation paths with actual services, systems, remote work, AI tools, staff, and recent tickets.
CPA and Financial Firms IT improvement: Update documents from verified current state, assign owners and review dates, connect procedures to ticket templates and exercises, train affected roles, and archive prior approved versions.
Measurement: Track current documents, overdue reviews, exercise findings closed, staff acknowledgment, correct contact tests, recurring support errors, and policy exceptions.
Measure security and operational visibility after cleanup
Review the cleanup with service leaders, security, operations, and the people who perform daily client work. Every change should name the dependency, affected service and deadline, retained evidence, replacement owner, user communication, verification, and follow-up date.
- Known identity and ownership: Percentage of users, administrators, recovery methods, service identities, integrations, devices, and vendors mapped to a current owner and purpose.
- Client-access accuracy: Sampled client and engagement permissions that match current role, assignment, restriction, temporary approval, and inactive status.
- Approved data placement: Client records using the approved portal and repository, with unsafe copies, public links, and undocumented exports corrected.
- Endpoint health: Managed, encrypted, protected, patched, supported devices without unnecessary local administration or unknown remote access.
- Detection and response: Critical events reaching an accountable responder with useful context, containment, evidence, and corrective follow-through.
- Recovery confidence: Representative client records, messages, application exports, and configurations restored within documented deadline needs.
A cleanup wave that respects the next filing deadline
Hypothetical sequencing example. The service owner approves the actual timing and record decisions.
On a narrow screen, scroll horizontally to read every table column.
| Finding | Safe first action | What must pass before closure |
|---|---|---|
| Seasonal worker still has client-portal access | Compare current engagements, revoke unneeded access and preserve relevant activity records. | A current preparer can still reach the client record; the seasonal account cannot. |
| Scheduled report uses a former employee’s credentials | Move to the platform’s supported firm-controlled connection and run a test. | The report reconciles with the source and a failed run reaches the new owner. |
| Scanner sends tax documents into a personal mailbox | Correct the approved scan/upload route using test documents. | The intended client folder receives the file and no personal copy is created. |
Frequently Asked Questions
How should a financial firm clean up unknown administrator access?
Identify who owns each privileged account and what it still controls before disabling it. Establish firm-controlled recovery, then transfer necessary application or automation ownership and remove excess roles. Review vendor and service identities as well as named employees. An unexplained administrator needs investigation; renaming it or moving it into an inventory does not prove that the access is safe.
What should a CPA firm do when client files are scattered across email and desktops?
Choose the approved client repository and move a sample engagement with its folder context and required history. Show staff and a test client how to upload and find the right records there. Correct the scanner destination or portal problem that caused the email workaround. Delete old copies only after the firm’s retention and preservation decisions are satisfied.
How can an accounting firm clean up stale client permissions?
Compare current engagement assignments with actual access, including seasonal staff, transferred employees, inherited groups and shared links. Test a permitted person and someone who should be excluded against the same sample client. Remove the source of excess access and repeat both tests. A clean user list alone can miss a broad group or a still-working public link.
What is the safest way to clean up an accounting firm's device inventory?
Reconcile purchasing, assigned users and live device-management/security records before retiring anything. Investigate missing or stale devices, recover required firm data and confirm encryption, patching and supported software. Use the approved lost-device or disposal process when appropriate. Do not wipe an apparently unused computer until its data, ownership and any preservation requirement have been checked.
How should a CPA firm clean up employee-owned automations?
Find the automation’s owner, credentials, data flows and failure alerts, then create a supported firm-controlled connection with a backup owner. Test one representative input through to the accounting or reporting destination before retiring the old connection. Preserve configuration and reconciliation evidence. Where managed identities are unsupported, document the supported service-account arrangement and secret-rotation process instead of inventing an unsupported substitute.
Supporting sources: [3]
How can a firm improve client portal adoption without weakening security?
Fix the point where a novice client gets stuck: invitation, MFA, upload location, file size or confirmation. Test the full journey on a phone with non-client sample files. Provide clear support and a secure exception route instead of allowing sensitive attachments into ordinary email. Success means staff can retrieve the correct file from the intended client area without widening access.
How can a financial firm improve payment-change verification?
Require an independent callback or in-person verification before changing payment, payroll or banking details. Use an established number or a separately verified contact, not the number in the change request. Record the verifier, approved change and second approval where required by the firm’s controls. A familiar email thread or an MFA-protected mailbox does not by itself prove that the request is legitimate.
Supporting sources: [4]
How can a CPA firm make security monitoring more useful?
Select a few important events and follow each from the source system into the assigned ticket, responder and corrective action. For example, a suspicious sign-in should reach someone who can investigate it; a failed backup should reach someone who can restore coverage. Reduce duplicate alerts only after confirming what evidence and escalation would be lost.
How should CPA firms prove that cloud and application backups work?
Restore representative client records and the application or export needed to use them, using current recovery credentials. Test a changed or deleted record as well as a recent intact one. Record completeness, elapsed recovery time and the gap between the recovery point and current work. Repeat the exercise after material platform changes and around critical delivery workflows.
Supporting sources: [5]
When should a financial firm update its written security and continuity plans?
Update the plans when services, systems, providers, risks, staffing or incident findings change, and on the firm’s scheduled review cycle. Professional tax preparers should use current IRS guidance; FTC Safeguards Rule duties depend on covered activities and jurisdiction. Verify the actual scope before assigning a regulatory requirement to every CPA or financial firm.
Choose the next step
- Audit Financial-Firm Access, Devices, Data, and Recovery — Test the access, device and recovery evidence after the cleanup wave.
- Fix Accounting-Firm Onboarding and Offboarding Before Peak Season — Repair the staff-change process when seasonal or departed users keep creating dependencies.
Sources
- IRS Publication 4557: Safeguarding Taxpayer Data. Tax-professional taxpayer-data safeguards, written security plan, access and recovery guidance; not universal securities-regulator requirements. ↩
- FTC Safeguards Rule: What Your Business Needs to Know. Rule applies by covered activity/jurisdiction; written risk-based program, access controls, provider oversight and periodic evaluation for covered entities, with specific exceptions. ↩
- Microsoft 365: Remove a former employee and secure data. Block sign-in, preserve required mailbox and OneDrive data, arrange continuing access and handle licensing/deletion as distinct steps; Microsoft 365 example only. ↩
- FBI: Business Email Compromise. Independently verify payment and account-number changes via known contact routes instead of replying to the changed message. ↩
- CISA: #StopRansomware Guide. Maintain protected offline/encrypted backups, regularly test recovery, and understand cloud responsibility; no universal 14–30 day retention rule. ↩
- Microsoft Learn: Share a cloud flow Official guidance distinguishes flow owners, run-only access and connection identity, including failure risks when a departed user’s connection remains embedded. The image is a vendor example, not a completed client transfer. ↩