Device management connects every business laptop, desktop, mobile device, kiosk, shared workstation, and remote endpoint to an accountable lifecycle. The objective is not simply to install an agent. A dependable program proves what the company owns, who uses it, which controls apply, whether the device is healthy, how support reaches it, and what happens when it is replaced, lost, reassigned, or retired.
Do not enroll production devices by applying broad untested policies to every employee at once. Capture the current encryption, local administrator, security, network, application, certificate, update, and recovery state. Test representative users, device models, remote connections, accessibility needs, line-of-business applications, and shared devices before expanding a policy.
What a dependable device management setup should accomplish
A dependable device-management program maintains a current inventory, uses company-controlled enrollment, applies role-based security and configuration, monitors failures, deploys updates and applications safely, supports users with authorized remote access, preserves data and recovery, and records every ownership change through secure disposition.
- Each device has a unique asset record, assigned owner, location, hardware identity, operating system, warranty, business role, and management status.
- Enrollment and identity tie the endpoint to a company-controlled tenant and named user or documented shared-device purpose.
- Encryption, endpoint protection, firewall, screen lock, local administration, recovery keys, and compliance requirements are verified.
- Operating-system, driver, firmware, and application updates use tested rings, maintenance windows, restart communication, and rollback evidence.
- Monitoring, alert routing, backup, remote support, software, peripherals, and user workflows are tested on office and remote networks.
- Lost, departing, reassigned, replaced, and retired devices follow documented access, data, wipe, recovery, and disposition procedures.
Create the authoritative endpoint inventory and ownership model
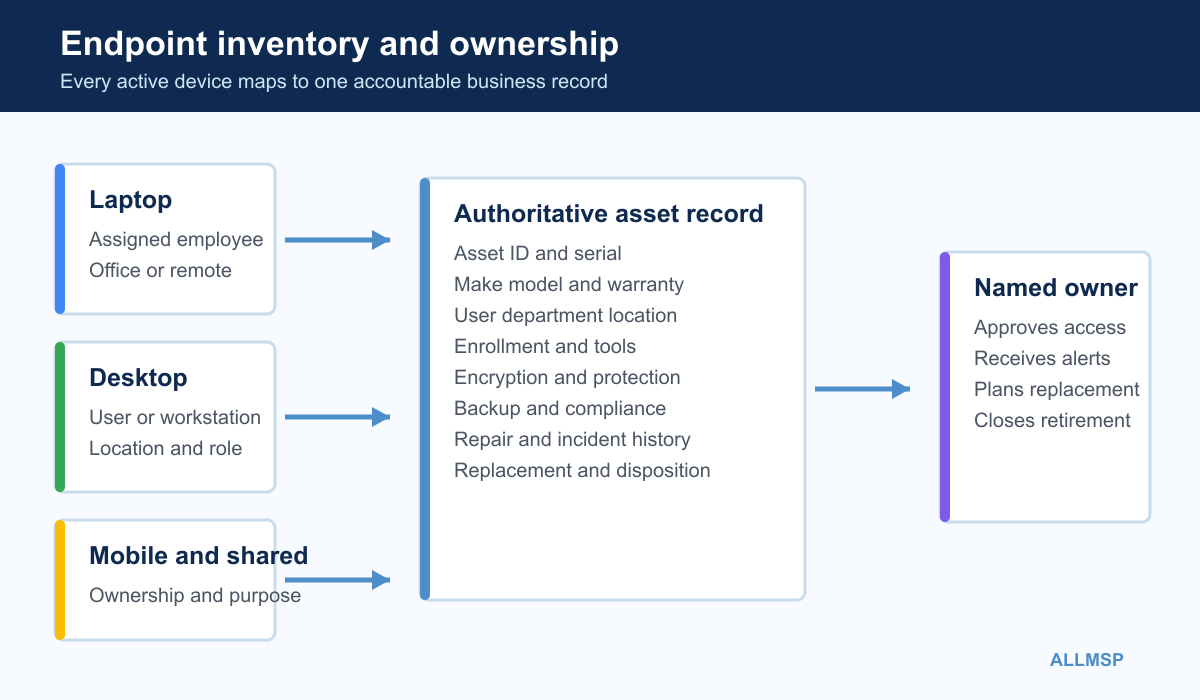
1. Define device classes and lifecycle owners
Define laptops, desktops, workstations, phones, tablets, kiosks, meeting-room systems, shared devices, servers where applicable, personally owned endpoints, loaners, and lab equipment. Assign who approves purchase, enrollment, configuration, data access, repair, reassignment, wipe, and disposition for each class.
Where to work: Asset policy, HR process, purchasing, help desk, security, finance, department interviews, and legal or compliance requirements
Verification: A new, lost, shared, personally owned, reassigned, and retiring device scenario each has a named decision owner and documented path.
2. Build and reconcile the asset inventory
Record asset tag, serial number, hardware ID, make, model, processor, memory, storage, operating system, assigned user, department, location, warranty, purchase date, business role, management tools, encryption, security, backup, and expected replacement date. Mark unknown and duplicate records for investigation.
Where to work: Procurement records, management console, identity directory, endpoint security, backup, RMM, warranty portals, network observations, and physical inventory
Verification: Sample devices can be matched physically to one asset record and every active management console device maps to an authorized user or shared purpose.
3. Establish company-controlled enrollment
Connect devices to the company tenant through supported automated enrollment where possible. Define who can enroll, which device identifiers are accepted, whether personally owned devices are permitted, enrollment limits, naming, ownership type, and the process for devices acquired outside standard purchasing.
Where to work: Microsoft Intune, Apple Business Manager or supported management service, Android Enterprise, RMM, identity directory, and approved provisioning workflow
Verification: A factory-reset pilot device reaches the correct tenant, user, ownership type, configuration, applications, security, and support tools without a technician’s personal account.
Enroll devices and enforce the secure baseline
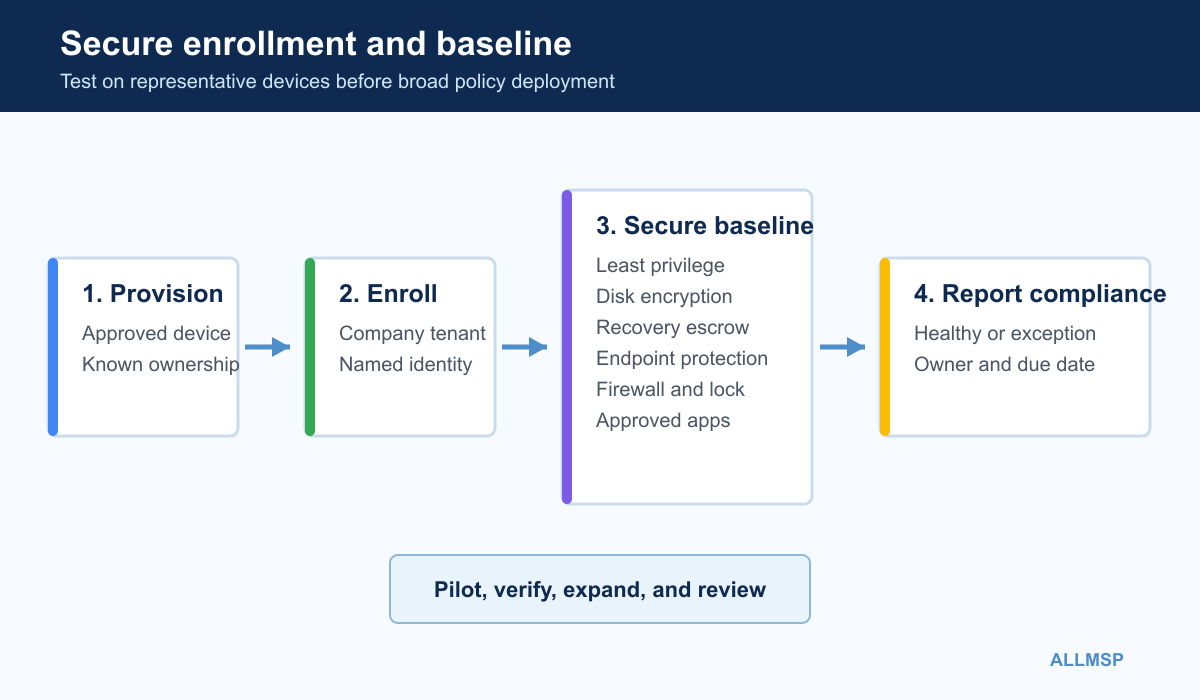
1. Design groups, profiles, and policy rings
Group devices by operating system, ownership, role, location, risk, and deployment stage. Keep policy purposes clear and avoid broad overlapping profiles. Use pilot, early, standard, and exception rings with named owners and expiration dates for exclusions.
Where to work: Management platform groups, identity groups, dynamic rules, configuration profiles, compliance policies, update rings, application assignments, and exclusions
Verification: A representative device receives one explainable result for each important setting and an exception does not silently remove unrelated protection.
2. Apply identity, privilege, and access controls
Tie access to named identities and compliant devices where appropriate. Remove routine local administrator rights, provide controlled elevation for approved work, protect administrator accounts, and document break-glass access. Configure certificates, VPN, Wi-Fi, and single sign-on without embedding shared credentials.
Where to work: Identity provider, device join or registration, local users and groups, MFA, conditional access, certificate or Wi-Fi profiles, and administrator solution
Verification: Normal users complete required work without permanent administrator rights, while support can perform an approved elevation and the event is attributable.
3. Enforce encryption, endpoint protection, and firewall
Enable supported full-disk encryption, escrow recoverable keys to a company-controlled system, deploy endpoint protection, enable tamper protection where supported, configure firewall rules, and define compliance actions. Test legitimate business applications before blocking broadly.
Where to work: Device-management security profiles, BitLocker or FileVault, recovery-key escrow, endpoint security console, firewall policy, and compliance reporting
Verification: A backup administrator can retrieve a test recovery key, security agents report healthy, firewall profiles apply, and a noncompliant pilot follows the documented response.
4. Create a tested patch and firmware process
Separate security urgency from ordinary feature updates, test representative models and applications, schedule installation and restart expectations, monitor failures, and keep exceptions temporary. Include browsers, collaboration tools, firmware, drivers, and common third-party applications rather than Windows updates alone.
Where to work: Operating-system update rings, RMM patch policy, vendor firmware and driver tools, application patching, maintenance calendar, and rollback procedure
Verification: Pilot devices install the approved update, restart successfully, run critical workflows, report status, and demonstrate a documented rollback or recovery path.
Operate updates, applications, monitoring, and support
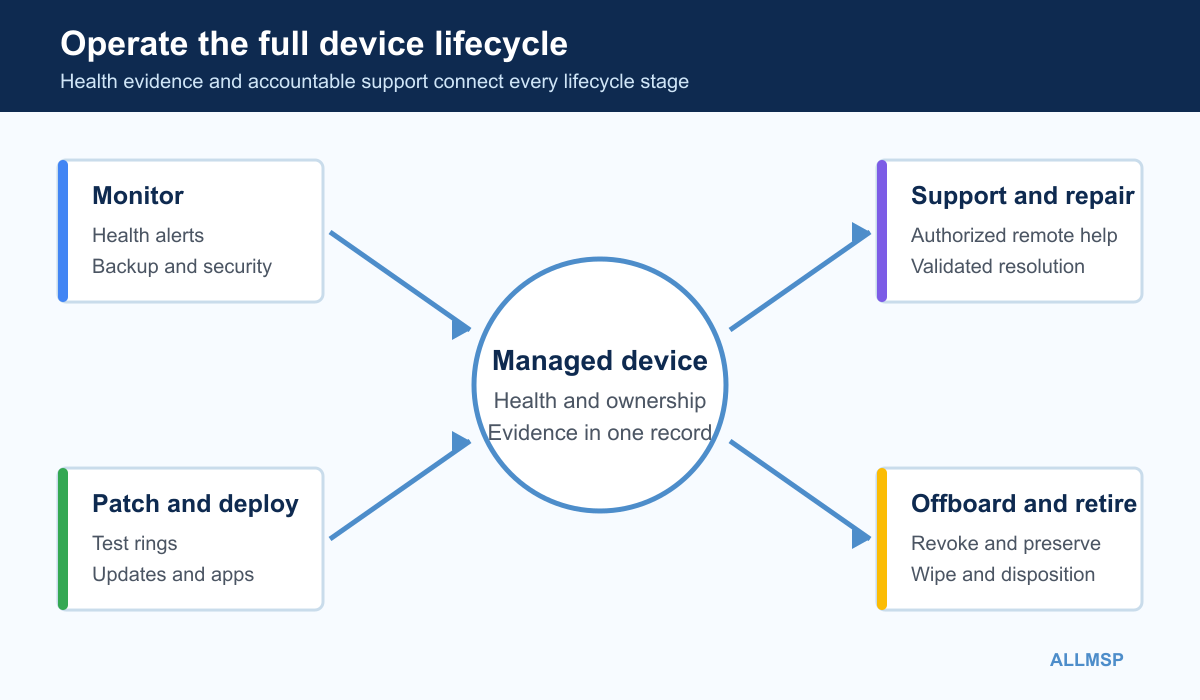
1. Deploy and remove applications predictably
Define required, available, prohibited, and exception software by role. Package versions, prerequisites, settings, license ownership, update source, detection, repair, and removal. Avoid scripts that expose secrets or succeed without verifying the final application state.
Where to work: Managed application catalog, packaging process, license assignment, dependencies, security review, deployment rings, detection rules, and uninstall workflow
Verification: A new pilot user receives required software, an unauthorized or obsolete application is removed safely, and detection reports the actual installed version.
2. Configure monitoring, backup, and authorized remote support
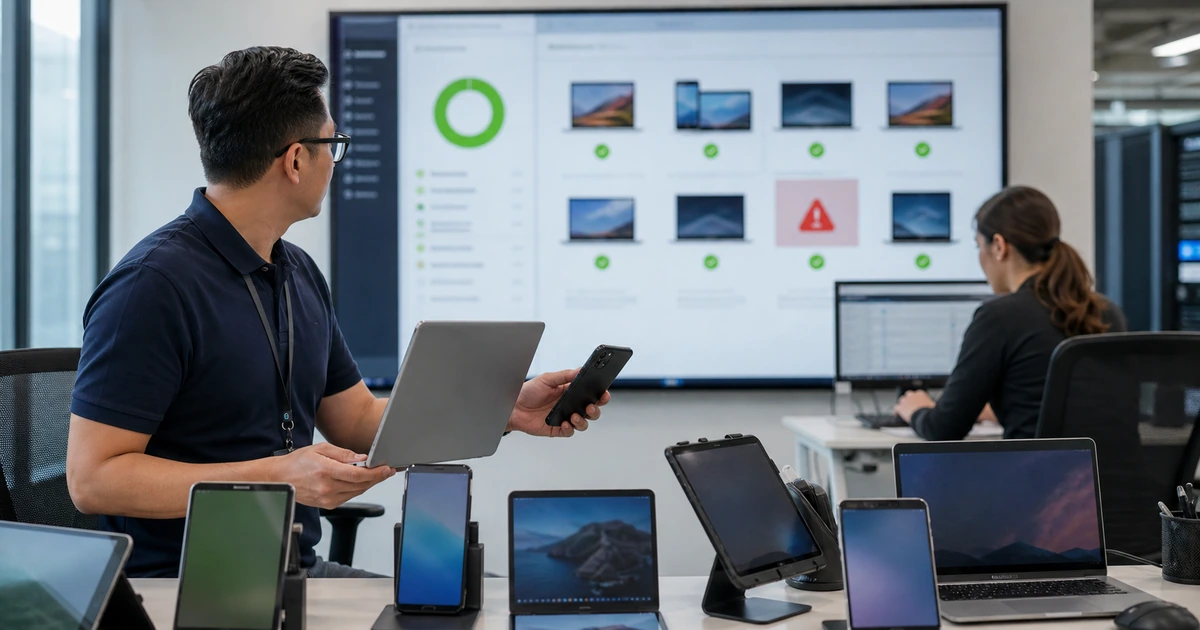
Monitor actionable health such as storage, backup, endpoint protection, update failure, repeated crashes, battery, critical services, and offline status. Route alerts to named owners with severity and suppression rules. Require user notice or consent for remote support according to policy and log technician access.
Where to work: RMM, endpoint security, backup console, alert rules, remote-support permissions, ticketing, monitoring thresholds, and user-notification settings
Verification: Trigger approved test alerts, restore a representative file, open a consented remote session, and confirm the ticket contains the device, technician, time, action, and outcome.
3. Build onboarding, incident, and offboarding runbooks
Document staging, assignment, user acceptance, lost-device response, compromise isolation, repair, loaner issuance, reassignment, employee departure, remote wipe, data preservation, license recovery, secure erase, recycling, and certificate of destruction where required. Include ownership and approval at each handoff.
Where to work: HR system, help desk, asset register, identity, device management, endpoint security, backup, remote support, purchasing, and disposition provider
Verification: Run tabletop and pilot tests for a new remote employee, lost laptop, suspected compromise, urgent loaner, departing user, and retired encrypted device. Every system and record closes correctly.
Test onboarding, daily use, incident response, and offboarding
Pilot with users who expose real edge cases. Include a heavy application user, remote employee, mobile user, shared-device workflow, limited-bandwidth connection, unusual peripheral, accessibility need, and user with historical workarounds. Track both technical results and whether the employee can complete normal work without bypassing controls.
- Zero-touch or guided enrollment: Reset and provision a representative supported device using the documented company workflow. Pass: The device reaches the correct tenant, owner, policies, applications, security, inventory, and support tools.
- Security and recovery: Verify encryption, endpoint protection, firewall, local privilege, compliance, and a test recovery-key retrieval. Pass: Controls report healthy and authorized recovery works without storing secrets in an unsafe location.
- Update and restart: Deploy an approved operating-system, application, driver, or firmware update through the pilot ring. Pass: Installation, restart, business applications, peripherals, monitoring, and rollback evidence pass.
- Remote employee workflow: Use the device away from the office on a representative network with VPN, cloud apps, updates, support, and backup. Pass: The employee works securely and management remains healthy without an office-only dependency.
- Lost or compromised device: Run a tabletop exercise for a lost endpoint with sensitive access or a suspected security incident. Pass: The team can locate the asset record, revoke access, isolate or wipe as appropriate, preserve evidence, notify owners, and issue a replacement.
- Offboarding and retirement: Process a pilot departure and a device marked for disposal through every system. Pass: Access, data, licenses, management records, recovery, wipe, physical custody, and disposition evidence are complete.
Frequently Asked Questions
Which device types should a business device-management program cover?
Define device classes and lifecycle owners should be handled in asset policy, HR process, purchasing, help desk, security, finance, department interviews, and legal or compliance requirements. The firm should define laptops, desktops, workstations, phones, tablets, kiosks, meeting-room systems, shared devices, servers where applicable, personally owned endpoints, loaners, and lab equipment, Assign who approves purchase, enrollment, configuration, data access, repair, reassignment, wipe, and disposition for each class, then retain a test record showing that a new, lost, shared, personally owned, reassigned, and retiring device scenario each has a named decision owner and documented path.
What information belongs in a business device inventory?
Build and reconcile the asset inventory should be handled in procurement records, management console, identity directory, endpoint security, backup, RMM, warranty portals, network observations, and physical inventory. The firm should record asset tag, serial number, hardware ID, make, model, processor, memory, storage, operating system, assigned user, department, location, warranty, purchase date, business role, management tools, encryption, security, backup, and expected replacement date, Mark unknown and duplicate records for investigation, then retain a test record showing that sample devices can be matched physically to one asset record and every active management console device maps to an authorized user or shared purpose.
Why should device enrollment use company-controlled accounts?
Establish company-controlled enrollment should be handled in microsoft Intune, Apple Business Manager or supported management service, Android Enterprise, RMM, identity directory, and approved provisioning workflow. The firm should connect devices to the company tenant through supported automated enrollment where possible, Define who can enroll, which device identifiers are accepted, whether personally owned devices are permitted, enrollment limits, naming, ownership type, and the process for devices acquired outside standard purchasing, then retain a test record showing that a factory-reset pilot device reaches the correct tenant, user, ownership type, configuration, applications, security, and support tools without a technician’s personal account.
How should device groups and policy rings be designed?
Design groups, profiles, and policy rings should be handled in management platform groups, identity groups, dynamic rules, configuration profiles, compliance policies, update rings, application assignments, and exclusions. The firm should group devices by operating system, ownership, role, location, risk, and deployment stage, Keep policy purposes clear and avoid broad overlapping profiles, Use pilot, early, standard, and exception rings with named owners and expiration dates for exclusions, then retain a test record showing that a representative device receives one explainable result for each important setting and an exception does not silently remove unrelated protection.
Should employees have local administrator rights on managed computers?
Apply identity, privilege, and access controls should be handled in identity provider, device join or registration, local users and groups, MFA, conditional access, certificate or Wi-Fi profiles, and administrator solution. The firm should tie access to named identities and compliant devices where appropriate, Remove routine local administrator rights, provide controlled elevation for approved work, protect administrator accounts, and document break-glass access, Configure certificates, VPN, Wi-Fi, and single sign-on without embedding shared credentials, then retain a test record showing that normal users complete required work without permanent administrator rights, while support can perform an approved elevation and the event is attributable.
How should encryption recovery keys be managed for business devices?
Enforce encryption, endpoint protection, and firewall should be handled in device-management security profiles, BitLocker or FileVault, recovery-key escrow, endpoint security console, firewall policy, and compliance reporting. The firm should enable supported full-disk encryption, escrow recoverable keys to a company-controlled system, deploy endpoint protection, enable tamper protection where supported, configure firewall rules, and define compliance actions, Test legitimate business applications before blocking broadly, then retain a test record showing that a backup administrator can retrieve a test recovery key, security agents report healthy, firewall profiles apply, and a noncompliant pilot follows the documented response.
What should a business patch-management process include?
Create a tested patch and firmware process should be handled in operating-system update rings, RMM patch policy, vendor firmware and driver tools, application patching, maintenance calendar, and rollback procedure. The firm should separate security urgency from ordinary feature updates, test representative models and applications, schedule installation and restart expectations, monitor failures, and keep exceptions temporary, Include browsers, collaboration tools, firmware, drivers, and common third-party applications rather than Windows updates alone, then retain a test record showing that pilot devices install the approved update, restart successfully, run critical workflows, report status, and demonstrate a documented rollback or recovery path.
How should business applications be deployed through device management?
Deploy and remove applications predictably should be handled in managed application catalog, packaging process, license assignment, dependencies, security review, deployment rings, detection rules, and uninstall workflow. The firm should define required, available, prohibited, and exception software by role, Package versions, prerequisites, settings, license ownership, update source, detection, repair, and removal, Avoid scripts that expose secrets or succeed without verifying the final application state, then retain a test record showing that a new pilot user receives required software, an unauthorized or obsolete application is removed safely, and detection reports the actual installed version.
What should be monitored on business laptops and workstations?
Configure monitoring, backup, and authorized remote support should be handled in rMM, endpoint security, backup console, alert rules, remote-support permissions, ticketing, monitoring thresholds, and user-notification settings. The firm should monitor actionable health such as storage, backup, endpoint protection, update failure, repeated crashes, battery, critical services, and offline status, Route alerts to named owners with severity and suppression rules, Require user notice or consent for remote support according to policy and log technician access, then retain a test record showing that trigger approved test alerts, restore a representative file, open a consented remote session, and confirm the ticket contains the device, technician, time, action, and outcome.
What should happen to managed devices when an employee leaves?
Build onboarding, incident, and offboarding runbooks should be handled in hR system, help desk, asset register, identity, device management, endpoint security, backup, remote support, purchasing, and disposition provider. The firm should document staging, assignment, user acceptance, lost-device response, compromise isolation, repair, loaner issuance, reassignment, employee departure, remote wipe, data preservation, license recovery, secure erase, recycling, and certificate of destruction where required, Include ownership and approval at each handoff, then retain a test record showing that run tabletop and pilot tests for a new remote employee, lost laptop, suspected compromise, urgent loaner, departing user, and retired encrypted device, Every system and record closes correctly.