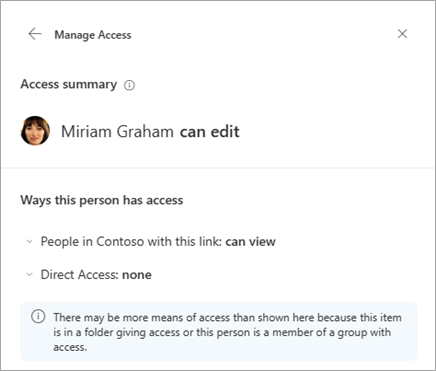
Microsoft’s SharePoint example warns that this panel may omit access inherited from a parent folder or group. Treat the displayed link as one path to investigate. Test an authorized matter-team member and an unrelated user against the same restricted record; the panel alone does not prove isolation.[5]
Law firm IT cleanup should reveal hidden dependencies before removing them. Client files may be scattered across email, personal drives, practice platforms, local desktops, e-discovery systems, and old vendor portals. Accounts may remain active because they own a calendar, automation, billing export, verification token, or restricted matter. The cleanup begins with evidence, not deletion.
Add and test replacement ownership before removing a lawyer, employee, consultant, vendor, integration, verification method, or service account. Preserve records according to the firm’s legal and ethical decisions. A cleanup can interrupt representation or destroy evidence when it treats every old item as disposable.
Use the current official Georgia rules for attorney review of confidentiality and communications; the firm determines their application. [1]
How to choose the right law firm IT operations improvements
A useful cleanup leaves one accountable record for systems, users, matters, devices, integrations, backups, deadlines, billing, and exceptions. Stale access is removed, restricted matters are enforced, personal workarounds are migrated, recovery is tested, and every remaining dependency has a current owner.
- Former employees, outside providers, shared accounts, or unknown service identities remain privileged.
- Matter documents and communications exist in personal mailboxes, local folders, consumer sharing tools, or abandoned portals.
- Restricted matters rely on manual instructions while inherited groups and search can still expose content.
- Critical deadlines, billing exports, or automations depend on one employee’s account or undocumented spreadsheet.
- Backup reports show success, but no one has restored a representative matter or cloud-service record.
- Generative AI, browser extensions, mobile apps, and new cloud tools are used without a reviewed client-data decision.
Find account, matter, device, and vendor dependencies
Unknown and excessive privileged access
Diagnosis: Export administrators, privileged roles, manager accounts, service identities, recovery contacts, and local administrators across email, practice management, documents, billing, backup, remote support, and security. Match each identity to a current person or system.
Law Firms IT improvement: Add tested internal recovery, separate administration, reduce roles, remove shared access, rotate exposed credentials, and investigate unknown activity before revocation.
Measurement: Track privileged identities with owners, MFA coverage, stale access removed, emergency-access tests, and unexplained activity closed.
Matter access no longer matches the team
Diagnosis: Compare active and closed matter teams with document groups, practice roles, email spaces, e-discovery, billing, shared links, and inherited access. Include lateral moves, leave, temporary staff, and ethical walls.
Law Firms IT improvement: Correct the approved team at the source, remove inherited access paths, expire temporary exceptions, and verify restricted matters with normal and blocked test accounts.
Measurement: Track access mismatches, restricted-matter test results, exceptions past due, and time to remove access after a role change.
Client information stored outside the matter record
Diagnosis: Search approved inventory and user interviews for personal drives, local desktops, downloads, consumer cloud storage, email-only files, removable media, chat, and abandoned portals. Identify the authoritative copy and retention decision.
Law Firms IT improvement: Move records through a controlled process, preserve metadata and required history, restrict the destination, update links and procedures, and securely dispose of unneeded copies after approval.
Measurement: Track unmanaged locations closed, files migrated, duplicate storage reduced, access exceptions, and user success finding the authoritative record.
Correct access, file placement, deadlines, and billing control
Calendars and deadlines depend on one person
Diagnosis: Review critical dates, source notices, rules calculations, reminder patterns, shared visibility, leave coverage, reassignment, and completion evidence. Identify personal calendars and tasks with no responsible backup.
Law Firms IT improvement: Move deadlines into the governed practice process, add accountable review and backup coverage, reconcile notices, and test reassignment during absence.
Measurement: Track critical dates with source and owner, unacknowledged reminders, late tasks, coverage tests, and deadline-related incidents.
Billing and payment access is too broad
Diagnosis: Map time entry, invoice approval, write-offs, refunds, payment changes, trust functions where applicable, bank access, reconciliation, exports, and vendor support. Identify shared credentials and one-person control.
Law Firms IT improvement: Separate incompatible duties, require independent verification for payment changes, narrow data exports, add backup coverage, and review activity after role changes.
FBI guidance recommends independent verification of payment/account-number changes using a known contact route. [4]
Measurement: Track privileged billing roles, approval exceptions, payment-change verification, reconciliation completion, and unresolved access conflicts.
Departed users still own records and automation
Diagnosis: Inspect mail, calendars, forms, workflows, integrations, shared links, e-signature, reports, service accounts, mobile devices, and vendor portals for former-employee ownership or credentials.
Law Firms IT improvement: Transfer matter responsibility and durable assets, replace personal connections, revoke sessions and recovery, preserve required records, and retest each automation under company control.
Microsoft 365 documents blocking access and preserving/handing over data as distinct offboarding steps. Apply the supported sequence for the actual platform. [2]
Measurement: Track departed-user dependencies, transfer completion, revoked sessions, automations retested, and exceptions with deadlines.
Unreviewed AI and browser tools
Diagnosis: Inventory generative AI, transcription, summarization, research, drafting, browser extensions, meeting tools, and mobile applications. Record users, data entered, terms, training use, retention, sharing, and client or matter restrictions.
Law Firms IT improvement: Apply the firm’s current ethical and legal decision, block or limit unsafe tools, provide an approved workflow, require qualified review, and train users on confidential information and verification.
Measurement: Track approved-tool use, policy exceptions, confidential-data incidents, output-review failures, and employees completing role-based tests.
Review AI, integrations, backup, and incident readiness
Backup success is assumed instead of tested
Diagnosis: Map matter, document, email, practice, accounting, configuration, cloud, and endpoint data to actual backup and export coverage. Review alerts, retention, immutability, credentials, and last restore evidence.
Law Firms IT improvement: Close coverage gaps, separate backup administration, protect credentials, create matter-based restore tests, and document recovery priorities for active representation.
CISA recommends protected backups and regular recovery testing, including attention to cloud responsibility. [3]
Measurement: Track protected systems, restore success, recovery time, recovery point, failed jobs, and unresolved records that cannot be exported.
Vendor access and exit plans are unclear
Diagnosis: Review technology, legal software, marketing, e-discovery, accounting, payment, phone, security, and support providers for accounts, data, subcontractors, integrations, billing, retention, export, notice, and termination.
Law Firms IT improvement: Document business ownership, narrow vendor access, correct recovery contacts, preserve configurations, define export and deletion evidence, and test the exit path before renewal or transition.
Measurement: Track vendors with owners, access reviews, exit documentation, company-controlled accounts, export tests, and overdue terminations.
Incident response is not connected to client work
Diagnosis: Review plans for account takeover, ransomware, lost devices, wire fraud, vendor breach, unavailable practice systems, and compromised client information. Check deadlines, client communication, insurance, evidence, and restoration roles.
Law Firms IT improvement: Run a realistic exercise with an active matter and deadline, update technical and legal decision paths, create offline contacts, and close each observed failure.
Measurement: Track exercise actions closed, detection and containment time, deadline continuity, restore result, communication decisions, and repeated gaps.
Measure continuity after cleanup
Complete cleanup in controlled waves and preserve a change record. Recheck a normal matter, restricted matter, remote user, billing workflow, deadline, backup restore, and provider-departure scenario after changes. The environment is cleaner only when daily representation remains dependable and the firm can explain every retained exception.
- Privileged access ownership: Administrators, service identities, recovery paths, and local privilege mapped to a current approved owner and business purpose.
- Matter-access accuracy: Active and restricted matter access matching the approved team, including inherited groups, integrations, and temporary exceptions.
- Authoritative-record coverage: Client and matter information stored in approved systems with unmanaged copies and abandoned portals resolved.
- Deadline continuity: Critical dates with source, responsible lawyer, backup coverage, completion evidence, and tested reassignment.
- Restore readiness: Representative matter and system restores completed within approved recovery objectives using current administrators.
- Departure and vendor continuity: People and provider changes completed without lost records, broken automation, missing access, or interrupted client service.
Worked example: remove a former administrator without losing a matter workflow
Hypothetical cleanup record. Adapt the evidence to the firm’s platform and record decisions; these rows do not authorize deletion or establish legal compliance.
On a narrow screen, scroll horizontally to read every table column.
| Dependency found | Controlled action | Completion evidence |
|---|---|---|
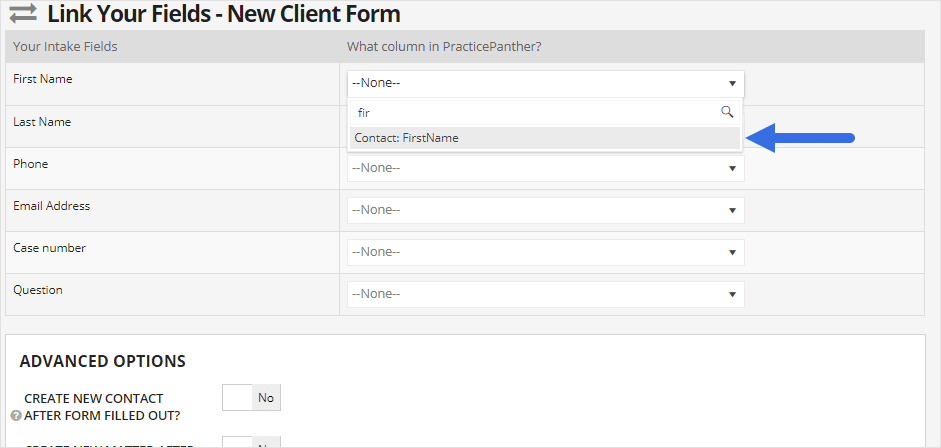
| Former employee owns the matter-intake form connection | Assign an approved replacement owner and reconnect a non-client test submission. | A current owner receives the test and can repair the connection; no confidential facts enter the test. |
| Restricted matter inherits an all-staff group | Correct the source group and any separate sharing path. | The approved team opens the matter; an unrelated test account cannot find or open it. |
| Departing user alone receives a critical reminder | Assign the responsible lawyer and backup through the firm’s deadline process. | The backup finds the original notice and acknowledges the correct task without the old account. |
Frequently Asked Questions
How should a law firm clean up administrator access?
Start by identifying every privileged person and service identity, then establish a firm-controlled recovery administrator before reducing access. Check practice management, documents, email, billing and remote support separately. An old administrator may also own an integration or recovery method. Preserve the logs, transfer those dependencies, and confirm that a current administrator can perform the required work before removing obsolete privileges.
How often should law firm matter access be reviewed?
Review matter access whenever the team, employment status, confidentiality restriction or matter status changes, and on a documented periodic schedule. Monthly checks for restricted or rapidly changing matters and quarterly checks for stable matters are possible starting points for the responsible lawyer to adjust; they are operational examples, not a prescribed legal interval. Compare the approved roster with effective permissions and test both an allowed user and an unrelated user.
How can a law firm clean up client files stored in personal locations?
Choose the authoritative matter repository first. Move a small, representative set of files with its dates, links and required history, then ask a matter-team member to retrieve it from the approved location. Resolve personal folders and email-only copies through the firm’s retention decision. Do not delete duplicates until the responsible lawyer confirms that required records and holds are preserved.
How can a law firm reduce deadline risk during staff changes?
Give every critical date a responsible lawyer, a backup and a traceable source notice before changing staff access. Test an absence: can the backup find the source, see the deadline and act without the departing person’s mailbox? Technology can support the firm’s review process, but it should not silently calculate or approve a legal deadline without the assigned professional’s control.
What billing access should be reviewed during a law firm IT cleanup?
Review who can change payment details, approve invoices, issue refunds, export client information and administer billing. Give each role only the authority it needs, and independently verify financial-detail changes through a known contact route. Keep trust-account and other professional decisions with the firm’s responsible people; an application permission setting does not settle those obligations.
Supporting sources: [4]
Which law firm systems must be checked after an employee departure?
Check the departing person’s matter assignments, email, calendars, documents, forms, e-signature, integrations and recovery methods. Block access promptly using the platform’s supported offboarding process while preserving records and continuity. For Microsoft 365, blocking sign-in, saving data, arranging continuing mailbox/OneDrive access and deleting the account are separate steps; do not assume that removing a license completes the departure.
Supporting sources: [2]
How should a law firm review AI tools during an IT cleanup?
Decide whether the specific tool and account may receive the specific client information before allowing routine use. Review its terms, retention, sharing, training use, connected accounts and matter restrictions with the firm’s responsible lawyer. Use non-client test material during evaluation. Require professional checking of citations and conclusions, and offer an approved alternative when users would otherwise invent their own workflow.
Supporting sources: [1]
What should a law firm restore during a backup test?
Restore a representative matter with its documents, important correspondence, permissions and required history into a controlled environment. Include a restricted matter and a file that was changed or deleted before the test. Record what was missing and how long retrieval took. A vendor’s successful backup job is not a substitute for the firm demonstrating that it can resume the affected work.
Supporting sources: [3]
What belongs in a law firm technology vendor access review?
Keep a current owner, named vendor identities, approved scope, recovery contacts and an exit checklist for each important provider. Test whether the firm can administer the system and obtain usable records without that provider. Remove unnecessary standing access, preserve relevant activity evidence and verify the export before approving an account closure or contract transition.
How can a law firm test incident response without disrupting real matters?
Use a fictional active matter and a near-term deadline in a tabletop exercise. Walk through an unavailable practice system or compromised mailbox without sending real client notices or changing production access. Record who makes containment, continuity, client-communication and legal-notification decisions. Turn each missing contact or failed handoff into an assigned action and repeat the failed part.
Choose the next step
- Protect Client Data and Keep Legal Teams Productive — Use the security review to test whether the cleanup fixed effective access and recovery.
- Build Reliable Legal IT Around Matters, Deadlines, and Client Data — Rebuild the daily matter and deadline workflow when the dependency needs a wider redesign.
Sources
- State Bar of Georgia: Georgia Rules of Professional Conduct. Current official Georgia rulebook to review confidentiality, supervision and communications about legal services; attorney determines application. ↩
- Microsoft 365: Remove a former employee and secure data. Block sign-in, preserve required mailbox and OneDrive data, arrange continuing access and handle licensing/deletion as distinct steps; Microsoft 365 example only. ↩
- CISA: #StopRansomware Guide. Maintain protected offline/encrypted backups, regularly test recovery, and understand cloud responsibility; no universal 14–30 day retention rule. ↩
- FBI: Business Email Compromise. Independently verify payment and account-number changes via known contact routes instead of replying to the changed message. ↩
- Microsoft Support: See who a file is shared with in OneDrive or SharePoint ↩