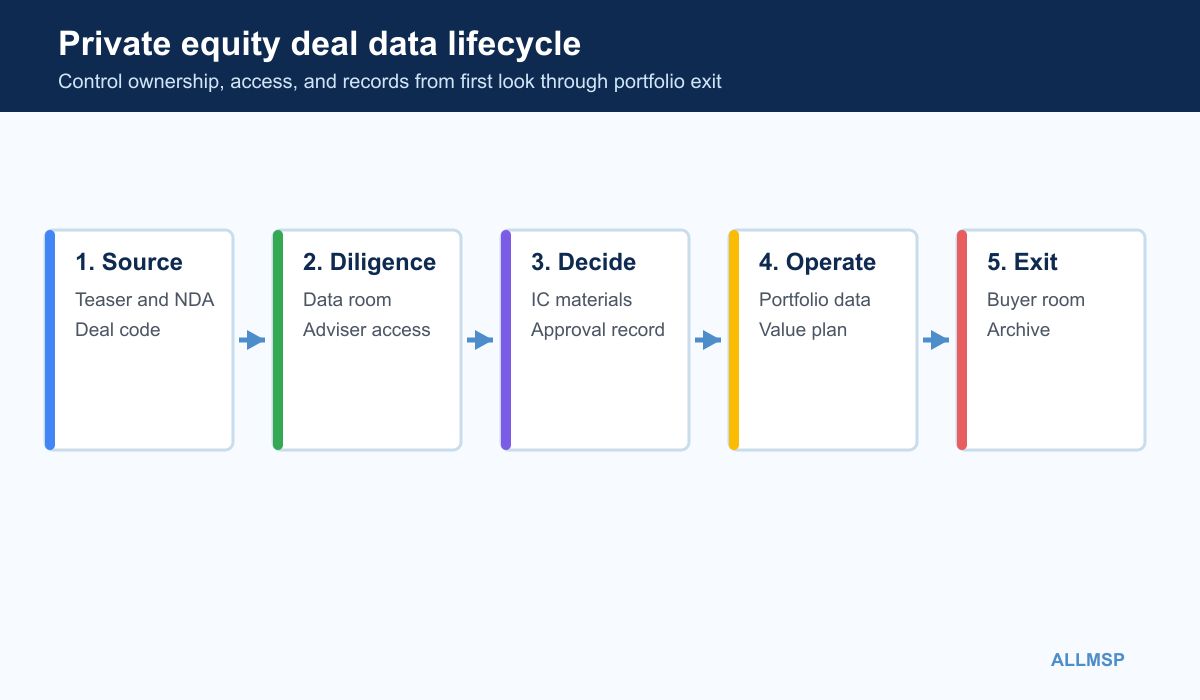
Private equity technology cleanup should expose dependencies before removing them. An adviser may own a data room, an employee may own a fund export or automation, and a portfolio integration may rely on a personal credential. Deal files can persist in abandoned rooms and synchronized folders long after a transaction ends.
Preserve investment, fund, transaction, investor, legal, compliance, and portfolio records according to current decisions before deletion. Transfer ownership and test replacement access before removing employees, advisers, providers, integrations, or service accounts. Coordinate work around active diligence, signing, closing, wires, reports, audits, and exits.
How to choose the right private equity IT improvements
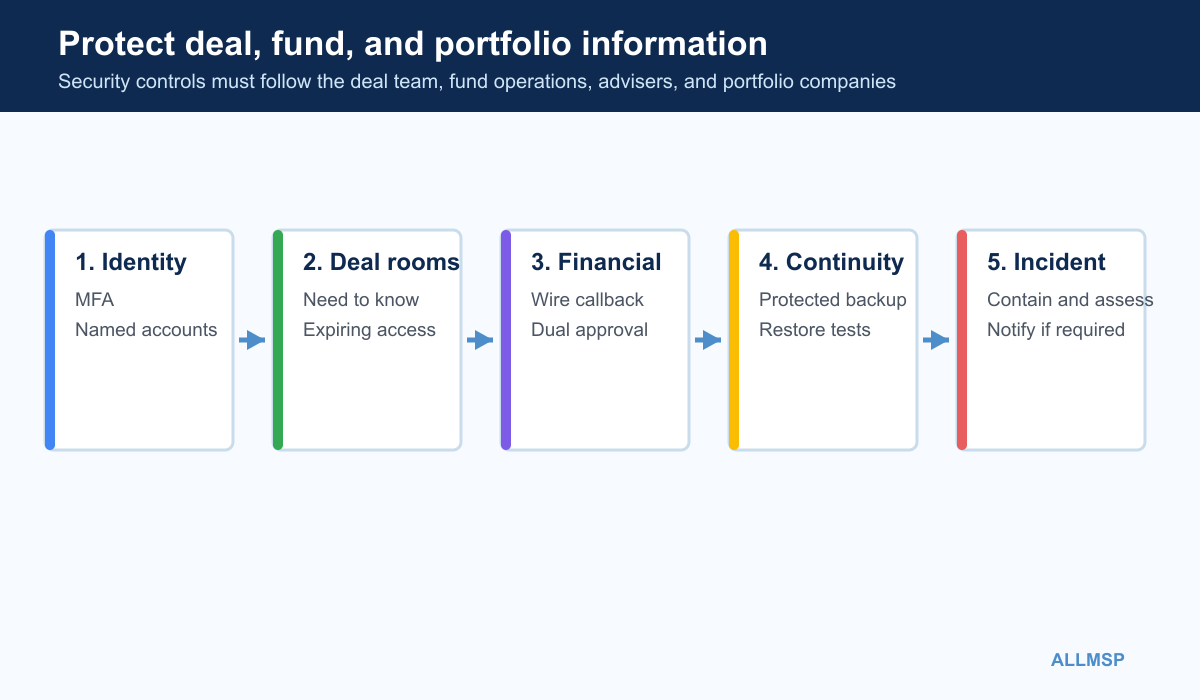
A successful cleanup leaves one accountable record for entities, systems, deals, rooms, fund data, people, advisers, devices, integrations, portfolio connections, providers, backups, deadlines, and exceptions. Temporary access is closed, financial authority is separated, and recovery is proven.
- Former employees, advisers, portfolio users, providers, or unknown service identities remain active.
- Abandoned or closed deal rooms still permit links, downloads, synchronized copies, or unowned administration.
- Wires, fund reports, portfolio dashboards, or recurring exports depend on one employee or personal credential.
- Portfolio cyber findings lack post-close owners, budgets, evidence, deadlines, or board escalation.
- Devices, integrations, and remote tools do not match the worker, adviser, deal, or portfolio inventory.
- Backups report success without clean restores of deal, fund, investor, and configuration records.
Find deal, fund, identity, adviser, device, and portfolio dependencies
Unknown privileged, adviser, and service access
Diagnosis: Export owners, administrators, recovery contacts, advisers, providers, service identities, delegated roles, local administrators, tokens, and sessions. Match each to a current sponsor, purpose, entity, fund, deal, portfolio, last use, and end date.
Private Equity Firms IT improvement: Add company-controlled recovery, separate administration, close unknown or expired access, reduce roles, rotate affected credentials, transfer ownership, enforce expiration, and alert on privilege and recovery changes.
Measurement: Track known privileged identities, MFA, stale access removed, provider sessions, emergency recovery tests, time-limited access, and approved exceptions.
Abandoned and overexposed deal rooms
Diagnosis: Inventory active, rejected, signed, closed, and exited rooms with owner, roster, roles, links, downloads, synchronized copies, administrators, retention, archive, and last activity. Compare with deal status and confidentiality decisions.
Private Equity Firms IT improvement: Correct rosters, remove broad and public links, expire participants, preserve the approved final index and records, transfer administration, close unused rooms, and remove copies through the firm’s approved process.
Measurement: Track rooms with current owners, stale users removed, links closed, archives completed, synchronized copies addressed, and closeout time after deal status changes.
Fund and investor data outside approved systems
Diagnosis: Sample email, local folders, downloads, personal storage, shared links, spreadsheets, CRM exports, portal exports, and adviser locations for investor, capital account, tax, banking, and reporting information.
Private Equity Firms IT improvement: Move required records to approved repositories, preserve context and retention, correct delivery and export procedures, restrict access, close public links, remove redundant copies through approved handling, and coach users who created workarounds.
Measurement: Track unsafe locations, records migrated, public links closed, portal adoption, recurring exports, stale copies, and follow-up sample results.
Correct rooms, authority, data placement, integrations, and support
Broad wire and financial authority
Diagnosis: List banking, capital-call, distribution, AP, payroll, vendor, fund accounting, administrator, approval, release, reconciliation, administration, and contact-change roles by person and last use. Compare with current duties and dual-control policy.
Private Equity Firms IT improvement: Separate initiation, verification, approval, release, reconciliation, and administration, remove standing authority, refresh independent callback records, expire emergency roles, and test representative changes and transactions.
Measurement: Track high-impact roles reduced, dual approval, callbacks completed, emergency duration, transaction alerts reviewed, fraudulent-change tests, and exceptions.
Employee-owned integrations and reporting
Diagnosis: List scheduled fund and portfolio exports, dashboards, data connectors, CRM automation, APIs, scripts, mailbox rules, browser extensions, service identities, personal billing, credentials, and failure handling.
Private Equity Firms IT improvement: Transfer critical ownership to managed identities where supported, reduce scopes, rotate secrets, document input and output, add monitoring and backup owners, remove abandoned connections, and create manual continuity for critical reports.
Measurement: Track managed ownership, excessive scopes removed, secrets rotated, failures detected, orphaned automation retired, and continuity tests completed.
Unmanaged devices and remote tools
Diagnosis: Reconcile procurement, workers, advisers, device management, endpoint security, encryption, networks, VPN, remote support, mobile management, return, and disposal. Find unsupported systems, unknown tools, stale devices, and local administrators.
Private Equity Firms IT improvement: Enroll, patch, encrypt, protect, replace, quarantine, recover, or retire each system. Remove unauthorized remote access and local privilege, recover firm data, and document approved personal-device and adviser boundaries.
Measurement: Track inventory match, encryption, patch and protection coverage, unsupported devices, local administrators, unknown remote tools, returns, and disposal evidence.
Portfolio cyber findings lost after close
Diagnosis: Compare diligence requests, evidence, findings, deal assumptions, investment-committee material, insurance, purchase terms, 100-day plans, budgets, board reporting, tickets, and current technical state. Identify findings without proof or owner.
Private Equity Firms IT improvement: Assign sponsor and portfolio owners, fund urgent containment, define outcome and evidence, schedule board or operating review, record accepted risk, and integrate unresolved findings into ongoing portfolio oversight.
Measurement: Track material findings with owners, overdue actions, risk acceptance, budget, proof completed, repeat findings, incidents tied to known gaps, and board escalation.
Improve portfolio remediation, monitoring, recovery, and closeout
Monitoring and support lack deal context
Diagnosis: Compare identity, email, endpoint, cloud, room, finance, backup, and provider alerts with tickets and incidents. Identify noise, blind spots, missed ownership, unknown deal sensitivity, and recurring warnings without root-cause correction.
Private Equity Firms IT improvement: Route meaningful events to accountable queues, include entity, deal, fund, portfolio, user, device, and financial context, define severity and timing, add after-hours escalation, and correct recurring causes.
Measurement: Track critical coverage, alert-to-ticket linkage, acknowledgment and containment time, deal-context completeness, recurring events, missed escalations, and corrective closure.
Backup and provider export are unproven
Diagnosis: Map rooms, email, fund systems, CRM, investor records, finance, portfolio reporting, configurations, local data, and provider exports to protected copies. Inspect failures, permissions, immutability, retention, and restore evidence.
Private Equity Firms IT improvement: Add missing scope, isolate backup administration, correct jobs, automate protected exports, run clean restores, document timing and dependencies, and repeat around platform, fund, transaction, and provider changes.
Measurement: Track protected critical data, clean restores, restore time, recovery-point gap, export currency, failures corrected, and unresolved provider dependencies.
Deal closeout and incident procedures are stale
Diagnosis: Compare room closeout, adviser removal, portfolio handoff, archive, investor and fund contacts, incident plans, provider notices, regulatory decisions, insurance, continuity, and escalation procedures with current systems and recent transactions.
Private Equity Firms IT improvement: Update from verified current state, assign owners and review dates, connect procedures to tickets and closing checklists, run a deal-closeout and incident exercise, train affected roles, and archive approved versions.
Measurement: Track timely room closure, adviser access removed, portfolio ownership transferred, current contacts, exercise findings closed, procedure reviews, and recurring support errors.
Measure visibility and control after cleanup
Review cleanup decisions with investment, finance, investor relations, compliance, operations, security, and portfolio leaders. Every action should name the entity, deal, fund, portfolio, dependency, preserved evidence, replacement owner, deadline, user communication, verification, and follow-up date.
- Known ownership: Systems, accounts, rooms, administrators, service identities, advisers, integrations, providers, devices, and recoveries mapped to current owners and entities.
- Deal access accuracy: Sampled room and workspace permissions matching current deal status, role, need to know, approval, and expiration.
- Financial-control coverage: Wire, capital-call, distribution, vendor, payroll, and banking changes using separated authority and independent verification.
- Portfolio remediation: Material cyber findings with sponsor and portfolio owners, budgets, due dates, evidence, escalation, and accepted-risk records.
- Detection and support: Critical events reaching accountable responders with entity, deal, fund, portfolio, user, device, and financial context.
- Recovery and closeout: Representative records restored and closed deals transferred, archived, and cleared of temporary access within approved time.
Frequently Asked Questions
How should a private equity firm clean up unknown administrator and adviser access?
Start with this diagnostic step: Export owners, administrators, recovery contacts, advisers, providers, service identities, delegated roles, local administrators, tokens, and sessions, Match each to a current sponsor, purpose, entity, fund, deal, portfolio, last use, and end date. Next, add company-controlled recovery, separate administration, close unknown or expired access, reduce roles, rotate affected credentials, transfer ownership, enforce expiration, and alert on privilege and recovery changes. Use track known privileged identities, MFA, stale access removed, provider sessions, emergency recovery tests, time-limited access, and approved exceptions to determine whether the change helped.
What is the safest way to clean up old private equity data rooms?
Start with this diagnostic step: Inventory active, rejected, signed, closed, and exited rooms with owner, roster, roles, links, downloads, synchronized copies, administrators, retention, archive, and last activity, Compare with deal status and confidentiality decisions. Next, correct rosters, remove broad and public links, expire participants, preserve the approved final index and records, transfer administration, close unused rooms, and remove copies through the firm’s approved process. Use track rooms with current owners, stale users removed, links closed, archives completed, synchronized copies addressed, and closeout time after deal status changes to determine whether the change helped.
How should a private equity firm clean up investor information stored outside approved systems?
Start with this diagnostic step: Sample email, local folders, downloads, personal storage, shared links, spreadsheets, CRM exports, portal exports, and adviser locations for investor, capital account, tax, banking, and reporting information. Next, move required records to approved repositories, preserve context and retention, correct delivery and export procedures, restrict access, close public links, remove redundant copies through approved handling, and coach users who created workarounds. Use track unsafe locations, records migrated, public links closed, portal adoption, recurring exports, stale copies, and follow-up sample results to determine whether the change helped.
How can private equity firms reduce excessive wire and payment authority?
Start with this diagnostic step: List banking, capital-call, distribution, AP, payroll, vendor, fund accounting, administrator, approval, release, reconciliation, administration, and contact-change roles by person and last use, Compare with current duties and dual-control policy. Next, separate initiation, verification, approval, release, reconciliation, and administration, remove standing authority, refresh independent callback records, expire emergency roles, and test representative changes and transactions. Use track high-impact roles reduced, dual approval, callbacks completed, emergency duration, transaction alerts reviewed, fraudulent-change tests, and exceptions to determine whether the change helped.
How should private equity firms clean up employee-owned reporting and automation?
Start with this diagnostic step: List scheduled fund and portfolio exports, dashboards, data connectors, CRM automation, APIs, scripts, mailbox rules, browser extensions, service identities, personal billing, credentials, and failure handling. Next, transfer critical ownership to managed identities where supported, reduce scopes, rotate secrets, document input and output, add monitoring and backup owners, remove abandoned connections, and create manual continuity for critical reports. Use track managed ownership, excessive scopes removed, secrets rotated, failures detected, orphaned automation retired, and continuity tests completed to determine whether the change helped.
How can a private equity firm clean up deal-team devices and remote access?
Start with this diagnostic step: Reconcile procurement, workers, advisers, device management, endpoint security, encryption, networks, VPN, remote support, mobile management, return, and disposal, Find unsupported systems, unknown tools, stale devices, and local administrators. Next, enroll, patch, encrypt, protect, replace, quarantine, recover, or retire each system, Remove unauthorized remote access and local privilege, recover firm data, and document approved personal-device and adviser boundaries. Use track inventory match, encryption, patch and protection coverage, unsupported devices, local administrators, unknown remote tools, returns, and disposal evidence to determine whether the change helped.
How should sponsors improve follow-through on portfolio cyber diligence?
Start with this diagnostic step: Compare diligence requests, evidence, findings, deal assumptions, investment-committee material, insurance, purchase terms, 100-day plans, budgets, board reporting, tickets, and current technical state, Identify findings without proof or owner. Next, assign sponsor and portfolio owners, fund urgent containment, define outcome and evidence, schedule board or operating review, record accepted risk, and integrate unresolved findings into ongoing portfolio oversight. Use track material findings with owners, overdue actions, risk acceptance, budget, proof completed, repeat findings, incidents tied to known gaps, and board escalation to determine whether the change helped.
How can private equity security monitoring include deal and portfolio context?
Start with this diagnostic step: Compare identity, email, endpoint, cloud, room, finance, backup, and provider alerts with tickets and incidents, Identify noise, blind spots, missed ownership, unknown deal sensitivity, and recurring warnings without root-cause correction. Next, route meaningful events to accountable queues, include entity, deal, fund, portfolio, user, device, and financial context, define severity and timing, add after-hours escalation, and correct recurring causes. Use track critical coverage, alert-to-ticket linkage, acknowledgment and containment time, deal-context completeness, recurring events, missed escalations, and corrective closure to determine whether the change helped.
How should private equity firms prove that provider and cloud data can be recovered?
Start with this diagnostic step: Map rooms, email, fund systems, CRM, investor records, finance, portfolio reporting, configurations, local data, and provider exports to protected copies, Inspect failures, permissions, immutability, retention, and restore evidence. Next, add missing scope, isolate backup administration, correct jobs, automate protected exports, run clean restores, document timing and dependencies, and repeat around platform, fund, transaction, and provider changes. Use track protected critical data, clean restores, restore time, recovery-point gap, export currency, failures corrected, and unresolved provider dependencies to determine whether the change helped.
When should private equity deal-closeout and incident procedures be updated?
Start with this diagnostic step: Compare room closeout, adviser removal, portfolio handoff, archive, investor and fund contacts, incident plans, provider notices, regulatory decisions, insurance, continuity, and escalation procedures with current systems and recent transactions. Next, update from verified current state, assign owners and review dates, connect procedures to tickets and closing checklists, run a deal-closeout and incident exercise, train affected roles, and archive approved versions. Use track timely room closure, adviser access removed, portfolio ownership transferred, current contacts, exercise findings closed, procedure reviews, and recurring support errors to determine whether the change helped.