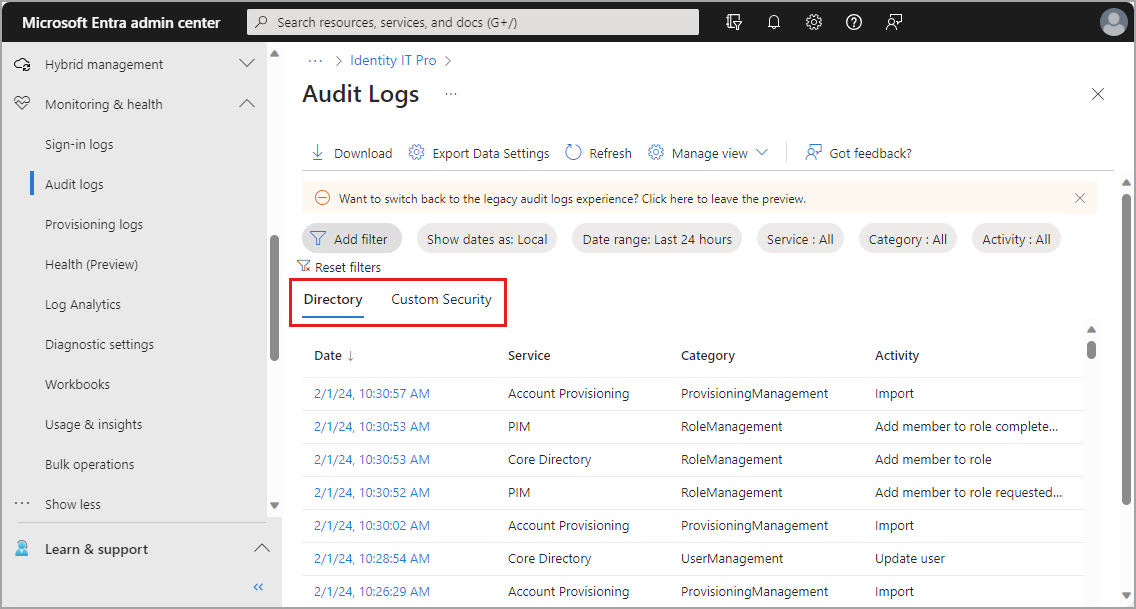
Microsoft’s published Entra audit-log sample uses 2024 example dates and a preview interface. Its date range, filters and directory activities show where to investigate who changed an identity or role. Verify the resulting access separately; a logged event does not prove that the firm’s full access review or recovery test passed.[5]
A useful security review does not begin with a generic score. It collects current evidence from the written plan, identities, client systems, devices, integrations, vendors, alerts, backups, support records, and incidents. The evidence should show whether safeguards operate during ordinary work and peak deadlines.
Preserve logs, approvals, ownership, client records, and recovery paths before changing access or deleting anything. Confirm which obligations apply to the firm’s services and registration. A review should identify uncertainty for leadership or counsel rather than present every IRS, FTC, SEC, or FINRA requirement as universal.
The FTC guide explains coverage and risk-based safeguards for entities within its jurisdiction; it is not a universal requirement for every business called a financial firm. IRS Publication 4557 addresses taxpayer-data safeguards for tax professionals. Confirm the firm’s actual services and legal scope. [1] [2]
Evidence to collect before changing CPA and financial firm IT
The review produces a dated record of scope, tested controls, failed evidence, affected services and data, risk priority, accountable owner, corrective action, verification, and written-plan update. It separates configuration problems from training, workflow, vendor, capacity, and governance problems.
- Current service inventory, regulatory determination, written information security plan, policies, insurance requirements, and responsible people.
- User, group, administrator, service-account, recovery, device, application, portal, integration, and vendor-access exports.
- Security alerts, email events, endpoint status, vulnerability and patch findings, support tickets, incidents, and response records.
- Backup scope, job history, restore evidence, application exports, business-continuity tests, and deadline coverage.
- Vendor contracts, data flows, breach-notice contacts, access methods, recovery promises, and exit procedures.
Confirm scope, ownership, identity, and client access
Written plan and service scope
What to check: Record approval date, responsible person, covered services and information, risk assessment, safeguards, providers, training, testing, incident process, review cadence, and unsupported assumptions.
What to do next: Assign an accountable owner, confirm actual legal and contractual scope, update the plan from current systems and risks, and schedule leadership approval and recurring review.
Privileged identity and recovery
What to check: Export administrators, roles, shared accounts, service identities, MFA status, recovery methods, emergency accounts, last use, and vendor access. Test backup ownership without exposing privileged credentials.
What to do next: Add company-controlled recovery, separate daily and administrative identities, reduce roles, remove unknown access, rotate affected secrets, and alert on privileged changes.
Client and engagement access
What to check: Sample active, inactive, restricted, payroll, assurance, tax, and advisory clients across permanent, seasonal, remote, and former users. Capture inherited groups, public links, exports, and exceptions.
What to do next: Assign access from approved role and engagement, correct broad groups, close stale links, transfer ownership, document exceptions, and repeat the sample until denied and allowed paths match the roster.
Test applications, devices, communications, and monitoring
Endpoint and remote-work control
What to check: Reconcile people to devices and collect enrollment, encryption, patch, protection, administrator, last-seen, risk, ownership, and recovery status. Test one office and one remote workflow.
What to do next: Quarantine high-risk devices, enroll supported equipment, patch, encrypt, reduce local privilege, replace unsupported systems, close unknown remote tools, and document approved personal-device boundaries.
Application integrations and service identities
What to check: List owner, purpose, permissions, client data, credential type, last use, logs, failure handling, renewal, export, and removal path for each integration and service identity.
What to do next: Disable unknown or unused connections after preserving evidence, reduce scopes, replace employee credentials with managed service identity where supported, rotate secrets, assign monitoring, and document failure recovery.
Email, phishing, and financial-change procedure
What to check: Test spoofing controls, external forwarding, hidden rules, executive impersonation, reporting, escalation, and independent verification using representative messages.
What to do next: Correct authentication and protection, remove malicious rules and access, require known-channel verification, retrain affected roles, and monitor high-risk financial and credential changes.
FBI guidance recommends independent verification of payment/account-number changes using a known contact route. [4]
Security monitoring and support evidence
What to check: Choose representative critical and warning events and record whether they were received, owned, investigated, contained, resolved, documented, and followed by corrective action within expectations.
What to do next: Fix missing telemetry and routing, assign severity and ownership, create escalation and after-hours coverage, test a known event, and review recurring alerts that support staff have normalized.
Review vendors, recovery, support, and incident readiness
Provider safeguards and breach notice
What to check: For each material provider, record client information handled, access, safeguards evidence, notice timing, responsible contacts, recovery, subcontractor relevance, and replacement or export steps.
What to do next: Escalate missing material terms, reduce standing access, add internal ownership and notice contacts, test export and recovery, and obtain leadership or counsel review where contractual risk remains.
Backup, restore, and continuity
What to check: Match production data to protected copies and capture retention, encryption, immutability, success history, failed jobs, restore time, restore completeness, responsible owner, and deadline priorities.
What to do next: Add missing data, isolate backups, correct failures, document cloud responsibility, run clean restores, and revise continuity steps around filing, payroll, close, client delivery, and communications.
CISA recommends protected backups and regular recovery testing, including attention to cloud responsibility. [3]
Incident and support readiness
What to check: Run a scenario involving client-data access, account takeover, ransomware, vendor outage, or financial fraud and capture response timing, decisions, missing information, deadline effects, and corrective tasks.
What to do next: Correct contact, authority, evidence, containment, continuity, notification, and recovery gaps, then repeat the exercise and update the written plan and training.
Prioritize findings by client impact and deadline risk
Present findings by affected client information, service, deadline, likelihood, operational consequence, evidence strength, immediate containment, long-term correction, owner, due date, and retest. A useful report tells leaders what to decide and technicians what must pass.
Priority 1: Active exposure or inability to operate
Respond immediately to confirmed compromise, exposed client or taxpayer information, uncontrolled privileged access, fraudulent financial changes, failed critical backup, unsupported internet-facing systems, or an outage threatening filing, payroll, close, or client obligations.
Priority 2: Material control failure
Correct missing MFA, broad client access, unknown service identities, unmanaged devices, untested recovery, vendor-notice gaps, or ineffective alert handling on a scheduled urgent plan with accountable leadership.
Priority 3: Process and evidence weakness
Address incomplete inventories, stale procedures, inconsistent training, unclear metrics, weak ownership, and lower-impact configuration drift after higher-risk paths are controlled.
Priority 4: Planned improvement
Sequence usability, automation, reporting, and modernization work only after the firm can protect, support, recover, and explain the current environment.
What counts as evidence in a financial-firm review?
Illustrative audit tests. Confirm the applicable legal and contractual scope separately; these examples do not certify compliance.
On a narrow screen, scroll horizontally to read every table column.
| Claim | Evidence to request | Finding if the test fails |
|---|---|---|
| “The written plan is current” | Compare one new service/provider with the plan, named owner and risk decision. | Plan scope does not match the live business; assign a scoped update and approval. |
| “Client access is restricted” | A permitted user opens the sample; an unrelated or expired user is denied through all relevant sharing paths. | An inherited group or link bypasses the approved engagement roster. |
| “Backups protect client delivery” | Recover a representative client dataset and its usable application/export; record age and elapsed time. | A successful job exists but the required data or application cannot be recovered. |
Frequently Asked Questions
What evidence shows that a CPA firm's written security plan is current?
A current written plan should agree with the firm’s real services, data, systems, providers, responsible people and risk decisions. Compare its inventory with live exports and its procedures with a recent incident or exercise. Record what changed and who approved it. A recently edited cover date does not prove that the safeguards operate or that the plan covers the actual business.
How should a financial firm review administrator and recovery access?
List privileged roles and recovery methods across the applications that can expose client data or interrupt operations. Confirm a current owner and business purpose, then test firm-controlled recovery without disclosing privileged credentials. Review shared accounts and vendor access separately. Preserve evidence and replacement ownership before removing an unexplained identity, and verify both normal administration and emergency access afterward.
How can a CPA firm test whether client access is too broad?
Use the engagement roster to define who should and should not reach a sample client record. Test those people through direct permissions, inherited groups, portal links and exports, including seasonal and former users. A denied test must actually fail while the permitted user still works. Correct the access path at its source and retain the result for the next staffing review.
What should a CPA firm verify during a device security review?
Verify the device is known, assigned, supported and reporting current management/security evidence. Check encryption recovery, patch status, protection, local privileges and remote-support tools, then test an ordinary office and remote workflow. Investigate records that disagree rather than accepting a coverage percentage. Treat a missing endpoint agent and a genuinely lost device as different findings.
Why should accounting firms review integrations and service accounts?
An integration can read client information or move payroll and accounting data even when no employee signs in. Record its supported owner, permissions, credential lifecycle and outputs. Test that a failed run is detected and the destination reconciles with the source. Remove or reduce access only after identifying the dependencies and preserving the firm’s evidence and continuity needs.
What should a financial firm test in its email security review?
Test whether staff can report a suspicious message and whether the assigned responder can investigate it. Review spoofing protections, forwarding, delegated access and unexpected mailbox rules. Separately rehearse a financial-detail change using an independent known-number verification route. Passing an email-authentication check does not prove that a payment request inside a compromised legitimate account is safe.
Supporting sources: [4]
How can a firm tell whether security alerts are actually being handled?
Pick a real or safely generated representative event and follow it from the source log to an accountable responder, investigation, decision and closure record. Record timestamps and missed handoffs. An alert existing in a dashboard is not evidence that anyone acted on it. Correct routing or coverage gaps and repeat the failed step with the responsible team.
What service-provider evidence should a CPA or financial firm keep?
Keep the provider’s business owner, data handled, approved access, relevant contract terms, security evidence, incident contacts and exit/export procedure together. For FTC-covered firms, evaluate providers against the applicable Safeguards Rule requirements. A certificate or sales assurance is one input, not proof of every control. Escalate missing material terms and test that the firm can obtain usable records.
Supporting sources: [1]
What evidence proves that financial-firm backup can actually recover client work?
A completed restore using the actual protected copy is stronger evidence than a successful-job report. Recover representative records, application exports and necessary configurations into a controlled environment. Check that authorized staff can use them, measure elapsed time and document the age of recovered data. Record any SaaS information the backup did not cover and the alternative recovery path.
Supporting sources: [3]
How often should CPA and financial firms test incident response?
Set an exercise cadence from the firm’s risks and applicable obligations, then retest after major changes, incidents or failed exercises. A practical internal baseline is an annual tabletop plus targeted tests during the year, but it is not a universal legal frequency. Use a realistic account-takeover or provider-outage scenario and close the specific continuity and decision gaps it exposes.
Supporting sources: [1]
Choose the next step
- Reduce Accounting Technology Delays During Peak Work — Turn confirmed audit findings into a controlled accounting-technology cleanup.
- Prepare Financial-Firm IT for Tax Season and Client Deadlines — Redesign the underlying peak-work setup when several findings share the same workflow gap.
Sources
- FTC Safeguards Rule: What Your Business Needs to Know. Rule applies by covered activity/jurisdiction; written risk-based program, access controls, provider oversight and periodic evaluation for covered entities, with specific exceptions. ↩
- IRS Publication 4557: Safeguarding Taxpayer Data. Tax-professional taxpayer-data safeguards, written security plan, access and recovery guidance; not universal securities-regulator requirements. ↩
- CISA: #StopRansomware Guide. Maintain protected offline/encrypted backups, regularly test recovery, and understand cloud responsibility; no universal 14–30 day retention rule. ↩
- FBI: Business Email Compromise. Independently verify payment and account-number changes via known contact routes instead of replying to the changed message. ↩
- Learn about the audit logs in Microsoft Entra ID - Microsoft Entra ID | Microsoft Learn ↩