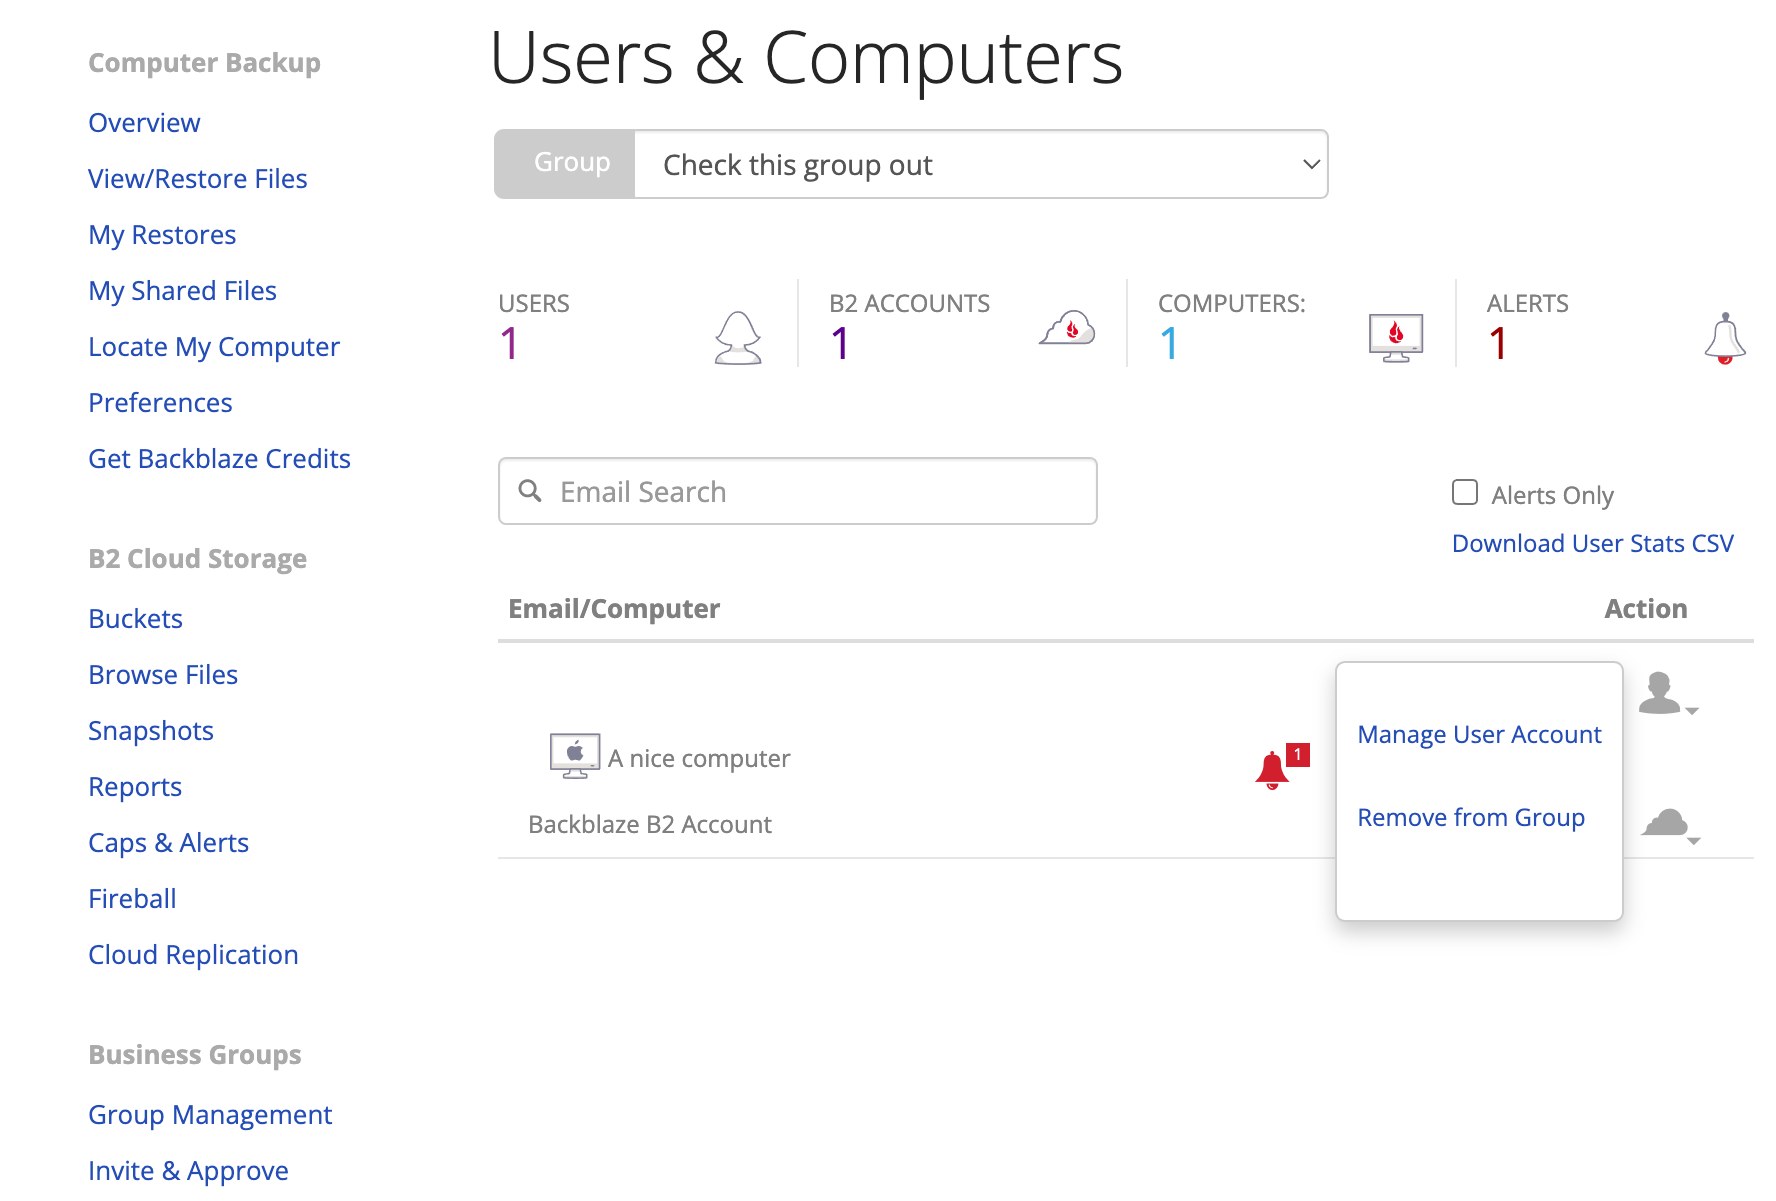
Backblaze’s published group-administration example shows Manage User Account and Remove from Group before either action is executed. Check the actual approved role and account disposition. This historical interface does not prove effective restore permission, completed removal, session revocation or account deletion.[5] View full-size image
Backblaze administration involves more than a working sign-in. A managed-group administrator can reach member backup data, Enterprise Control can change restore and deletion authority, and a departing person’s group membership is separate from their account, payment and identity access. Decide which operator is authorized to do which action before treating a console option as permission to use it.
For an urgent authorized cutoff, contain access through the approved identity, account and endpoint controls immediately. Do not wait for a business handoff or restore. Preserve required records through an authorized remaining recovery owner while separately checking group membership, backup retention and passphrase custody. Do not assume that a group-removal click terminates every session or deletes the person’s account.
Our in-house team delivers Backblaze Business Backup access, ownership, and security review for businesses around Lawrenceville, Suwanee, Gwinnett County, Metro Atlanta, and the rest of Georgia, while coordinating the applications, identities, devices, data, security controls, and employees affected by the work.
Key decisions at a glance
- Document whether administrators may browse and restore member backups because managed-group authority changes the privacy and insider-risk model.
- Treat Enterprise Control file-management options as an approval checkpoint because those settings cannot be changed after configuration.
- Use OpenID Connect SSO for authentication where appropriate, but govern group membership, administrator roles, account recovery, and endpoint ownership as distinct lifecycle controls.
- If a private encryption passphrase is enabled, maintain tested dual custody because Backblaze cannot recover forgotten material or restore the affected backup without it.
- For an urgent authorized cutoff, contain access immediately; preserve required data through an authorized remaining recovery owner while separately closing group access, payment and endpoint coverage.
Define managed-group and Enterprise Control authority before configuration
Start with a role matrix that separates group billing, member approval, administrator management, backup-status review, account impersonation, file browsing, restore creation, backup deletion, user deletion, SSO configuration, and encryption custody. Backblaze says group administrators have equal rights and can add or remove other administrators, which makes every administrator assignment material. Require an accountable business owner, security approval, periodic recertification, and at least two trained but narrowly selected administrators for continuity.
Record the managed-group privacy decision. Managed administrators can enter a member’s account through Users/Computers, inspect backups, create restores, and update certain account details. Users must acknowledge administrator access when they join a managed group. An unmanaged design limits administrators to payment and group administration without file access. The consent notice, employment policy, support procedure, and legal basis should agree with the chosen design before invitations are issued.
Treat Enterprise Control as an entitlement and irreversible-change gate. The published setup procedure first requires Backblaze Sales or Support to grant access. Its File Management choices govern administrator deletion of member backups, member deletion of their own backups and administrator restore on behalf of members; the documentation says those choices cannot be edited after configuration. Distinguish those decisions from later-editable advanced options such as membership locking, restore-purchase restrictions, update control and the menu icon. Preserve an approved decision record and test plan before submitting the wizard; do not assume every Business Group already has this entitlement.
Business Groups combine product billing with a selected administration model,[1] and group creation fixes the managed-access decision.[2] Review B2 group-account administration separately when storage accounts share the group; do not substitute it for an endpoint restore-permission review.[3] The Enterprise Control procedure identifies vendor-granted access and the uneditable File Management settings.[4]
Connect OpenID SSO while keeping membership and restore control separate
Configure SSO as an authentication control for the approved group. Backblaze Enterprise Control supports OpenID Connect by using the issuer or metadata URL, auto-discovered endpoints, authentication, and one or more organization domains. Older group guidance also references selected Google and Microsoft authentication domains. Use the current option presented in the account, record the issuer and verified domains, and test with a normal member, administrator, excluded identity, and recovery identity before broad enforcement.
Do not treat an accepted SSO login as proof of correct group membership or backup ownership. Reconcile identities from the authoritative directory against Backblaze group members, group administrators, computer records, centralized accounts, and decentralized user accounts. A person can authenticate correctly while the wrong computer remains attached to an old account or group. Every joiner and mover event should specify the intended account model, group, region, endpoint name, restore route, and member-data access outcome.
Give the help desk a tested sign-in and restore escalation path. A managed administrator can act on a member’s account, while a decentralized user may restore independently and a centralized user may need the account manager. Require an approval record for administrator-created restores, minimize the selected files, protect the delivery destination, and tell the employee when policy requires. SSO does not remove the need to validate a restore requester’s identity or protect restored data after download.
The current Enterprise Control documentation describes OpenID Connect issuer discovery and domain configuration. Validate the options and entitlement actually present before enforcement; authentication does not itself prove group membership or restore authorization.
Protect private encryption passphrases and prove restore authority
Backblaze encrypts Computer Backup data and manages the backup key in its data centers. An optional passphrase protects that backup key. The current passphrase reference says Backblaze never stores the passphrase, uses it when the user supplies it for a supported operation and immediately discards it afterward. Never storing a passphrase is different from never processing it. If the passphrase is forgotten, the provider cannot restore the data or change or remove the passphrase; approve custody and an authorized recovery test before enabling it.
Design custody before enabling the passphrase. Use an approved secrets vault with dual control or another resilient mechanism, grant access only to named recovery authorities, log retrieval, prohibit copies in tickets or deployment scripts, and keep a secondary recovery path independent of the endpoint and normal identity provider. Record which backups use a passphrase without recording the value. A quarterly custodian review should confirm that multiple authorized people can locate the material under an approved scenario.
Test the complete restore path with the passphrase, not merely retrieval from the secrets vault. Select a small non-sensitive file set, obtain approval, reach the correct member backup, supply the passphrase through the supported interface, download to a controlled device, verify integrity and permissions, and dispose of the test copy. The evidence should prove that the correct custodians can cooperate without disclosing the passphrase to observers, work tickets, or screenshots.
Distinguish the provider-managed backup key from the optional passphrase using the encryption architecture reference[6] and the newer passphrase explanation.[7] The private-key restore guidance confirms that the supplied secret is required when that option protects a backup; do not promise recovery of a forgotten secret.[8]
Offboard members without losing required business data or ownership evidence
Match the response to the offboarding trigger. If access presents an active risk and the cutoff is authorized, begin containment immediately using the responsible identity, account and endpoint owners. Inventory the person’s computers, drives, group and administrator roles, account ownership, region, retention, alerts and passphrase custody in parallel. An authorized remaining administrator or recovery owner should preserve required business records without waiting for the departing person’s cooperation. Keep the archive intact until preservation, retention and legal requirements are resolved; deleting it is not a substitute for access control.
Track administrator removal, directory or SSO action, endpoint isolation or collection and company-account recovery as separate controls, with an owner and observed result for each. Backblaze’s group administration procedure says a removed member is notified to add a payment method for uninterrupted service. That action changes group participation and billing; it does not establish account deletion or complete session revocation. Record whether the account is personal or company-owned, who receives the notice and who retains approved recovery authority. Test the supported access outcome instead of inferring it from a removed row.
Close the event with coverage and data-access evidence. Verify that no departed administrator remains, no orphaned computer is silently excluded from the group’s denominator, required restores are protected, company passphrases remain recoverable, and the active fleet still reports expected status. Preserve the approval, timeline, account and device disposition, restore evidence, group removal, license action, identity change, endpoint action, exceptions, and independent reviewer. Never place recovered file contents or encryption values in the offboarding ticket.
The administrator guide shows account-management and group-removal actions and explains the removed member’s payment notice.[5] A desktop Restore App test must also select the intended restore date and safe destination; a successful sign-in or visible file list is not completed recovery.[9]
Worked leaver review: containment and preservation are separate tracks
This hypothetical review names the evidence still needed. It is not an executed offboarding procedure or a claim about universal session behavior.
| Situation | Immediate decision | Preservation or product check | Closure evidence |
|---|---|---|---|
| Authorized urgent cutoff | Contain identity and endpoint access now through the responsible owners | Keep required archive data available to an approved remaining recovery owner | Record each actual control and test its supported access result; do not wait for handoff |
| A managed administrator needs selected business files | Require a scoped restore approval | Check actual group/Enterprise restore permission and available passphrase custody | A permitted action plus usable restored samples; the presence of Manage User Account is not enough |
| The group member is removed | Treat group participation and billing as changed | Resolve the notified account's company/personal ownership and continued payment decision separately | Verify the group action, account disposition and fleet coverage; do not claim automatic account deletion |
| The passphrase custodian is unavailable | Keep access containment in effect; escalate recovery custody | Do not delete the backup or promise that Support can recover a forgotten passphrase | Approved custody resolution and an actual authorized restore, with secrets excluded from the ticket |
Use the Backblaze deployment and coverage guide when the account-to-endpoint mapping is unclear. Use the Backblaze recovery-testing guide to validate the approved operator, retained date, destination and usable files.
Official product documentation and ALLMSP resources
Frequently Asked Questions
Can a Backblaze managed-group administrator see employee backup data?
Yes. Backblaze says managed administrators can manage a member account, including browsing backed-up data and creating restores. Treat that capability as privileged data access, restrict administrators, align it with employee notice and policy, review it regularly, and retain approval evidence for administrator-created restores.
Do all Backblaze group administrators have the same rights?
Backblaze’s current group guidance says administrators have equal rights and can add or remove other administrators. Keep the administrator set small, require business and security approval, protect each identity, review membership on a schedule, and investigate any unapproved role change as a privileged-access event.
Which Backblaze Enterprise Control settings cannot be changed later?
The published Enterprise Control procedure says its File Management choices cannot be edited after configuration: administrator deletion of member backups, member deletion of their own backups and administrator restore for members. Vendor access must first be granted. Obtain the responsible privacy and recovery approvals before submitting that wizard; do not confuse later-editable advanced settings with those fixed choices.
Does Backblaze Business Backup support OpenID Connect SSO?
The Enterprise Control procedure documents OpenID Connect issuer discovery, authentication and approved domains after the relevant access is granted. Confirm the entitlement and configuration actually available in the group instead of promising OpenID Connect for every account. Test ordinary, administrator and recovery identities, then review membership and restore authority separately from sign-in success.
Does SSO automatically prove a Backblaze computer is in the correct group?
No. Authentication success does not prove correct group membership, administrator assignment, computer ownership, region, or restore route. Reconcile the authoritative identity directory with Backblaze members, administrators, accounts, and endpoint records, then test each joiner and mover scenario through an actual backup and restore.
Can Backblaze recover a forgotten private encryption passphrase?
No. The current passphrase documentation says Backblaze never stores it, uses it when the user supplies it for a supported operation and immediately discards it afterward. Without the forgotten passphrase, Backblaze cannot restore the affected data or change or remove that protection. Maintain approved independent custody and prove an authorized restore before relying on the option.
Should a private encryption passphrase be stored in an endpoint deployment script?
No. Keep it out of scripts, logs, tickets, email, chat, screenshots, and endpoint-local notes. Store it in an approved secrets system with limited recovery authorities, dual control where appropriate, audit logging, an independent contingency path, and a record of which backups use it without the value itself.
What must be approved before an administrator restores a member's files?
Require a documented requester, business purpose, scope, information owner, privacy or legal authority where applicable, approving administrator, secure destination, and disposal plan. Select the minimum necessary files, preserve the operational audit evidence, verify integrity, and never attach recovered sensitive content to the service ticket.
What happens when someone is removed from a Backblaze Business Group?
The administrator guide says the removed member is notified to add a payment method to avoid interruption. Group removal is not account deletion, and that notice does not prove every identity or session is disabled. Decide company versus personal ownership, required preservation and payment separately, and verify the actual authorized access cutoff and remaining backup coverage.
What evidence should close a Backblaze employee offboarding?
Record the authorized trigger and actual identity, administrator and endpoint containment, then separately close group membership, account ownership, retention, passphrase custody and payment. An urgent cutoff must not wait for handoff or a restore. Preserve required records through an approved remaining recovery owner, verify usable output and fleet coverage, and keep secrets and recovered contents out of the ticket.
Sources
- Backblaze Business Groups ↩
- Backblaze create a group ↩
- Backblaze manage groups and member accounts ↩
- Backblaze Enterprise Control ↩
- Backblaze group account administration ↩
- Backblaze Computer Backup encryption ↩
- Backblaze data encryption and passphrases ↩
- Backblaze private encryption key for restore ↩
- Backblaze: create a restore with the Restore App ↩