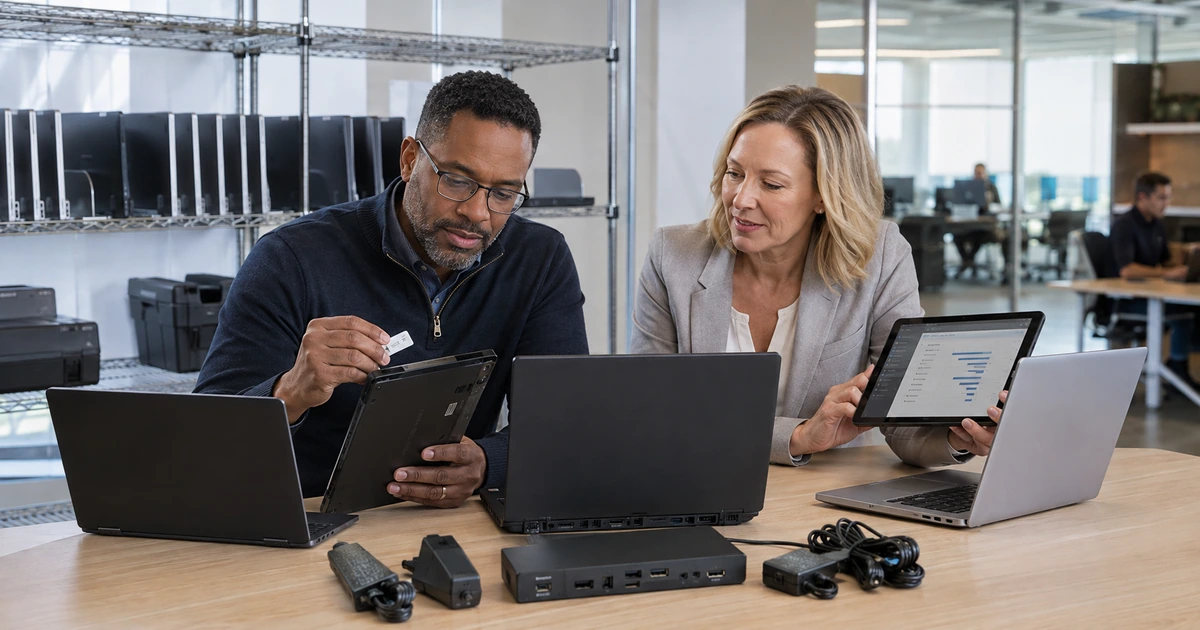
A device lifecycle plan gives a business a repeatable way to select, purchase, configure, assign, support, refresh, and retire laptops, desktops, tablets, and related equipment. Without it, purchases become emergency reactions, employees receive inconsistent systems, warranties expire unnoticed, spare capacity disappears, and old devices keep sensitive data long after they stop receiving reliable support.
The plan should begin with job requirements rather than a preferred model. A financial analyst, field technician, designer, front-desk employee, executive, and shared workstation may need different processors, memory, storage, graphics, screens, ports, durability, mobility, privacy, and support coverage. Standard profiles reduce needless variety while preserving exceptions for documented business needs. Every device should move through an accountable record from approved request to final disposition.
ALLMSP plans and operates device lifecycles in house for businesses in Lawrenceville, Suwanee, Gwinnett County, Metro Atlanta, and across Georgia. We can combine hardware selection, competitive procurement, staging, deployment, endpoint security, support, repair, warranty coordination, data migration, refresh scheduling, sanitization, and recycling under one practical process.
Design one accountable lifecycle for every company device
- Classify work: Define user and workload profiles, mobility, peripherals, durability, security, performance, and support requirements.
- Set standards: Approve device classes, configurations, operating systems, warranties, accessories, suppliers, and exception rules.
- Track custody: Maintain serial, asset tag, owner, user, location, status, dates, warranty, configuration, and financial records.
- Operate securely: Enroll, configure, patch, protect, monitor, support, repair, reassign, and recover devices through controlled procedures.
- Plan refresh: Use support life, reliability, performance, battery, repair history, risk, role, warranty, and business timing.
- Retire completely: Recover assets, protect data, remove management and identity records, sanitize media, document disposition, and recycle responsibly.
Create role-based device standards and a complete asset record
Interview business and technical owners about the work performed, applications, browser workloads, data size, display needs, video meetings, mobility, travel, field conditions, docking, printing, scanning, point-of-sale, accessibility, and expected useful life. Translate those needs into a small set of profiles such as standard office, mobile professional, performance, field, shared, and specialty. Each profile should specify minimum and target performance, operating system, management support, security capabilities, ports, wireless standards, camera and audio needs, warranty, accessories, and approved alternatives.
Standardization should reduce support complexity without blocking legitimate work. Define who can approve an exception, what evidence is required, how the exception affects software, security, repair, spares, training, and cost, and when it will be reviewed. Include purchase channels and model-change rules so a discontinued device does not prompt an unreviewed substitute. Microsoft Intune planning guidance recommends inventorying device platforms and ownership while considering supported operating systems and replacement of unsupported devices.
Maintain a lifecycle record for each asset. Include manufacturer, model, serial number, asset tag, device type, purchase order, cost, supplier, received date, warranty and support dates, assigned user, owner, department, location, status, operating system, management platform, encryption, recovery-key custody, configuration profile, accessories, repair history, data disposition, and final retirement evidence. Reconcile management data, procurement records, physical counts, and help desk records. CISA’s Cybersecurity Performance Goals include regularly updated inventories to improve visibility into managed and unmanaged assets.
- Role profile: Document applications, performance, storage, graphics, mobility, ports, displays, accessories, durability, and support needs.
- Approved standard: Set device class, minimum configuration, operating system, security features, warranty, supplier, and alternatives.
- Exception record: Preserve business reason, approver, configuration, support impact, security requirements, cost, and review date.
- Asset identity: Track serial, tag, purchase, warranty, user, owner, location, status, configuration, and management identifiers.
- Inventory reconciliation: Compare physical assets, procurement, endpoint management, directory, finance, repair, and help desk evidence.
A device standard is useful when it matches real work, limits needless variation, supports secure management, and maps every physical asset to a current owner and status.
Plan cost, availability, deployment, support, repair, and refresh as one service
Budget beyond purchase price. Include docks, displays, adapters, bags, spare chargers, warranties, accidental-damage coverage where appropriate, staging, deployment, licenses, management, security, backup, support, repair labor, temporary replacements, shipping, data migration, downtime, and retirement. Compare the cost of a longer warranty or more memory with the operational cost of early replacement and employee delay. Maintain planned purchases by quarter and hold a small approved spare pool for critical roles and predictable new hires.
Design the deployment process before the order arrives. Register or enroll supported devices, apply naming and ownership, install approved applications, configure security, encryption, updates, browsers, Wi-Fi, VPN, printers, collaboration tools, and role settings, then validate compliance. Microsoft describes the device lifecycle in Intune as enrollment, configuration, protection, and retirement. Windows Autopilot can use the manufacturer-installed Windows image and enroll organization-owned devices when the user signs in, which can reduce manual imaging when the environment and licensing support it.
Set repair and refresh decision rules. Consider support life, operating-system eligibility, warranty, age, reliability, battery health, storage health, performance under the real workload, repair history, parts availability, security features, employee impact, and replacement lead time. A device should not remain in service solely because it still powers on. Build refresh waves around business calendars, budgets, onboarding demand, and critical operations. Define temporary equipment and data continuity before taking a primary device out of service.
- Lifecycle cost: Model hardware, accessories, warranty, deployment, licenses, management, support, repair, downtime, migration, and retirement.
- Capacity plan: Forecast hiring, growth, refresh waves, failures, project demand, supplier lead time, standard models, and spare stock.
- Deployment baseline: Automate enrollment where appropriate and verify configuration, apps, security, updates, access, peripherals, and documentation.
- Repair decision: Compare failure, warranty, parts, labor, data risk, loaner need, remaining support life, and employee disruption.
- Refresh trigger: Use support status, reliability, health, performance, role, security, repair history, business timing, and total cost.
The lifecycle budget becomes credible when purchasing, deployment, support, downtime, repair, refresh, and retirement are planned together instead of appearing as unrelated emergencies.
Retire devices with account cleanup, data protection, sanitization evidence, and responsible disposition
Create a retirement ticket before the device changes custody. Record asset identity, user, reason, condition, expected destination, data sensitivity, backup or migration requirement, accessories, approvals, and responsible technician. Recover the device and confirm whether it must be preserved for legal, regulatory, insurance, or investigative reasons. Disable or remove access that should not follow the asset. Handle lost or stolen systems through the incident process rather than ordinary retirement.
Remove the device from management, identity, deployment, security, remote-support, backup, certificate, licensing, and vendor systems according to platform behavior and the intended disposition. A remote retire command may remove company configuration without erasing all data, while a wipe or reset can have different results. Microsoft documents distinct retire, wipe, delete, and reset actions, and notes that a completed server-side action may not prove the client finished. Verify the observed state and clean up persistent records such as automated deployment registration when the device permanently leaves the organization.
Choose media sanitization from data sensitivity, media type, intended reuse, device condition, and an approved organizational standard. NIST SP 800-88 Revision 2 focuses on a media sanitization program, appropriate techniques, assurance, and validation. Record the method, tool or service, device and media identifiers, operator, date, result, validation, exception, and final disposition. Reuse equipment only after configuration and data controls pass. Use responsible donation, resale, take-back, or certified recycling channels and preserve chain-of-custody and disposition records when required.
- Retirement authorization: Document asset, user, reason, condition, data, destination, legal hold, migration, approval, and custody.
- System cleanup: Remove or update management, directory, deployment, security, backup, certificates, licenses, support, and remote access.
- Sanitization decision: Select an approved method from media, sensitivity, reuse, condition, threat, validation, and applicable requirements.
- Disposition evidence: Record identifiers, custody, method, operator, date, validation, recipient, recycler, exception, and final status.
- Inventory closure: Reconcile the asset register, finance records, spare stock, user assignment, accessories, and management systems.
A device leaves the lifecycle only when its custody, company access, data, management records, financial status, and physical disposition are all verified and documented.
Complete business device lifecycle management from ALLMSP
ALLMSP can define device standards, source equipment, coordinate project timing, stage and enroll systems, migrate user data, apply security, manage inventory, provide support, coordinate repairs, maintain spares, plan refresh waves, sanitize media, and document retirement with its in-house team.
We support Windows, macOS, ChromeOS, mobile devices, workstations, laptops, displays, docks, and business accessories according to the customer’s environment. Lifecycle reporting keeps leadership informed about ownership, support status, age, health, upcoming costs, exceptions, and unresolved risk.
- Standardize: Match approved device profiles, configurations, warranties, accessories, and suppliers to real business roles.
- Operate: Track, deploy, secure, support, repair, reassign, and refresh equipment through owned procedures.
- Retire: Recover custody, remove access, protect and sanitize data, document disposition, and close every record.
Official device lifecycle references
Use current platform and security guidance as a baseline, then tailor lifecycle decisions to business roles, data, devices, support commitments, and applicable requirements.
- NIST Cybersecurity Framework 2.0. Provides outcomes for governing, identifying, protecting, detecting, responding to, and recovering from cyber risk.
- CISA Cybersecurity Performance Goals. Includes prioritized practices such as maintaining visibility into organizational technology assets.
- Microsoft Intune core concepts. Describes device enrollment, configuration, protection, compliance, application management, and retirement.
- NIST media sanitization guidance. Defines a program-oriented approach to sanitization methods, assurance, validation, and disposition.
- EPA electronics donation and recycling. Provides considerations for donation, recycling, batteries, and responsible handling of used electronics.
Business device lifecycle planning FAQs
What stages belong in a business device lifecycle?
Include requirements, approval, standards, procurement, receipt, tagging, enrollment, configuration, assignment, support, patching, repair, warranty, reassignment, refresh, recovery, access cleanup, sanitization, disposition, and record closure.
Why should device standards be based on employee roles?
Role profiles connect hardware and accessories to actual applications, mobility, performance, security, support, and working conditions, reducing waste while preserving justified exceptions for specialized work.
What information belongs in a device inventory?
Track manufacturer, model, serial, asset tag, purchase, cost, supplier, warranty, user, owner, location, status, operating system, management, encryption, configuration, accessories, repairs, data disposition, and retirement evidence.
How often should business computers be replaced?
There is no universal age. Use operating-system and vendor support, reliability, battery and storage health, workload performance, security features, repair history, warranty, employee impact, cost, and business timing.
When should a computer be repaired instead of replaced?
Compare the fault, data risk, warranty, parts and labor, expected downtime, temporary-device need, remaining support life, reliability, performance, security, and total cost against a suitable replacement.
What costs should a device budget include?
Include hardware, accessories, warranty, staging, deployment, licenses, management, security, backup, support, repairs, spares, shipping, migration, downtime, refresh, sanitization, and recycling.
What should happen when a device is reassigned?
Verify ownership approval, protect or migrate required data, remove the former user, reset or rebuild appropriately, confirm management and security, update inventory, test the role configuration, and document the new custody.
Is deleting files enough before recycling a computer?
No. Use an approved sanitization method appropriate to the media, data sensitivity, condition, and intended disposition, then validate and document the result before the asset changes custody.
Can ALLMSP manage the full device lifecycle in house?
Yes. ALLMSP can handle standards, procurement, staging, deployment, inventory, security, support, repair coordination, refresh, data migration, sanitization, and retirement with its in-house team.
Where does ALLMSP provide device lifecycle services?
ALLMSP supports organizations in Lawrenceville, Suwanee, Gwinnett County, Metro Atlanta, and throughout Georgia according to fleet size, platforms, locations, and operating needs.