Frontline access spreads across more systems than most account lists reveal. A restaurant manager may have point-of-sale, scheduling, timekeeping, email, ordering, inventory, camera, alarm, door, file, marketing, and vendor-portal access. A retail employee may use a shared terminal, handheld scanner, mobile app, discount code, badge, key, and location-specific permissions. An audit must connect those digital and physical paths to one current business identity.
The largest risks often hide in ordinary exceptions. A former manager retains access to a second location. A shared register code never changes. A contractor controls the primary profile owner. A rehire receives a duplicate account. A store transfer adds new rights without removing old ones. A badge is returned but active mobile sessions remain. The goal is not to collect screenshots of settings. It is to reconcile who should have access with who can actually use each system now.
ALLMSP performs and remediates frontline access audits through its in-house team for organizations in Lawrenceville, Suwanee, Gwinnett County, Metro Atlanta, and across Georgia. We examine identities, applications, point-of-sale, devices, badges, remote access, vendors, logs, lifecycle processes, and recovery controls across locations.
Reconcile every person, account, device, badge, and location
- Define the population: Include active workers, managers, contractors, vendors, service identities, shared access, leaves, transfers, departures, and exceptions.
- Collect each system: Export identity, point-of-sale, scheduling, email, files, inventory, ordering, cameras, networks, badges, alarms, remote access, and devices.
- Resolve identities: Match records through stable identifiers, names, locations, managers, activity, devices, and investigation of uncertain or duplicate users.
- Compare approved access: Test actual roles, functions, locations, privilege, group inheritance, temporary access, ownership, and separation of duties.
- Inspect lifecycle evidence: Sample starts, transfers, leaves, rehires, no-shows, departures, urgent removals, and asset recovery through closure.
- Remediate and retest: Disable, reduce, reassign, secure, document, reconcile, test recovery, monitor exceptions, and verify final state.
Build an identity inventory across applications, locations, devices, and physical access
Start with the authoritative active-worker and approved-exception population, then collect current users and owners from identity, email, point-of-sale, scheduling, timekeeping, inventory, ordering, delivery, loyalty, ecommerce, files, cameras, alarm, door access, remote support, network administration, marketing, analytics, and vendor portals. Add device management, tablets, scanners, phones, workstations, and badges. Capture identifier, display name, username, owner, role, groups, locations, privilege, MFA, recovery, status, creation, last activity, device, authentication method, and expiration.
Resolve records to a person or accountable service. Use stable identifiers where available and investigate name, email, manager, location, activity, device, and creation history when systems do not share one key. Identify duplicates, generic managers, shared codes, unknown owners, departed users, dormant accounts, service identities used interactively, vendor users, break-glass accounts, orphaned devices, former locations, and records that cannot be confidently matched. Do not delete uncertain evidence simply to make the report clean.
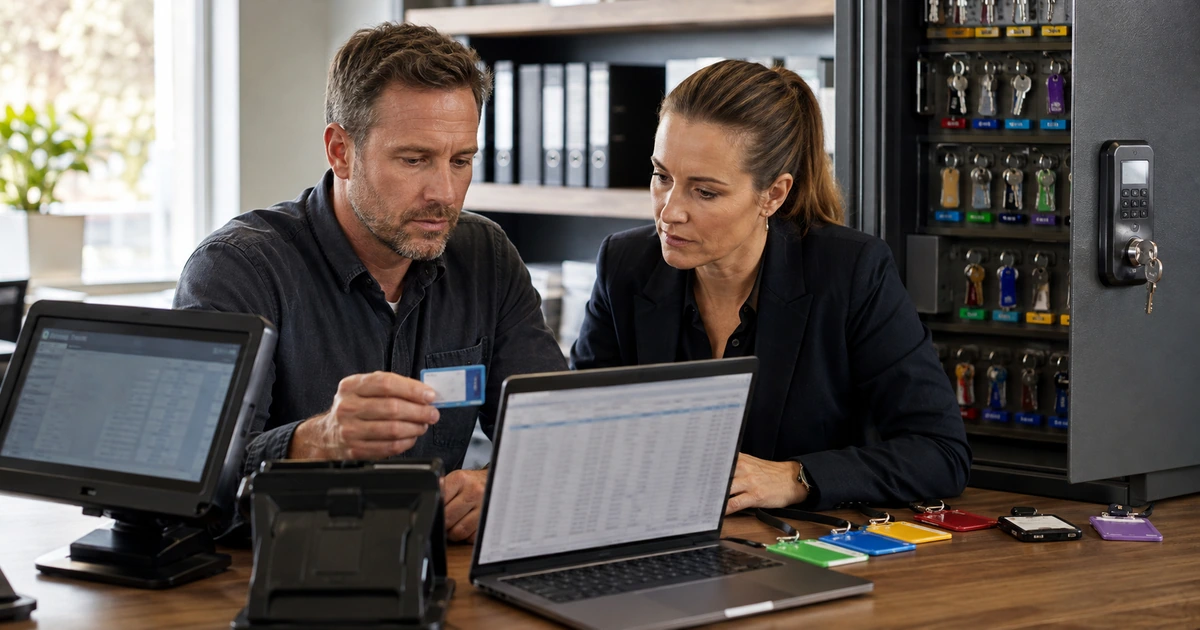
Include physical and local access that cloud exports miss. Inspect keys, badges, alarm codes, door groups, locked cabinets, network closets, payment terminals, device storage, manager tablets, paper password lists, shared browsers, saved credentials, unattended sessions, and handwritten codes near registers. Review which roles can open, refund, discount, void, adjust inventory, view reports, change menus or prices, export customer data, review cameras, administer users, or reach multiple locations. Connect each capability to an approved business responsibility.
- Population record: List active, transferred, leave, seasonal, departed, contractor, vendor, service, shared, emergency, and exception identities.
- System export: Capture account, owner, role, groups, locations, privilege, MFA, recovery, activity, status, creation, and expiration.
- Identity match: Use stable identifiers and corroborate name, manager, location, device, activity, dates, and system history.
- Physical access: Inventory badge, key, alarm, cabinet, terminal, device storage, shared browser, saved credential, and printed code exposure.
- High-risk function: Review refunds, voids, discounts, cash, inventory, exports, cameras, administration, remote access, and multiple locations.
The inventory is trustworthy only when every usable access path has a current owner or a documented exception requiring resolution.
Review role fit, MFA, shared access, vendors, and lifecycle failures
Compare each account with the current job and location profile. Investigate broad manager roles, inherited groups, access from a former location, temporary rights without expiration, unused privilege, self-approval, and conflicts between transaction and administrative duties. Confirm MFA for supported important systems and protect recovery methods. Review whether mobile applications, remembered browsers, API tokens, app passwords, and active sessions can continue after the visible account is changed. Test representative restrictions with an authorized nonproduction account.
Reduce shared access wherever named identities are supported. For unavoidable shared terminals or codes, document owner, purpose, approved users, authentication, rotation, monitoring, session behavior, physical controls, and replacement plan. Change shared credentials when membership changes and after suspected exposure. Separate vendor users from employees and require named accounts, MFA, limited locations, approved tools, logged activity, support tickets or maintenance records, expiration where possible, and prompt removal after the work or contract ends.
Sample lifecycle events against evidence. For starts, verify approved role, secure credential delivery, first-shift access, device, badge, training, and restrictions. For moves, verify new rights and removal of old ones. For leaves and departures, compare effective time with account disablement, session revocation, application removal, badge and key status, device return, shared credential changes, data handling, and manager confirmation. CISA identity guidance warns that users can accumulate privileges as roles change and recommends timely termination of accounts and rights when a relationship ends.
- Role comparison: Match job, location, manager, baseline, additions, high-risk functions, group inheritance, use, approval, and review.
- Authentication check: Review MFA, recovery, remembered sessions, app passwords, tokens, shared secrets, emergency access, and reset controls.
- Shared-access control: Document necessity, users, owner, rotation, monitoring, sign-out, physical protection, accountability, and replacement.
- Vendor boundary: Confirm company owner, named user, purpose, location and system scope, MFA, tool, schedule, logs, expiration, and removal.
- Lifecycle sample: Trace join, move, leave, rehire, temporary assignment, no-show, urgent removal, and asset return to verified closure.
An access review must test current business need and lifecycle evidence, not merely confirm that a familiar username still exists.
Prioritize remediation, test removal, strengthen recovery, and maintain evidence
Prioritize findings by current exploitability and business impact. Immediately address active former users, unknown owners, unprotected administrative accounts, default credentials, exposed remote access, excessive multi-location rights, shared high-risk credentials, unsupported systems, and accounts involved in suspicious activity. Preserve evidence before making changes when an incident may have occurred. For ordinary excess access, coordinate with the accountable manager, record the decision, remove the exact privilege, test the employee’s required work, and monitor for unintended disruption.
Test disablement and recovery controls. With authorization, use representative accounts to confirm that disabling identity blocks applications, point-of-sale, mobile sessions, remote access, VPN, email, files, and managed devices as intended. Verify badge and physical-access changes separately. Test emergency administrative access, account recovery, ownership transfer, and the ability to operate when a primary manager is unavailable. Protect recovery methods from the same compromise that might affect ordinary accounts and review every use.
Create a recurring reconciliation and event-driven review. Compare approved workers and exceptions with systems, devices, and physical access at a frequency based on risk and turnover. Trigger targeted reviews after departures, transfers, role changes, new locations, acquisitions, platform migrations, security incidents, vendor changes, and unusual activity. Track finding, affected identity, system, location, risk, owner, correction, due date, evidence, retest, exception, expiration, and final closure. Use support tickets and audit differences to improve source data, roles, integrations, and manager procedures.
- Immediate action: Secure former, unknown, default, unprotected admin, suspicious, exposed remote, and excessive multi-location access.
- Removal test: Verify identity, applications, point-of-sale, sessions, mobile access, remote tools, devices, badges, doors, and alarms.
- Recovery test: Confirm protected owner recovery, emergency administration, unavailable-manager procedures, logging, communication, and review.
- Review trigger: Start checks after departure, move, new location, migration, incident, vendor change, unusual activity, and scheduled cadence.
- Finding closure: Record identity, system, location, evidence, risk, owner, action, due date, retest, exception, expiration, and decision.
A maintained access program can show which paths were removed, which exceptions remain, who accepted them, and when they will be reviewed again.
Multi-location access audits and remediation from ALLMSP
ALLMSP can collect account and device records, reconcile identities, inspect locations, review roles, secure authentication, reduce shared access, control vendor users, trace lifecycle cases, test disablement, strengthen recovery, implement remediation, and build recurring access reviews. Our in-house team performs both the assessment and technical corrections.
We help retailers and restaurants in Lawrenceville, Suwanee, Gwinnett County, Metro Atlanta, and throughout Georgia understand and control frontline access across one location or a complex multi-site operation.
- Discover: Inventory workers, systems, roles, locations, applications, devices, badges, shared access, vendors, sessions, and exceptions.
- Correct: Remove stale rights, secure accounts, reduce privilege, repair lifecycle workflows, recover assets, and document decisions.
- Maintain: Reconcile records, test disablement, review events, monitor exceptions, improve source data, and report closure evidence.
Official identity governance and account references
Use these resources with current application documentation and applicable organizational, employment, privacy, security, legal, and recordkeeping requirements.
- CISA identity and access management practices. Provides recommendations for governance, account administration, authentication, lifecycle management, and access review.
- CISA multifactor authentication guidance. Explains stronger authentication for important business, remote, email, and storage systems.
- Microsoft Entra lifecycle workflows. Describes joiner, mover, and leaver tasks, automated access changes, workflow history, and audit logs.
- NIST subscriber account guidance. Addresses account access, suspension, termination, notification, and lifecycle handling.
Frontline access audit FAQs
Which systems belong in a retail or restaurant access audit?
Include identity, email, point-of-sale, scheduling, timekeeping, inventory, ordering, files, cameras, alarms, doors, networks, remote support, marketing, vendor portals, devices, badges, and shared credentials.
How are accounts matched when systems use different usernames?
Use stable identifiers where possible, then corroborate name, email, manager, location, device, activity, creation dates, employment events, and system history.
What should happen to access after a store transfer?
Add only the approved destination duties, remove rights from the prior location that are no longer needed, set temporary expiration, and test the complete result.
Are shared register codes acceptable?
Prefer named identities. When a system requires shared access, document necessity, authorized users, rotation, monitoring, sign-out, physical controls, accountability, and replacement plans.
How should vendor accounts be controlled?
Use company ownership, named users, MFA, exact purpose, limited locations and systems, approved access tools, logs, maintenance records, expiration, review, and removal.
Does disabling the main identity end every active session?
Not always. Test applications, mobile sessions, remembered browsers, tokens, app passwords, remote tools, VPN, point-of-sale, devices, and physical access separately.
Which access findings require immediate action?
Prioritize active former users, unknown owners, default credentials, weak administrative accounts, exposed remote access, suspicious activity, and excessive high-risk privileges.
How often should frontline access be reconciled?
Use a risk-based schedule and trigger additional reviews after departures, transfers, role changes, incidents, new locations, migrations, and vendor changes.
Can ALLMSP remediate findings instead of only reporting them?
Yes. ALLMSP secures accounts, removes rights, repairs workflows, configures MFA, reconciles devices, tests removal, and maintains the program through its in-house team.
Where does ALLMSP provide multi-location access audits?
ALLMSP serves Lawrenceville, Suwanee, Gwinnett County, Metro Atlanta, and retail and restaurant organizations throughout Georgia.