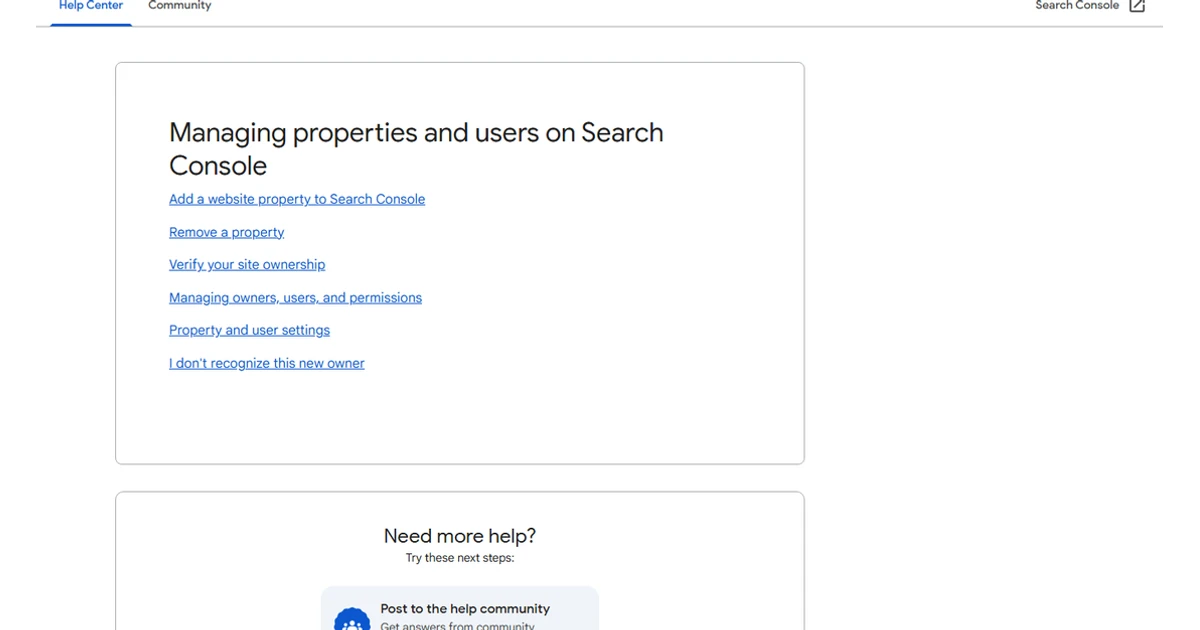
Removing a former provider from the Search Console user list may leave a route for that person to verify ownership again. A safe access review checks both the people listed in the property and the verification methods behind ownership.[1]
Start by establishing working company ownership. Then remove access that no longer has a business purpose, address the associated verification dependencies, and confirm that the company and its current provider can still do their jobs. This is especially useful before a website migration, agency change, or employee departure.
First, establish who can keep the company in control
Open the exact property used for reporting and inspect Settings, then Users and permissions. Record the account, role, business reason, and person who approved each grant. If you cannot see the user list, ask a property owner to perform the review with you.[1]
| Permission | What distinguishes it | Your review question |
|---|---|---|
| Verified owner | Proved ownership through a verification method | Does the company control a valid ownership route? |
| Delegated owner | Received owner status through another owner | Is owner-level control necessary for this person? |
| Full user | Can view data and take some actions | Which operational tasks require this access? |
| Restricted user | Has limited viewing access | Would this meet the person’s reporting need? |
These are different permission levels.[1] Choose the least access that supports an agreed task and test that task after a change. Keep a responsible company contact and a recovery path in the handover record; do not make an external provider’s personal account the only practical route back in.
Trace verification to the system that actually controls it
For each owner being removed, inspect Ownership verification details and the unused ownership tokens list. Record the relevant method, token location, and administrator who can change it. Verification can depend on DNS, an HTML file or tag, or eligible Analytics or Tag Manager access.[2]
Use a small dependency register rather than a screenshot of names alone:
- Property: the precise domain or URL prefix, including any important parent property.
- Account and method: who owns the token and how verification is established.
- Change location: the active DNS zone, website file, template setting, Analytics account, or Tag Manager container.
- Other dependencies: whether the proposed change could affect another verified service or a live tracking deployment.
- Replacement and test: who will retain ownership and how continuity will be confirmed.
A token can have uses beyond this property. Check its dependencies before deleting it; a broad DNS cleanup or removal of a live tracking tag can create a separate problem.[1] If the company lacks a verified property, use the Search Console setup guide before scheduling the old provider’s removal.
Remove the right access route in a controlled sequence
Agree on the scope and timing with the authorized company contact. Capture the current permissions and relevant configuration, confirm replacement ownership, and make each change in the system that controls it. Do not remove an entire tracking deployment merely to solve one person’s access problem.
| Access being retired | What needs attention |
|---|---|
| User or delegated owner | Remove the grant in Search Console and confirm the intended remaining permissions. |
| Verified owner | Remove access, then address every verification route associated with that person so it cannot restore ownership. |
| Analytics-based verification | Review the person’s qualifying Analytics edit access as part of revoking that verification route. |
| Tag Manager-based verification | Review the person’s qualifying Publish or Admin access in the relevant account. |
Google’s permission guide explains these different removal mechanisms.[1] For a DNS record, file, or meta tag, identify the departing person’s exact token before removing it. Keep the replacement company’s verification intact.
For example, if an agency verified a URL-prefix property through a tag it installed, removing its Search Console entry alone is an incomplete handover. The next step is to identify that specific verification dependency and remove the agency’s route while preserving working company ownership. This is an illustrative scenario, not a claim about a particular customer.
Test the handover, including the work people still need to do
After the changes, have the company owner open the correct property and confirm its verification. Have the current provider test the agreed reporting or operational task. Review ownership history and unused tokens for anything left unresolved. Keep an exception list if a dependency requires a later approved change.
Also check connected working arrangements: who receives alerts, who prepares reports, where exports are stored, and who responds when an important page has an indexing problem. Access is only useful when someone owns the follow-up.
If an owner is unfamiliar or access unexpectedly returns, investigate the underlying website and account controls rather than repeatedly deleting the visible entry. An account that can alter the site or verification configuration may be able to reintroduce a token. Treat that as a separate security investigation.[1]
Once the handover is complete, use the service-page improvement workflow to give the retained reporting access a clear purpose. For help tracing verification dependencies or documenting the transition, contact ALLMSP through software support.
Frequently asked questions
Is removing a Search Console user enough to end verified ownership?
Not necessarily. A remaining verification route can let a removed verified owner establish ownership again. Review and retire the relevant verification methods as well as the visible access grant.
[1]What is the difference between a verified owner and a delegated owner?
A verified owner proved ownership through a verification method. A delegated owner received owner status through another owner. The distinction matters when deciding how access must be removed.
[1]Should an agency always have owner permissions?
No. Match access to the work it has been authorized to do. Review the required tasks, choose an appropriate role, and confirm those tasks still work after any change.
What should happen before the only verified owner leaves?
Establish and test replacement company ownership before the departure. Record its verification dependency and the responsible company contact so access can be maintained.
[2]Where can I check how an owner verified the property?
Review Ownership verification details and unused ownership tokens in the property settings. Record the method and exact change location before retiring it.
[1]Can I remove every Google verification record from DNS?
Do not remove records indiscriminately. Identify the departing account’s token, check other service dependencies, and preserve working company verification.
[2]Why should Analytics and Tag Manager access be reviewed too?
Eligible permissions in those systems can support verification. Include them in the dependency review when that method was used, without removing unrelated tracking that the business still needs.
[2]Will an ownership change improve search rankings?
Do not expect a ranking gain from an access cleanup. Its purpose is continuity, appropriate control, and accountability for the work done through Search Console.
What should I do about an owner nobody recognizes?
Confirm whether the account has an authorized business purpose. If it does not, investigate account and website controls as well as its verification route, and involve the responsible security administrator.
What is a useful final handover record?
Keep the property, current company owner, approved users and roles, verification dependencies, changes made, tests completed, unresolved exceptions, and the person responsible for alerts and reporting.