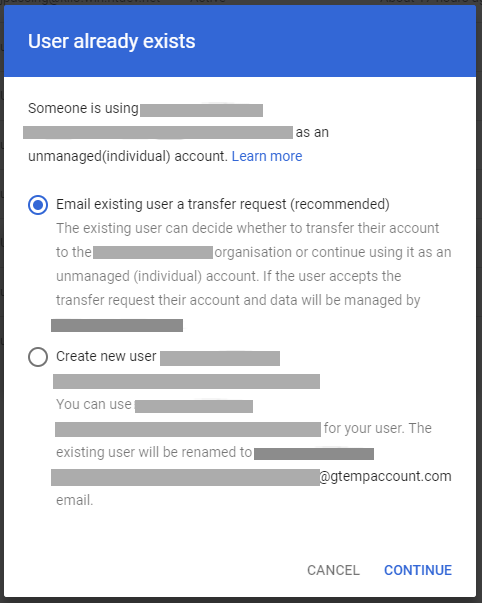
Google’s documented account-conflict dialog illustrates that a company email address does not by itself make an account company-managed. Review transfer, data and recovery responsibilities with the account owner before changing identities.[12]
A business can use Google Workspace, Ads, Analytics, Tag Manager, Search Console, Business Profile, YouTube, Merchant Center, and Google Cloud while still lacking dependable control of those services. Each product has its own owners, administrators, invitations, recovery methods, and linked accounts. A reliable setup gives the company at least two tested paths into every critical asset and documents how the services exchange data.
Do not remove an existing owner, verification token, manager account, service account, or website tag while establishing control. First capture the current state, add company-controlled access, test it in a separate session, and confirm that reporting, advertising, listings, video, commerce, and automated processes still work. Ownership cleanup should be a controlled migration with a rollback record.
ALLMSP handles business software deployment and configuration to teams near Lawrenceville and Suwanee, elsewhere in Gwinnett County and Metro Atlanta, and throughout Georgia, with planning, configuration, testing, and support completed by the same in-house team.
What a dependable Google account ecosystem setup should accomplish
A dependable Google account ecosystem lets an authorized employee find every important asset, identify who controls it, recover access without a former employee or vendor, trace marketing data from the website to the correct reports, and transfer responsibility without interrupting operations. Personal accounts may participate only when the business has explicitly approved the need and retained independent control.
- Every Google asset has a recorded account ID, URL, purpose, business owner, technical owner, billing contact, and recovery path.
- Critical services have at least two tested company-controlled administrators using individual accounts and strong 2-Step Verification.
- Google Workspace users, groups, organizational units, Shared drives, and offboarding rules support business continuity.
- Ads, GA4, Tag Manager, Search Console, Business Profile, YouTube, and Merchant Center links are documented and tested.
- OAuth applications, service accounts, API keys, scripts, website tags, and verification methods have named owners and limited access.
- Recovery, billing, alerts, change records, and quarterly review dates are stored where current administrators can use them.
Build the identity and asset foundation
1. Create the Google asset register
List every organization, domain, customer ID, account, property, data stream, container, website property, location group, channel, merchant account, project, billing account, and production integration. Record the exact identifier and URL because similar display names can hide duplicate or abandoned assets.
Where to work: Workspace Admin console, Ads account switcher, Analytics Admin, Tag Manager, Search Console, Business Profile Manager, YouTube Studio, Merchant Center, and Cloud console
Verification: A second administrator can open every listed asset from the register and can identify any account that appears in a product switcher but has no documented purpose.
2. Establish company-controlled administrator identities
Create named administrator accounts on a company-controlled domain, protect them with phishing-resistant 2-Step Verification where possible, and keep daily work separate from emergency administration. Assign the lowest role needed for routine work and reserve super administrator access for a small tested group.
Where to work: Admin console > Directory > Users, then Account > Admin roles
Verification: At least two authorized people can sign in independently, complete a privileged task, receive a security alert, and use the documented recovery path without sharing a password.
3. Design users, groups, and organizational units
Align users with employment status, department, location, and access need. Use groups for shared communication and role-based access. Use organizational units only where service settings truly differ. Document naming, aliases, delegated mailboxes, suspended users, and the offboarding owner.
Where to work: Admin console > Directory > Users, Groups, and Organizational units
Verification: Test a normal employee, manager, mobile user, outside collaborator, and departing employee scenario. Each receives the intended services and loses access according to the documented rule.
Establish product ownership and trusted data connections
1. Move durable files into Shared drives
Place team-owned procedures, client deliverables, marketing assets, finance records, and other durable work in appropriately restricted Shared drives. Assign managers, content managers, contributors, commenters, and viewers according to actual responsibility. Keep personal My Drive ownership for genuinely individual working files.
Where to work: Google Drive > Shared drives and Admin console > Apps > Google Workspace > Drive and Docs
Verification: A file created by one employee remains available to the authorized team after that employee is suspended, and external sharing follows the intended restriction.
2. Set up Ads ownership and billing continuity
Confirm the correct customer ID, business-controlled administrators, manager accounts, payments profile, billing contacts, conversion owners, and linked Analytics or Merchant Center accounts. Give agencies and specialists individual or manager-account access instead of a shared login.
Where to work: Google Ads > Admin > Access and security, Managers, Billing, and Linked accounts
Verification: A company administrator can review campaigns, billing, linked accounts, conversions, and change history, while an outside provider can be removed without locking out the business.
3. Connect GA4 and Tag Manager with deliberate permissions
Use the correct Analytics account and GA4 property, create the intended web data stream, document data retention and internal traffic rules, and assign account or property roles narrowly. In Tag Manager, separate read, edit, approve, and publish authority, then document which container and workspace deploy production tags.
Where to work: Google Analytics > Admin > Account and Property access management, then Google Tag Manager > Admin > User Management
Verification: Submit a real test lead and trace it through Tag Assistant, Tag Manager preview, GA4 Realtime or DebugView, the key event, and the linked Ads conversion without duplicate firing.
4. Verify Search Console with a durable method
Create a Domain property using company-controlled DNS verification when full-domain coverage is needed. Other verification methods apply to supported URL-prefix properties, not as a second method for the Domain property. Keep valid verification records, add tested company-controlled owners, submit the canonical sitemap, and connect the correct GA4 property only when the reporting workflow needs it. [8]
Where to work: Google Search Console > property selector > Add property, then Settings > Ownership verification and Users and permissions
Verification: Two company owners can open the property, view indexing and performance reports, use URL Inspection, and explain which verification method preserves access.
Control automation, billing, and business continuity
1. Secure Business Profile, YouTube, and Merchant Center
Confirm the exact locations, channel or Brand Account, and merchant account the business uses. Add company-controlled primary ownership and backup access, remove pending invitations that are no longer needed, and document connected Ads accounts, product feeds, websites, phone numbers, and public response responsibilities.
Where to work: Business Profile settings > People and access, YouTube Studio > Settings > Permissions, and Merchant Center > Settings > People and access
Verification: Authorized staff can update a location, review a channel permission, inspect a product issue, and reach support without using a former employee’s or vendor’s personal account.
2. Inventory Cloud, OAuth, service accounts, and API keys
Record organizations, folders, projects, billing accounts, APIs, OAuth clients, service accounts, keys, workload identities, and applications that use them. Replace broad basic roles and long-lived keys where practical. Give every production credential a named system owner, purpose, rotation or expiration rule, and incident contact.
Where to work: Google Cloud console > IAM & Admin, APIs & Services, Service Accounts, Credentials, and Billing
Verification: A reviewer can map each active credential to a production system, identify its permissions and billing project, and disable a test credential without affecting unrelated services.
3. Document recovery, billing, alerts, and change control
Document recovery phones and emails, backup codes, security keys, billing contacts, card or invoice ownership, alert recipients, support paths, emergency administrators, maintenance windows, and rollback instructions. Store sensitive recovery material in an approved protected system rather than a shared document.
Where to work: Security settings, product notification settings, billing profiles, company password manager, help desk, and change records
Verification: Run a tabletop test for a departed administrator, failed payment, lost security key, suspended listing, broken conversion tag, and compromised OAuth application. The assigned people can follow the written procedure.
Test the ecosystem before setup is complete
Use real evidence for final testing. Sign in with both company administrators, open each product, verify ownership, review billing and alerts, publish a controlled Tag Manager change, submit a real lead, inspect Search Console, update a test Business Profile detail where appropriate, and verify that emergency documentation works without verbal coaching. Record the date, tester, result, and any exception.
- Independent administrator access: Have each backup administrator sign in from a clean browser session and open every critical product. Pass: Both administrators reach the intended asset and privileged controls without a shared credential or personal recovery dependency.
- Lead data path: Submit a real test conversion from the website and trace the event through Tag Manager, GA4, Ads, and the receiving system. Pass: One qualified action appears once in each intended destination with correct source and campaign context.
- Website ownership: Inspect Search Console owners, verification methods, sitemap status, and URL Inspection for a current service page. Pass: The company retains two owners and a durable verification method, and the canonical page can be inspected.
- Local and commerce continuity: Open Business Profile and Merchant Center using the documented company accounts and review alerts, linked assets, and public data. Pass: Authorized users can act on location and product issues without an outside account.
- Automation ownership: Select one OAuth client, service account, API key, Apps Script, and website tag and trace each to its system and owner. Pass: Every selected automation has a documented purpose, limited access, support owner, and recovery action.
- Administrator departure: Run a tabletop exercise in which the primary administrator leaves without transferring knowledge. Pass: The backup team retains access, billing, alerts, files, recovery, and operational documentation across products.
A Google sign-in is not the same as product control
Use this handover checklist with exact asset IDs and independent company-controlled accounts. [1] [8] [9] [10] [11]
On a narrow screen, scroll the table horizontally to read every column.
| Asset | Control to verify | Common mistaken assumption |
|---|---|---|
| Workspace | Delegated roles, emergency administration and recovery | Workspace admin automatically owns every Google product. |
| Ads and billing | Customer access, manager relationship and payment permissions | Campaign access includes payment ownership. |
| Search Console | Valid company verification and owners | Removing a user also removes their DNS or HTML token. |
| YouTube and local profiles | Channel/profile roles plus underlying ownership | A content manager role transfers the underlying account. |
Choose the next step
- Who Controls Your Google Accounts? A Practical Access Audit — Audit effective owners and backup access across the current accounts.
- Fix Google Account Ownership, Recovery, and Data Connections — Use a controlled repair sequence for gaps found during the handover test.
Frequently Asked Questions
What should a Google business account inventory include?
Record each product's exact account or resource ID, URL, purpose, company owner, backup administrator and recovery path. Include domains and DNS, Workspace, marketing accounts, Cloud projects, billing, OAuth applications, scripts and production tags. Add linked accounts and outside-provider access so dependencies are visible. Store recovery secrets separately in an approved protected system; the inventory should explain where authorized staff can retrieve them without becoming a public list of credentials.
How many administrators should a Google business environment have?
Maintain at least two tested company-controlled administrative paths for critical services, using individual identities and strong authentication. This is a continuity design recommendation, not a reason to make everyone a Workspace super administrator. Delegate routine tasks through narrower roles, keep emergency access tightly controlled and ensure each relevant product has its own backup access. Being a Workspace administrator does not automatically grant ownership of Ads, Analytics or a YouTube channel.
How should Google Workspace users and groups be organized?
Use named user accounts for people, controlled groups for durable membership and organizational units where service policy needs to differ. Document who approves additions, role changes and removals. A group used for Cloud or file access needs a membership owner, not just a convenient email address. Test a joiner, role change and leaver so the structure supports the employee lifecycle rather than only looking tidy in the directory.
Supporting sources: [2]
Why should important company files use Google Shared drives?
Shared-drive files belong to the organization and remain when a creator leaves, which makes them suitable for durable team records. My Drive ownership remains tied to an individual and needs a transfer plan. Choose a restricted drive whose members should see that content, then test sharing and workflow dependencies before moving it. Do not assume that copying a shortcut or sharing a My Drive folder changes the underlying file's ownership.
How should a company control its Google Ads account?
Confirm the exact Ads customer ID and retain tested company-controlled administrators, billing contacts and access to conversion settings. Give the agency its own user or manager-account access, then review that manager's rights and any ownership relationship. Account administration, manager ownership and payments permissions are distinct. Test the company's independent access before removing a provider, and preserve necessary tag and CRM integrations during the handover.
How should Google Analytics and Tag Manager access be set up?
Assign Analytics access at the account or property scope required for the job, and review inherited access. In Tag Manager, keep account administration and container Read, Edit, Approve and Publish rights deliberate; a reporting user rarely needs production publishing. Document the live container and Measurement ID, plus a backup publisher and rollback version. Product ownership should be tested by opening the correct asset, not inferred from a successful Google sign-in.
Supporting sources: [3]
What is the best way to set up Google Search Console ownership?
Use a Domain property with company-controlled DNS verification when full-domain coverage is needed. A URL-prefix property can use other supported methods, but an HTML tag is not a second verification method for a Domain property. Keep the valid DNS record in place and add tested company-controlled owners. During provider removal, inspect that provider's verification tokens too; deleting an owner from the user list alone may let a still-valid token restore ownership.
How should Google Business Profile, YouTube, and Merchant Center ownership be protected?
Review each product separately: Business Profile owners and managers, YouTube channel permissions and any Brand Account ownership, and Merchant Center administrators and connected assets. Retain company-controlled primary control and a backup, with individual accounts instead of shared passwords. Transfers can have prerequisites or waiting restrictions, so confirm the new owner's actual authority before removing the old one. Channel permissions should not be mistaken for transferring Brand Account ownership.
Which Google Cloud credentials belong in an account ecosystem inventory?
Include service accounts, who can impersonate them, downloaded keys, workload-identity providers, OAuth client IDs, API keys and the applications using them. Record the owning project, scope, business purpose, support owner and replacement or rotation process. An API key and a service-account private key are different credentials with different controls. Never paste secrets into the inventory; record protected storage locations and test replacement on an isolated integration before retiring production access.
Supporting sources: [1]
What recovery documentation should be created for Google business accounts?
Document independent administrator access, protected recovery factors, domain and billing ownership, alert recipients, product-specific recovery steps and the person authorized to act. Include the account IDs and support evidence needed during a lockout, plus a provider-departure checklist. Keep backup codes and secrets in protected storage with an access procedure. Rehearse a lost security key or unavailable administrator; a document that only the locked-out person can open is not a recovery path.
Sources
- Google Workspace administrator privilege definitions. Official definitions for delegated administrator privileges and the controls available to each role, with the planning steps on this page applying it to the work needed to build company-owned access across every google business account. ↩
- Assign specific Google Workspace administrator roles. Official steps for assigning prebuilt or custom roles to users and groups with appropriate scope, with the configuration checks here applied to the controls needed to build company-owned access across every google business account. ↩
- Manage users and permissions. Tag Manager account and container permissions; distinct Read/Edit/Approve/Publish access. ↩
- Manage access to your Google Ads account. Individual account invitations, backup administrators and safe removal. ↩
- Troubleshoot issues with shared drives. Forms with file-upload questions are unsupported in shared drives; desktop editing requires appropriate role. ↩
- Add files and folders to a shared drive. Migration permissions, file ownership and changes in inherited access. ↩
- About access levels in your Google Ads account. Account roles, billing capabilities and payments-profile user management limits. ↩
- Verify your site ownership. Domain properties require DNS verification; keep verification records and establish controlled ownership. ↩
- Remove a property. Removing a verified owner requires removing their verification token to prevent regaining ownership. ↩
- Manage owners and managers of your Business Profile. Profile owners and managers use separate accounts; new-owner waiting restrictions. ↩
- Add or remove access to your YouTube channel with channel permissions. Channel permissions versus Brand Account ownership; role-based access without shared credentials. ↩
- Evict consumer accounts — account-conflict background ↩