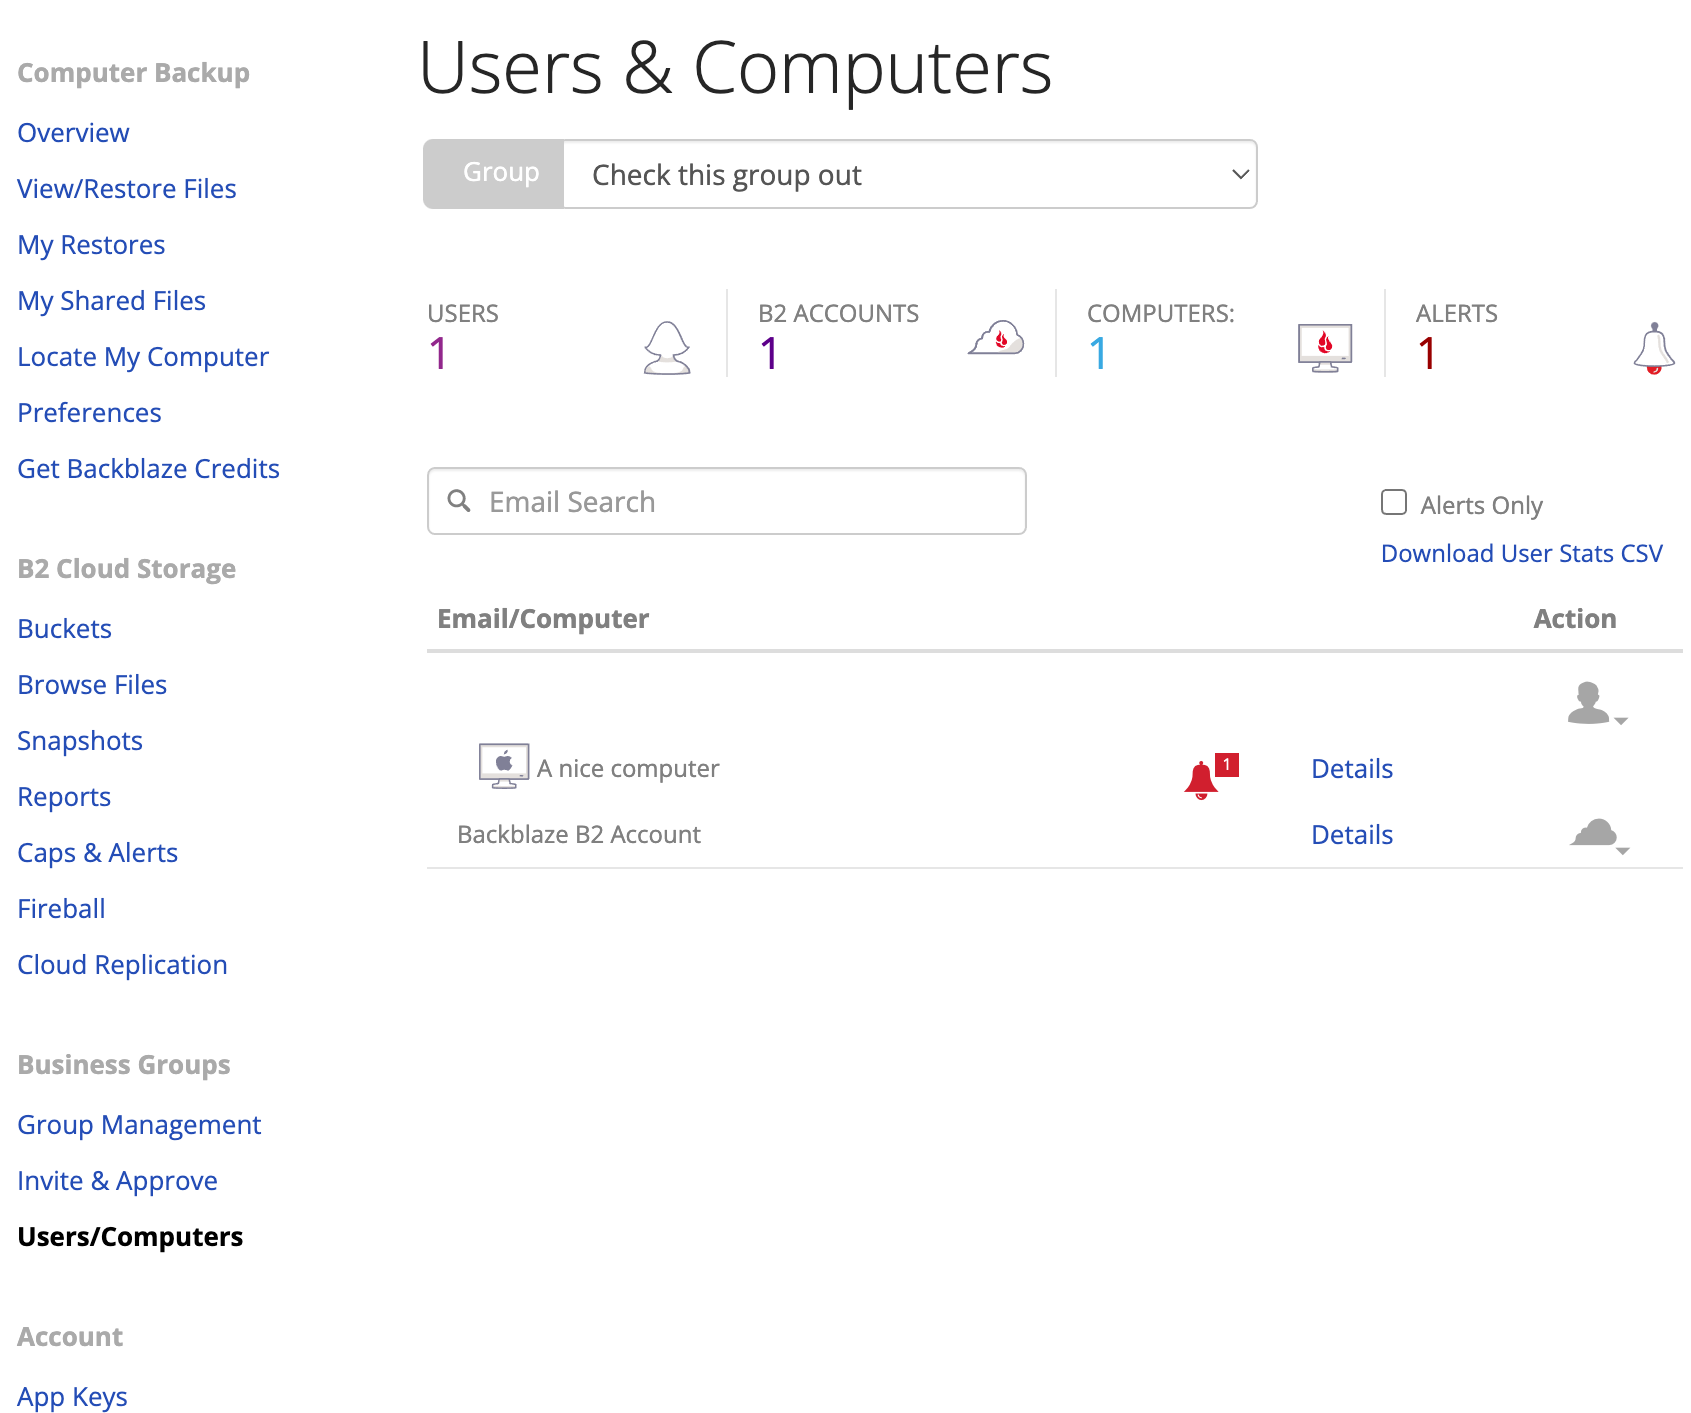
Backblaze’s published Users and Computers example separates one user, one B2 account and one computer, with an alert on the computer and a User Stats CSV option. Reconcile the actual endpoint inventory and restore evidence; this historical interface example does not prove a completed rollout.[10] View full-size image
A successful Backblaze installation is not yet a protected endpoint. First match each expected computer to the correct account and group, confirm that its required local files are eligible and selected, then restore a small approved sample. A missing device, an unselected external drive or a NAS share outside Computer Backup must remain an explicit exception instead of disappearing from the coverage count.
Use this guide to separate Computer Backup from B2 workloads, approve managed access, pilot silent deployment and reconcile the fleet before handoff. The example below deliberately holds back two plausible-looking pilot records. It is an illustrative acceptance exercise, not a client result.
Deployment should then proceed through a representative pilot that proves both installation and backup behavior. Include current Windows and macOS devices, laptops that sleep or travel, an external drive owner, large and frequently changing files, locally stored email, and at least one unsupported workload that must be routed to B2 instead. The rollout is accepted only when the organization can show which devices are enrolled, which data is eligible, whether the initial backup is progressing, and whether selected files can actually be restored.
ALLMSP handles Backblaze Business Backup deployment and configuration to teams near Lawrenceville and Suwanee, elsewhere in Gwinnett County and Metro Atlanta, and throughout Georgia, with planning, configuration, testing, and support completed by the same in-house team.
Key decisions at a glance
- Classify every workload before licensing because Computer Backup covers supported local Windows and Mac endpoint data, while NAS and server protection generally use Backblaze B2 with an integration.
- Decide managed versus unmanaged administration before creating the Business Group because the administrative-privilege choice cannot be changed afterward.
- Select centralized or decentralized endpoint ownership deliberately, choose the correct data region, and store Group ID and Group Token values only in secured deployment tooling.
- Pilot current Windows and macOS clients with required permissions, stable network access, awake endpoints, attached external drives, and realistic open-file behavior.
- Accept a rollout from device inventory, client state, backup progress, alert resolution, sampled-file evidence, and restore results rather than installer exit codes alone.
Separate Computer Backup endpoints from B2, NAS, and server workflows
Build a source inventory with one row per computer, external drive, server, NAS share, network volume, SaaS export, and application database. For each row, record the owner, operating system, physical location, data region requirement, data volume, growth rate, sensitivity, recovery objective, network path, and authoritative source. Route local Windows and Mac user data to the Computer Backup evaluation. Route NAS, server, network-mounted, and remotely mounted sources to a separate B2 integration design instead of implying that installing the endpoint client will protect them.
Review supported and excluded data on the pilot machines. Backblaze Computer Backup operates as a background service and can protect local data across user profiles, along with internal and selected USB or FireWire drives. Operating-system files, applications, caches, temporary files, empty directories, many virtual-drive formats, Time Machine data, symlinks, and network shares have documented limits or exclusions. An eligibility register should identify any business-critical data that lives in those areas and assign an alternate protection method before rollout approval.
Keep the B2 path operationally distinct. Backblaze B2 is object storage reached through its web interface, APIs, command-line tools, and integrations, it does not include the Computer Backup endpoint client. A NAS or server workflow therefore needs its own bucket, application key, integration configuration, retention, immutability, monitoring, cost, and restore tests. The Computer Backup project may reference that parallel design, but its endpoint license count and coverage reports must never be presented as evidence that B2-protected systems are healthy.
Check the supported-data reference for the actual local-drive and exclusion boundaries.[8] B2 integrations need their own storage, credential, monitoring and restore design; they are not Computer Backup endpoint successes.[9]
Lock the Business Group, administration, account, and region decisions
Decide whether each population needs a Business Group and whether that group should be managed. A small business with several computers under one account may not require multiple user accounts or a group, while organizations with separate users often value central billing, invitations, and reporting. In a managed group, administrators can browse data, create restores, and act on a member’s account. Record the lawful business purpose, least-privilege rationale, privacy notice, approvers, and recovery use case for that authority.
Treat group creation as a control gate. Backblaze documents that the administrative-privilege setting cannot be changed after creation, and a product added to a group cannot later be removed. Choose Computer Backup, B2, or both only after the service boundary is approved. Also select a restricted or domain-based join policy that matches identity governance. A publicly exposed automatic-approval invitation can create unexpected members and charges, so keep invitation links in approved channels and reconcile every accepted account.
Choose centralized or decentralized endpoint ownership and region deliberately. In a decentralized deployment, each endpoint uses its own related account and the user can access their data, subject to group administration. In a centralized deployment, endpoints share an IT-managed account and users must request their data from its manager. Record which model applies per population, how email values are supplied, who can initiate restores, and how the chosen region is passed and verified before production data begins uploading.
The group-creation reference makes the managed-access choice irreversible and describes the optional User Stats CSV.[1] The Business Groups reference explains the shared billing and member-account model; record the product and administrative scope before enrollment.[2]
The documented managed-group upgrade to Enterprise Control is a separate vendor-granted path; it is not an unrestricted managed/unmanaged toggle.[12]
Pilot secure silent deployment on current Windows and macOS devices
Download current installers from official Backblaze locations and use the platform-specific silent-install instructions. Windows MSI delivery and the Mac installer workflow have different configuration and identity prerequisites; an old command copied from a ticket is not a tested deployment design. Keep enrollment tokens in secured deployment variables, restrict who can retrieve them and avoid logging or screenshotting their values. After suspected exposure, ask Backblaze for the supported containment and enrollment-credential replacement procedure, then reconcile devices; do not assume an undocumented rotation command exists.
On macOS, pre-stage the current privacy and background-service profiles. Backblaze’s centralized Jamf guidance identifies Full Disk Access, a background or menu component profile, Managed Login Items for newer macOS versions, and optional environment-specific profiles. The current v10 workflow uses a Jamf policy, a JSON bootstrap configuration, `bzCLI`, extension attributes, and Smart Computer Groups to report state and trigger remediation. Validate those artifacts on each supported macOS release and confirm that the service remains active after reboot and update.
Pilot both ownership models where they are required. Confirm installation, assignment to the intended group and region, displayed computer identity, service state, client version, privacy permissions, backup schedule, exclusions, encryption state, and uninstall behavior. A successful installer message is only deployment evidence. The acceptance record must also show that the correct account owns the computer, no duplicate computer was created unexpectedly, all intended drives appear, and management telemetry agrees with the endpoint.
Follow the current silent-install overview,[3] then use the Windows[4] or Mac[5] procedure for the platform in scope. The centralized Jamf guide describes the v10 bootstrap, bzCLI and inventory-based compliance workflow; it does not make an installer result a restore test.[6]
Prove initial-backup readiness and convert rollout data into coverage evidence
Prepare endpoints for the initial backup. Backblaze recommends keeping the computer powered on, awake, and connected to a stable internet service. Files locked by another application cannot be backed up at that moment, so pilot locally stored email, finance databases, design files, and other frequently open content with the responsible application closed. Backblaze says the initial backup should be able to complete within thirty days, if the estimate exceeds that window, engage support instead of silently accepting permanent backlog.
Handle external drives as active sources, not archives. Confirm that each intended directly attached drive is supported and selected, keep it connected for regular scanning and prove that a recent sample reaches the backup. The older general best-practices page recommends a four-hour continuous run with all drives attached at least every two weeks; that is a useful operating check, not the retention rule for every configuration. Use the newer External Hard Drives guidance for the actual 30-day or one-year setting and its different missing-drive alerts. Neither a current online listing nor a longer history authorizes deleting the only original.
Create an acceptance dashboard from the Business Group Users/Computers view, client state, endpoint-management telemetry, and sampled restores. Track expected and discovered devices, account owner, region, last backup, remaining files, alerts, selected external drives, exclusions, version-history setting, encryption state, first successful sample restore, and exception owner. Backblaze can email administrators summary information and attach a User Stats CSV. Reconcile that report with the authoritative endpoint inventory so a missing computer cannot disappear from the denominator.
The general best-practices guide supports awake, connected initial backups and recurring sample restores.[7] Apply the newer external-drive guide when deciding what a disconnected drive’s selected history retains.[11] In the administration example, Computer Details can lag the endpoint; compare it with current client evidence and the authoritative inventory.[10]
Worked pilot: three endpoints and one NAS are not four accepted backups
This hypothetical register shows acceptance decisions, not measured client results. The endpoint denominator is three; the NAS is a separate workload with a different protection owner.
| Expected source | Observed pilot evidence | Acceptance decision | Next proof |
|---|---|---|---|
| Finance laptop | Correct account and group; required local sample appears and opens after a controlled restore | Accept the tested scope | Record the sample, date, operator and exceptions; do not imply all files were tested |
| Design Mac | Installer succeeded but required privacy permission and a fresh sample are unverified | Hold endpoint acceptance | Check supported permissions and file selection, then verify upload and restore |
| Field laptop with external drive | Laptop reports activity; the required drive has been absent for 36 days under a recorded 30-day setting | Treat the drive as a recovery risk | Inspect retained dates immediately, prepare any needed restore and escalate missing data; a later history upgrade cannot resurrect cleared versions |
| Office NAS share | A nearby workstation is backed up, but the share is outside Computer Backup | Keep outside the endpoint-success count | Link a separate B2 integration or other supported backup and its own restore evidence |
Before granting managed access, use the Backblaze administration and offboarding review. Before accepting the rollout, complete the Backblaze retention and recovery test for the actual account, drives and restore method.
Official product documentation and ALLMSP resources
Frequently Asked Questions
What should a Backblaze Business Backup rollout decide first?
Classify workloads before selecting licenses. Confirm which supported Windows and Mac computers and direct-attached drives belong in Computer Backup, then route NAS, server, network-mounted, and application-specific data to a separate Backblaze B2 integration or another approved protection method with its own recovery evidence.
Is Backblaze Computer Backup the same product as Backblaze B2?
No. Computer Backup is the managed endpoint backup service for supported local Windows and Mac data. Backblaze B2 is object storage accessed through a web console, APIs, command-line tools, and integrations. NAS and server designs generally use B2 with compatible backup software rather than the endpoint client.
Can Backblaze Computer Backup protect a NAS or network drive?
No. Backblaze lists network-mounted drives, NAS devices, remotely mounted computers or volumes, and shared volumes as excluded from Computer Backup. Use a supported Backblaze B2 integration for those workloads, then design bucket access, credentials, monitoring, retention, cost controls, and restore testing separately.
What is the difference between a managed and unmanaged Backblaze group?
A managed group allows administrators to manage member accounts, including browsing backed-up data and creating restores. An unmanaged group’s administrators handle payment without that content access. Treat managed authority as a material privacy and least-privilege decision, and secure approval before creating the group.
Can a Backblaze group's administrative level be changed later?
The managed-versus-unmanaged privilege choice in the group-creation procedure cannot be changed afterward. That is different from the documented managed-group upgrade to Enterprise Control, which first requires Backblaze to grant access. Approve the original privacy choice and check the actual entitlement before assuming an administrator can switch between these models.
What is the difference between centralized and decentralized Backblaze deployment?
Centralized deployment puts multiple endpoints under an IT-managed Backblaze account; their users rely on that account’s recovery authority. Decentralized deployment uses the relevant user’s Backblaze sign-in. In either model, verify the actual endpoint-to-account mapping, group and region in the pilot. Installing the right software or accepting an SSO login does not prove that ownership is correct.
How should Backblaze Group Tokens be handled during silent deployment?
Treat the Group ID and Group Token as protected enrollment values, not ordinary inventory labels. Keep them in secured deployment tooling with restricted access, and exclude their values from logs, screenshots and tickets. After suspected exposure, ask Backblaze for the supported containment and replacement procedure, then reconcile unexpected enrollments. Do not invent a token-rotation command or assume changing a local script revokes the old credential.
What must be configured before silently deploying Backblaze on Mac?
Prepare the supported macOS privacy and background-service settings for the actual OS and deployment method, including Full Disk Access and applicable Managed Login Items. In the current centralized Jamf v10 workflow, inspect bootstrap configuration and inventory-based status as well as installer delivery. Hold acceptance until a required local sample is backed up and restored; a policy or installer success alone is insufficient.
How long should a Backblaze initial backup take?
Backblaze’s general guidance says an initial backup should be able to finish within 30 days and recommends support review if the estimate is longer. That is not a recovery guarantee or a reason to ignore a stalled pilot for a month. Check power, sleep, connectivity, eligible files and progress early, and escalate missing or blocked business data when observed.
What evidence proves a Backblaze rollout is complete?
Reconcile the expected endpoint list with actual accounts, groups and computer records, then document eligible selections, current client status and a successful approved sample restore. Keep missing devices and disconnected required drives in the denominator with named exception owners. A NAS protected through B2 needs separate job and recovery evidence; it is not another successful Computer Backup endpoint.
Sources
- Backblaze create a Business Group ↩
- Backblaze Business Groups overview ↩
- Backblaze silent installation overview ↩
- Backblaze silent installation for Windows ↩
- Backblaze silent installation for Mac ↩
- Backblaze centralized Jamf Pro deployment ↩
- Backblaze Computer Backup best practices ↩
- Backblaze supported backup data ↩
- Backblaze B2 integration boundary ↩
- Backblaze: administer a Business Group and inspect alerts ↩
- Backblaze: external drives and Version History ↩
- Backblaze: Enterprise Control entitlement and managed-group upgrade ↩