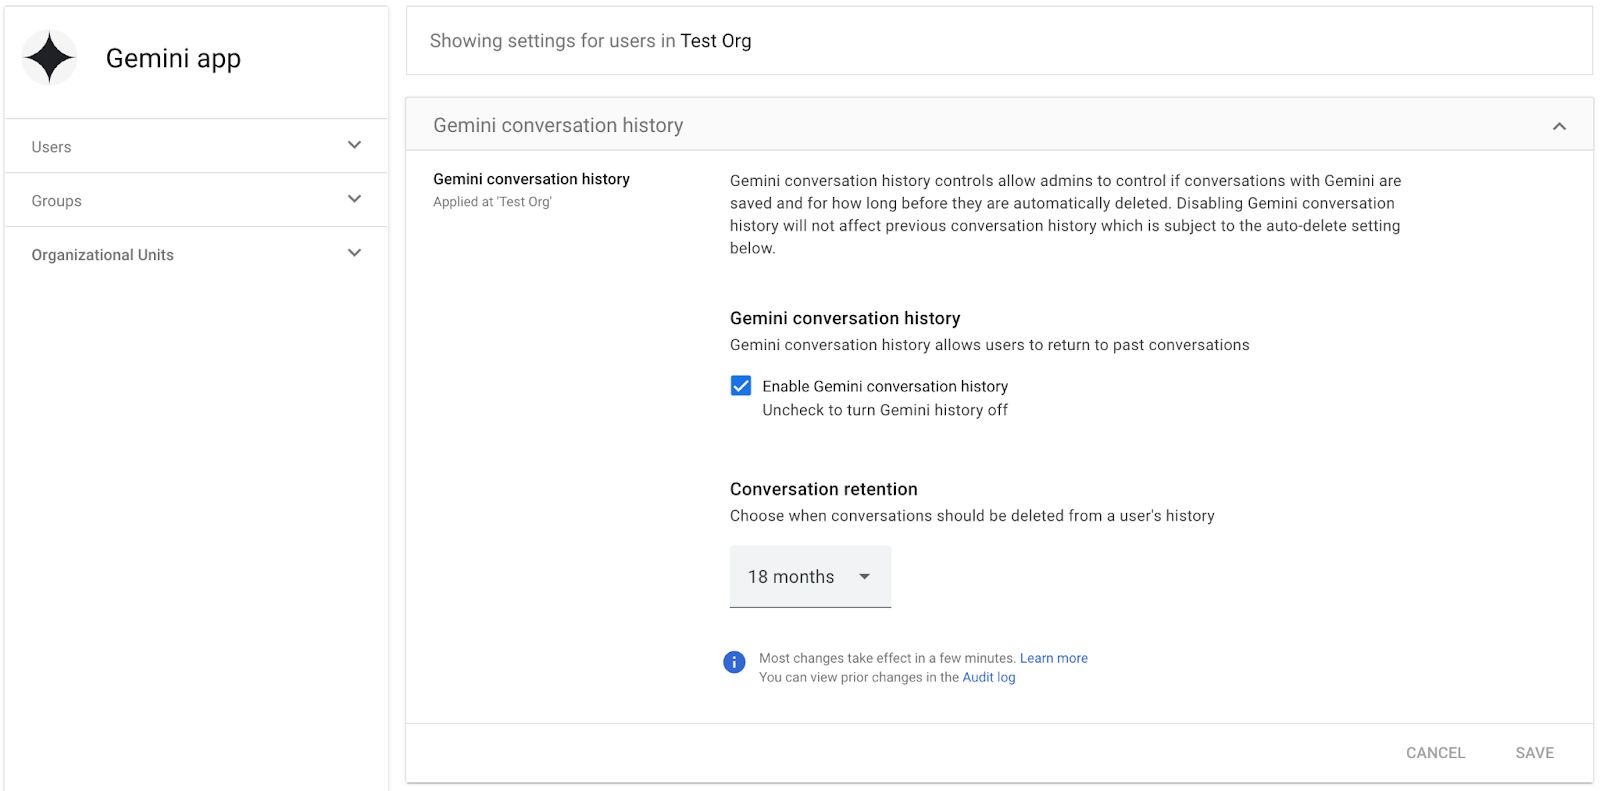
Google’s education administrator guide shows the Gemini app conversation-history panel for Test Org, with history enabled and 18 months displayed. This is a vendor example, not our tenant, a recommended retention period, or evidence that a change was saved. Confirm the current account, surface, applied scope and retention/deletion requirements separately.[11] View full-size image
A Gemini governance review should determine which services are enabled, what managed and personal identities users rely on, which Workspace data Gemini can reach, how conversations are retained or shared, and whether high-impact output receives meaningful human review. License assignment alone does not answer those questions.
Do not disable a service, remove a license, block a Workspace connection, or delete an integration until active workflows and required records are understood. Capture the applied organizational unit and group settings, identify affected users, and test a controlled replacement process.
ALLMSP provides Google Gemini access, ownership, and security review for Lawrenceville and Suwanee businesses, the wider Gwinnett County and Metro Atlanta area, and organizations across Georgia, with practical coordination across managed IT, cybersecurity, software support, backup, and employee operations.
Evidence to collect before changing Gemini governance
A useful review package connects user populations, licenses, service status, Workspace data controls, conversation settings, sharing, third-party apps, policy training, usage evidence, support incidents, and exceptions. It distinguishes a setting gap from a user behavior gap and a process design gap.
- Gemini app and Workspace AI service status by organizational unit and configuration group.
- Licenses, eligible users, inactive users, pilot users, mobile access, and personal-account workarounds.
- Google apps in Gemini, underlying Workspace sharing, OAuth access, and third-party AI integrations.
- Conversation history, retention, sharing, and records required by the business.
- Role-based policy, training, approved use cases, output review, and exception approvals.
- Usage reports, audit evidence, support tickets, incidents, and measurable business outcomes.
Worked example: distinguish three Gemini control questions
The following invented review cases separate access, history, and data handling. They are decision prompts, not recommended settings for every organization or evidence that a particular tenant has been secured.
| Question | Evidence to collect | Decision boundary |
|---|---|---|
| The Gemini app is off, but a user still sees Gemini inside a Workspace app. | Exact app/surface, edition, applied user scope, and relevant Workspace AI control | The Gemini app switch does not disable all Workspace AI features. |
| A user cannot reopen an old app conversation. | App history state, retention policy, account type, and any Workspace side-panel history | Loss of user visibility is not proof of immediate deletion from every store. |
| A worker submits a company document through a personal account. | The actual identity/service, data involved, approved purpose, and incident owner | Resolve the managed workflow gap and evaluate the exposure under the applicable terms; do not assume equivalent protections. |
Supporting documentation: [1] [4] [8] [6]
Image documentation: [11]
Map Gemini services, users, and applied settings
Service status and eligibility
What to check: Record service status by organizational unit and group, user eligibility, assigned licenses, age or edition restrictions, mobile behavior, and whether unlicensed users receive access under current settings.
What to do next: Align service access with approved populations and preserve required workflows. Review the actual Workspace subscription and any separately purchased eligible add-on before proposing a license change.
Treat the Gemini app, Gemini features in Workspace services, and any purchased add-on as separate entries. Many Workspace subscriptions include Gemini features. The Gemini app on/off switch has no effect on the other AI features in Workspace services, so record and test the control that actually governs the workflow.
Supporting documentation: [1] [4]
Organizational unit and group overrides
What to check: Identify the setting inherited by each user population, groups that override organizational units, pilot exceptions, and accounts placed in the wrong container. Capture propagation and review dates.
What to do next: Correct placement and simplify overlapping exceptions. Retest users whose access depends on a group override before removing the old rule.
Workspace data connections
What to check: Document whether Gemini may use Workspace data, which services are connected, what underlying content users can access, and examples where broad file sharing expands reachable information.
What to do next: Correct the underlying Workspace sharing and the Gemini connection policy together. Do not rely on prompt instructions to compensate for excessive Drive or Gmail access.
Do not assume every delegated workflow is available to Gemini: Google's current Workspace user guidance says Gemini does not access a delegated Gmail inbox. It also identifies file access, owner download/copy/print controls, and administrator settings as relevant boundaries. Check the specific surface and task rather than extrapolating from a person's ordinary browser access.
Supporting documentation: [2]
Review Workspace data reach and conversation behavior
Conversation history and retention
What to check: Capture whether history is enabled, the selected retention, applied user scope, legal or operational ownership, and user understanding. Review whether procedures assume records that the setting does not retain.
What to do next: Align retention and documentation with approved requirements, communicate the behavior, and remove unsupported assumptions from business processes.
Keep Gemini app activity separate from Workspace side-panel conversation history. A retention selection, a user's ability to reopen a conversation, and service-held copies are different questions. Document the applicable account/surface and current deletion controls without claiming that turning history off instantly erases everything.
Supporting documentation: [1] [6]
Conversation sharing
What to check: Record whether managed users may share conversations, outside recipients involved, sensitive content examples, business purpose, and personal-account bypasses. Confirm links still work as policy expects.
What to do next: Restrict unsafe sharing, remove exposed content where possible, correct the source data permission, and train affected users with realistic examples.
Google's current chat-sharing guide notes that a Workspace administrator can turn conversation sharing on or off. Where public links are supported and allowed, anyone holding the link can read and reshare the saved conversation. Treat exported documents, copied text, and shared Gems as separate sharing routes with their own controls.
Supporting documentation: [7]
Third-party and OAuth applications
What to check: List applications that request Gmail, Drive, Calendar, or other Workspace scopes and also provide AI features. Record verification, scopes, users, owner, data destination, contract, and current need.
What to do next: Block or limit obsolete and risky apps, assign an owner to approved access, and test business workflows before revocation.
Personal AI accounts and shadow use
What to check: Identify work performed in personal Gemini or other AI accounts, the reason managed tools were bypassed, data involved, output destination, and whether the employee understood the difference.
What to do next: Address the workflow or access problem that caused bypass, protect exposed data, and provide an approved path rather than relying only on a prohibition.
Inspect policy, third-party access, and operating evidence
Human review for high-impact output
What to check: Select customer, finance, HR, legal, security, and executive examples. Record source quality, reviewer qualification, corrections, approval, and whether final output can be traced to a responsible person.
What to do next: Add explicit review gates, qualified approvers, source requirements, and evidence retention where errors can materially affect people or the business.
Training and policy understanding
What to check: Compare training completion with the ability to classify data, choose approved tools, verify output, cite sources, escalate uncertainty, and report incidents. Identify departments using only generic awareness training.
What to do next: Deliver role-based exercises using actual workflows and require remediation for users with high-risk access or repeated unsafe behavior.
Usage, incidents, and business outcomes
What to check: Record active use, inactive licenses, feature patterns, risky sharing, data concerns, inaccurate output, time saved, rework, user adoption, and process outcomes. Separate reported enthusiasm from validated results.
What to do next: Close control gaps, support useful workflows, remove unsupported licenses, and keep only metrics that can be reproduced and tied to business work.
Rank findings by data and decision impact
Treat exposed restricted data, unmanaged personal use, unsafe external sharing, and high-impact output without qualified review as urgent. Treat broad file access, one-off group exceptions, unknown third-party apps, and missing incident procedures as control risks. Low adoption and inactive licenses can be corrected after material data and decision risks are contained.
Priority 1: Data exposure or unsafe decision use
Use this level for restricted information submitted or shared improperly, unapproved personal AI use involving business data, high-impact output accepted without review, or an active third-party connection with unjustified sensitive scopes.
Priority 2: Control and recovery weakness
Use this level for broad Workspace access, conflicting group settings, unclear conversation retention, unowned exceptions, weak incident response, and policy that users cannot apply to real work.
Priority 3: Adoption and license hygiene
Use this level for entitlement/access mismatches, unclear feature awareness, inconsistent prompt libraries, low-value experiments, and training improvements after data and decision risks are controlled.
Next task: review Drive ownership and offboarding dependencies; evaluate Gemini work quality and support gaps.
Continue reading
Frequently Asked Questions
What should be checked in a Gemini service access review?
Separate the Gemini app from Gemini features inside Workspace services. Record the signed-in account, qualifying Workspace edition, service status, and applied organizational unit or group for each intended workflow. Turning off the Gemini app does not turn off all Workspace AI features. Confirm the resulting behavior with a representative managed user rather than relying only on an administrator's view.
How can configuration groups change Gemini access?
For supported Gemini settings, a configuration group's setting can override the user's organizational-unit setting. Review group membership, applicable priority, inherited state, and the particular control being tested; one group's name is not proof that every Gemini feature follows it. Use a pilot account in the intended combination of groups and verify its effective service behavior.
FAQ supporting documentation: [1]
Why should Drive and Gmail permissions be reviewed with Gemini access?
Those permissions define important boundaries around the Workspace content the user can reach. Inspect a sensitive file, external share, group membership, and delegated workflow instead of assuming Gemini creates a new universal permission boundary. Connected-app availability also depends on edition and administrator settings. Correct excessive underlying access and test the approved workflow using the affected user's account.
What evidence is needed for a Gemini conversation retention review?
Record the exact Gemini surface and account type, the effective history setting, retention choice, and applicable deletion controls. Gemini app activity and Workspace side-panel conversation history are different stores. Turning app history off can prevent reopening chats without implying immediate erasure of all service-held data. Verify current admin documentation and a sanitized example before making a retention or deletion assurance.
How should shared Gemini conversations be audited?
Identify what was shared: a Gemini chat link, a shared Gem, an exported document, or copied text. Public chat links, where supported, can be opened and reshared by anyone holding the link; availability differs by account and surface. Audit the actual destination's access with sanitized content, remove an inappropriate supported share, and address copies already distributed rather than assuming one switch retracts them all.
Which third-party applications belong in a Gemini governance review?
Include OAuth applications, browser extensions, AI add-ons, connectors, and any other integration that receives company data or acts through a managed identity. Record the vendor, requested scopes, approved purpose, account, and revocation owner. A Google sign-in button is not evidence that an application has only basic profile access or is approved to receive confidential material.
FAQ supporting documentation: [9]
How should personal Gemini account use for business work be handled?
Treat it as an account and data-handling gap, then provide a usable approved route. Confirm which identity was used and what information may have left the managed environment; do not assume personal Gemini has the same terms and protections as an eligible Workspace core service. Resolve blocked workflows and training needs while escalating any sensitive-data incident through the organization's process.
Which Gemini outputs require formal human approval?
Require an accountable human to approve outputs that affect money, contracts, employment, security, regulated decisions, or external commitments according to the business's risk policy. Check the original evidence, calculations, and authority to act. This is a proposed review control, not a claim that Gemini can certify professional or legal correctness.
FAQ supporting documentation: [10]
How can a review tell whether Gemini training is effective?
Give users a representative approved task and check whether they can choose permitted inputs, verify important claims, recognize an unsafe request, and escalate uncertainty. Repeat with a different example after training and record errors and review effort. Usage counts can locate coaching needs, but neither high activity nor a confident self-rating demonstrates safe competence.
What should Gemini governance reporting include?
Report effective access and unresolved data exposure separately from adoption and quality. Name an owner and next action for each finding, with a sanitized test or source record showing the evidence. Include exceptions and review dates; do not present prompt counts as productivity gains or a clean sample as assurance about every user's conversations.
FAQ supporting documentation: [3]
Sources
- Control access to the Gemini app in Google Workspace. Official administrator guidance for service status, organizational scope, licensing, and conversation-history controls, with the planning steps on this page applying it to the work needed to audit Gemini data access, sharing, and conversation controls. ↩
- Controls for Gemini access to Workspace data. Official explanation of administrator, content-owner, sharing, download, and delegated-mail controls that affect Gemini data access, with the configuration checks here applied to the controls needed to audit Gemini data access, sharing, and conversation controls. ↩
- Review Gemini usage in an organization. Official guidance for organization and user adoption reports, app-level usage, last use, and audit-log analysis, with the review process on this page using that guidance to help the organization audit Gemini data access, sharing, and conversation controls. ↩
- Gemini AI features now included in Google Workspace subscriptions. ↩ ↩ ↩
- Use apps connected to Gemini with a work or school Google Account. ↩
- Using Google Workspace with Gemini. ↩ ↩ ↩
- Share your chats from Gemini Apps. ↩ ↩
- Use Gemini Apps with a work or school Google Account. ↩ ↩ ↩
- Control which third-party & internal apps access Google Workspace data. ↩
- View related sources from Gemini Apps. ↩ ↩
- Google for Education: Gemini and NotebookLM administrator enablement guide. ↩