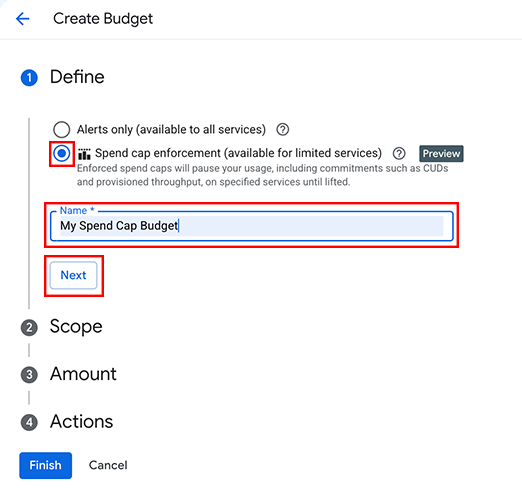
Google’s budget-creation example separates Alerts only from Spend cap enforcement. Check the eligible service, project scope and current availability before choosing a cap, then plan for the usage pause it can cause; it does not cap every charge.[5]
Google Cloud access is inherited through an organization, folders, projects, and individual resources. Billing access is related but separate. A user can control a billing account without administering workloads, or administer a project without seeing invoices. A dependable setup maps both authority paths and connects each project to a named business owner, technical owner, security owner, and cost owner.
Do not remove an Owner, billing administrator, service account, key, organization policy exception, or project link until effective permissions and workload dependencies are understood. Capture IAM policies at the organization, folder, project, resource, service account, and billing account levels. Test replacement access with a separate authorized identity before making a destructive change.
Businesses can use ALLMSP for Google Cloud deployment and configuration for organizations in Lawrenceville and Suwanee, throughout Gwinnett County and Metro Atlanta, and across Georgia, with local assistance available when device, network, office, or employee work needs an on-site component.
What a dependable Cloud IAM and billing setup should accomplish
A dependable setup gives people and workloads only the access they need, keeps production resources under company-controlled identities, separates billing tasks from resource administration, and produces enough logs and budget signals to investigate both security and cost changes. Emergency access and ownership recovery are tested rather than assumed.
- The Cloud organization, folders, projects, billing accounts, and important standalone resources are inventoried.
- Google Groups and role assignments follow business and technical responsibility instead of individual convenience.
- Basic Owner and Editor roles are avoided where predefined or custom roles can express the work more safely.
- Service accounts are single-purpose, keyless where possible, named clearly, and reviewed as both resources and identities.
- Billing roles, project links, labels, and exports support accountability. Ordinary alerts-only budgets notify owners; separately configured spend-cap budgets can pause covered usage only within their supported scope. [5]
- Audit logs, recovery identities, escalation contacts, and a tested change process are documented.
Build the Cloud resource and ownership model
1. Inventory the organization and billing boundary
Record the organization ID, folder hierarchy, project IDs, project numbers, lifecycle state, billing account IDs, linked payment profile, billing contacts, and projects outside the expected organization. Assign business, technical, security, and cost owners to each production project.
Where to work: Google Cloud console > IAM & Admin > Manage resources and Billing > Manage billing accounts
Verification: A reviewer can connect every active project to the correct organization, billing account, workload, environment, and accountable owner.
2. Design folders around policy and ownership
Use folders where a stable business, environment, compliance, or administrative boundary needs shared policy. Avoid deep hierarchy that makes inheritance difficult to explain. Separate production from development when access, logging, networking, or change control differs materially.
Where to work: Cloud resource hierarchy under the organization node
Verification: For a sample project, administrators can explain which IAM and organization policies are inherited from every parent and why the project belongs there.
3. Assign access through controlled groups
Create groups for durable responsibilities such as billing viewers, project administrators, security reviewers, developers, and incident responders. Grant the group a role at the narrowest practical resource level. Use individual assignments only for documented exceptions or emergency access.
Where to work: Cloud IAM policies and the company identity directory
Verification: Adding and removing a test member changes access as expected without editing several projects manually.
Configure user and workload access
1. Choose predefined roles before basic roles
Translate job tasks into required permissions, then choose predefined roles that cover those tasks. Avoid Owner and Editor for routine work. Use a custom role only when stable requirements cannot be met by predefined roles and someone owns its lifecycle.
Where to work: IAM & Admin > IAM and role documentation for each service
Verification: A representative user completes required actions and receives a clear denial for a higher-risk action outside the role.
2. Separate resource administration from billing
Assign Billing Account User, Billing Account Viewer, Billing Account Costs Manager, Billing Account Administrator, and project roles according to actual responsibility. Do not give broad project control merely so a person can view cost, or broad billing control merely so a developer can link an approved project.
Where to work: Billing account > Account management > Permissions and project IAM
Verification: Finance can view and manage the approved billing tasks without changing workloads, while technical staff can manage resources without changing payment ownership.
3. Create single-purpose service accounts
Create a dedicated service account for each workload or automation with a clear name, owner, purpose, environment, and retirement condition. Attach it to the workload and grant only resource roles it needs. Avoid shared default service accounts and broad Editor access.
Where to work: IAM & Admin > Service Accounts within the owning project
Verification: Logs and documentation can identify which application used the service account and which resources it is allowed to reach.
4. Avoid long-lived service account keys
Prefer attached service accounts, impersonation, or Workload Identity Federation instead of downloaded keys. When a key is unavoidable, document the system, owner, storage, rotation, monitoring, and expiration. Consider policies that disable key creation by default.
Where to work: Service account > Keys, workload authentication design, and organization policy
Verification: A workload authenticates successfully without a downloaded key, or the approved key appears in the inventory with a tested rotation procedure.
Connect billing, budgets, and audit evidence
1. Connect projects to billing with cost metadata
Link only approved projects to the correct billing account. Apply consistent environment, owner, department, client, application, and cost-center metadata where supported. Define who may create projects and who confirms their billing and lifecycle information.
Where to work: Billing account project links, project labels or tags, and cost allocation design
Verification: A cost report can group current spend by the categories management needs and every unclassified project has an owner and correction ticket.
2. Create budgets, alerts, and billing export
Create alerts-only budgets at useful scopes with thresholds that reach accountable people and operational systems. Separately evaluate spend-cap budgets for eligible services in a single project: enforcement is delayed, can interrupt the application, and does not cap every charge. Keep alerts and an approved cost export for broader cost visibility. [5]
Where to work: Billing > Budgets and alerts and Billing export settings
Verification: A controlled low threshold or test process proves the alert reaches the expected channel and the cost export produces current records.
3. Enable logs and emergency recovery
Confirm Admin Activity and System Event logs, decide where Data Access logs are required, protect log destinations, and document retention. Maintain tightly controlled emergency identities with strong authentication and a monitored use procedure.
Where to work: Cloud Audit Logs, Logging sinks, IAM policy, organization contacts, and company recovery documentation
Verification: A test IAM change appears in the expected logs and an authorized person can follow the recovery procedure without using a departing employee’s account.
Test effective access, recovery, and cost signals
Test both allowed and denied behavior. Seeing a role in the console does not prove effective access because inherited policies, deny policies, conditions, service account impersonation, and resource-level bindings can change the result. Save the principal, resource, action, time, expected result, actual result, and related log entry for each test.
- User least privilege: Use a representative user to perform required work and one prohibited administrative action. Pass: Required work succeeds while the unrelated high-risk action is denied and logged.
- Inherited policy: Inspect a project under each major folder and compare effective access with parent policies. Pass: Administrators can explain every inherited role and condition that affects the project.
- Service account authentication: Run the workload using the approved attached identity, impersonation, or federation method. Pass: The workload reaches only its intended resources and logs identify the service account.
- Billing separation: Test finance and technical personas against billing reports, billing settings, and project resources. Pass: Each persona performs assigned work without gaining the other’s authority.
- Budget signal: Use an approved threshold test or alert verification process. Pass: The correct recipients and operational channel receive an identifiable budget notification.
- Emergency recovery: Follow the documented recovery process with authorized staff and a controlled access check. Pass: The business can regain necessary administration and the test produces monitoring evidence.
Separate cost visibility, billing links and workload control
These examples describe permission boundaries. Confirm the required scope and exact roles for the task; they are not a recommendation to grant broad administrator access. [4] [5]
On a narrow screen, scroll the table horizontally to read every column.
| Person or control | Intended job | Keep separate |
|---|---|---|
| Finance reviewer | View the approved billing costs | Changing production resources or payment administration. |
| Project operator | Run the workload and request an approved billing link | Administration of the entire billing account. |
| Alerts-only budget | Notify an accountable cost owner | Any assumption that usage automatically stops. |
| Supported spend-cap budget | Pause covered new usage for one eligible service/project | A guarantee of zero overage or a cap on the entire bill. |
Choose the next step
- Audit Google Cloud Roles, Service Accounts, and Billing Access — Audit existing inherited access, service accounts and billing permissions against the design.
- Reduce Google Cloud IAM Risk and Uncontrolled Billing — Prioritize risky identities and unexplained costs after the inventory is complete.
Frequently Asked Questions
What should be inventoried before Google Cloud IAM is configured?
Map the organization, folders, projects and billing accounts before changing roles. For each project, record its immutable ID and number, environment, workload, billing link and business, technical and cost owners. Include projects outside the expected organization and workload identities as well as human users. Otherwise an apparently unused project or inherited role may turn out to run production or pay for a critical integration.
How should Google Cloud folders be designed?
Create folders where a stable policy or management boundary needs to be inherited, such as separate production and development administration. Avoid mirroring every temporary team change in a deep tree. Sketch where a developer, security reviewer and emergency administrator get access, then examine a sample project's inherited policy. Moving a project between folders can change effective permissions and organization policies, so it deserves a change review.
Supporting sources: [1]
Why should Google Cloud access be assigned through groups?
Groups let the company change team membership without editing the same role on every resource. For example, grant a controlled finance-viewers group the needed cost-view role instead of granting it separately to each accountant. Group ownership, membership and nested groups become part of the security boundary, so review them too. Use separate, documented emergency access rather than making a broad everyday group an administrator everywhere.
When should a custom Google Cloud IAM role be created?
Create a custom role only when a defined, stable task cannot be served adequately by supported predefined roles. List the required permissions and supported resource scope, test the real task, then assign someone to maintain the role as services change. A custom role with a copied bundle of Owner-like permissions is not automatically safer. Routine work should not receive broad Owner or Editor access simply because choosing permissions takes longer.
Supporting sources: [1]
How are Google Cloud billing roles different from project IAM roles?
Project roles control resources; billing-account roles control billing functions. A finance viewer does not need workload administration, and a developer should not receive billing-account administration just to link an approved project. Linking requires permission on both sides, commonly Project Billing Manager on the project and Billing Account User on the billing account. Payments-profile permissions are another boundary, so check them separately before promising someone can change payment details.
Supporting sources: [4]
Why should Google Cloud service accounts be single-purpose?
A dedicated service account ties an application's permissions and audit trail to a known workload. If one shared identity runs backups, deployments and reporting, granting or revoking access for one task affects the others and investigation becomes harder. Name the account for its purpose and environment, record its owner, and give it only the resources it needs. Also restrict who may impersonate or attach it; that can grant the same workload access.
Supporting sources: [2]
What should be used instead of Google Cloud service account keys?
Use an attached service account for supported Google Cloud workloads, short-lived impersonation for authorized operators, or Workload Identity Federation for suitable external workloads. Choose the method the platform supports instead of downloading a JSON key by default. Where a legacy application genuinely requires a key, record the exception, protect and rotate it, and plan migration. Removing the key before replacement authentication works can stop the workload.
Supporting sources: [2]
How should Google Cloud projects be labeled for cost ownership?
Use a small controlled vocabulary, for example environment=prod, application=client-portal and cost_center=operations. Store a durable owner or team identifier rather than personal information, and name who keeps it current. Check the labels actually available in the relevant cost reports or export; project labels, resource labels and IAM tags are different mechanisms and are not interchangeable. Labeling supports allocation and review, not access control by itself.
Supporting sources: [4]
Do Google Cloud budgets automatically stop spending?
Alerts-only budgets do not stop usage. Google also offers separately configured spend-cap budgets for a single eligible service in a single project, with restrictions and enforcement delay. These can pause covered new usage, but they are not a universal bill ceiling: overages and ongoing persistent-resource costs can still accrue. Check current service eligibility and the availability of the control before relying on it, and plan for the application interruption a cap can cause.
Supporting sources: [5]
What logging and recovery should be configured for Google Cloud IAM?
Keep Admin Activity and System Event evidence accessible to the right responders, and explicitly decide where Data Access logs are needed because their defaults and costs differ. Protect log storage and exports from the same users whose changes they record. Document emergency identities and recovery contacts, then rehearse a controlled access failure. A role screenshot is insufficient: investigators need the principal, resource, action, time and relevant policy or log entry.
Sources
- Google Cloud IAM overview. Official explanation of principals, roles, resources, policies, inheritance, and fine-grained authorization in Google Cloud, with the planning steps on this page applying it to the work needed to set up Google Cloud IAM, projects, and billing ownership. ↩
- Google Cloud service-account security practices. Official guidance for limiting service-account privilege, avoiding unnecessary keys, tracking ownership, and reducing impersonation risk, with the configuration checks here applied to the controls needed to set up Google Cloud IAM, projects, and billing ownership. ↩
- Google Cloud Billing access control. Official guidance for billing-account roles, project cost access, payment-profile permissions, budgets, and administrative control, with the review process on this page using that guidance to help the organization set up Google Cloud IAM, projects, and billing ownership. ↩
- Overview of Cloud Billing access control. Separate billing-account and project permissions, project linking, cost visibility and payments permissions. ↩
- Manage spend cap budgets. Separate alerts-only and spend-cap budgets; single project/service limits, eligible services, latency and ongoing charges. ↩
- Cloud Audit Logs overview. Admin Activity/System Event versus configurable Data Access logs and protected audit evidence. ↩