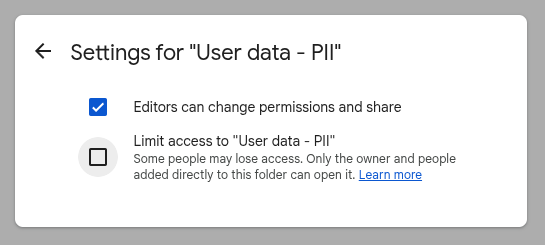
Google’s folder-settings example exposes two separate questions: whether editors may change sharing and whether access to the folder is limited. The pictured Limit access checkbox is unchecked; the example is not a secured client folder or a recommended saved configuration. Apply the documented My Drive or shared-drive rules and test the intended and excluded users.[8] View full-size image
A Drive ownership review should reveal where business-critical files live, who can remove or expose them, and which accounts the company cannot recover. The review must cover both My Drive ownership and Shared drive membership because transferring one employee’s files does not automatically correct direct shares, group membership, external access, scripts, or content stored in another organization’s drive.
Do not remove an owner, Manager, external collaborator, group, shortcut, or verification account until the business owner confirms the purpose and replacement access has been tested. A permission that looks unnecessary may support a client portal, form, published report, or automated workflow.
Our in-house team delivers Google Drive access, ownership, and security review for businesses around Lawrenceville, Suwanee, Gwinnett County, Metro Atlanta, and the rest of Georgia, while coordinating the applications, identities, devices, data, security controls, and employees affected by the work.
Evidence to collect before changing Drive ownership
A useful Drive review produces an asset and access record, not a folder cleanup impression. It identifies critical individual owners, Shared drive managers, externally shared content, public links, inactive users, unusual download or movement events, unresolved business ownership, and a tested remediation sequence.
- Critical folders and files still owned by individual users or outside accounts.
- Shared drive managers, members, groups, restrictions, and items with limited access.
- Files and folders shared externally, publicly, by link, or through groups with outside members.
- Inactive, suspended, former, service, agency, and personal accounts with access.
- Drive log events for sharing, downloads, deletion, ownership changes, and movement across organizations.
- Forms, scripts, Sites, reports, shortcuts, and integrations that depend on reviewed files.
Worked example: move the work, not just the files
This is a fictional offboarding checklist for a shared reporting process. Test a harmless copy or labeled submission first; a successful file move alone is not the acceptance criterion.
| Dependency | Evidence required | Acceptance check |
|---|---|---|
| A response sheet in an employee's My Drive | Actual owner, intended destination, direct shares, and report links | The authorized replacement can open the correct item and intended collaborators retain only approved access. |
| An Apps Script installable trigger | Creator/executing identity, required authorizations, and supported replacement | A labeled test submission reaches its expected output under the intended identity. |
| A confidential limited-access folder | Managers, directly permitted users, and relevant parent folders | An intended reader can open it; an ordinary excluded member cannot open its contents; manager access is understood. |
| An agency-owned source file | External ownership and permission for a supported copy/migration | The replacement's IDs, links, history needs, and downstream refresh are checked before the old dependency is retired. |
Find ownership and administrator concentration
Critical My Drive ownership
What to check: List important contracts, client folders, reports, Forms, scripts, templates, and operating records owned by individuals. Record the owner status, manager, collaborators, sensitivity, and whether the item belongs in a Shared drive.
What to do next: Move or transfer durable content through a controlled test. Keep personal drafts in My Drive only when a documented business rule supports that choice.
Shared drive Manager access
What to check: Record every Manager, whether access is direct or through a group, the person's current role, last review, and whether at least two authorized internal managers exist for a critical drive.
What to do next: Remove stale managers after a replacement has been tested. Use groups for durable team membership and keep management authority narrower than editing authority.
Member role accuracy
What to check: Compare Manager, Content manager, Contributor, Commenter, and Viewer assignments with current duties. Identify direct access that duplicates a group or gives deletion and movement rights unnecessarily.
What to do next: Downgrade excessive roles, consolidate membership through approved groups, and retest required work before removing direct access.
Inspect Shared drive and external access
External and public sharing
What to check: Filter for externally shared content and record the item owner, outside domain, access level, last activity, business reason, link setting, and expiration where supported. Include Groups that allow external members.
What to do next: Remove access that has no current owner, narrow access to the required file or folder, set expiration where appropriate, and confirm the client or vendor still completes the intended task.
Inactive and former user access
What to check: List suspended, archived, inactive, departed, renamed, and service accounts that own content or retain access. Record whether My Drive data was transferred and whether Shared drive memberships were removed separately.
What to do next: Complete data transfer and access removal through the offboarding process. Validate manager access and automation before deleting accounts or revoking credentials.
Content owned outside the organization
What to check: Identify critical items owned by personal Gmail accounts, agencies, clients, former employees, or another Workspace domain. Record what the business can export, copy, transfer, or recreate and which workflows depend on the external owner.
What to do next: Create a company-controlled copy or migration plan with permission from the business owner. Test links and automation before retiring the externally owned original.
External ownership is a migration constraint, not just a missing membership entry. Google does not let you directly move externally owned files or folders into your shared drive. Agree on an authorized supported copy or migration and check IDs, links, history needs, and downstream automation.
Supporting documentation: [5] [4]
Limited-access folders and direct exceptions
What to check: Record folders with limited access, nonmember shares, direct user exceptions, and the reason inherited drive membership is not sufficient. Confirm Managers understand who can still access the parent drive.
What to do next: Keep exceptions only where the sensitivity and workflow justify them. Name owners, use clear folder boundaries, and retest after membership changes.
Managers of the shared drive retain access. For other users, an Access removed entry does not settle the question if a group grant or general-access setting still permits entry. Test the folder contents with the intended and excluded accounts; its visible name alone is not an exposure finding.
Supporting documentation: [8]
Trace risky activity and workflow dependencies
File movement across organizations
What to check: Review files moved into external Shared drives, copied out of the organization, downloaded in volume, or transferred between domains. Capture actor, item, source, destination, timestamp, and approved business reason.
What to do next: Escalate unexplained external movement, preserve logs, restrict access, and coordinate with security and business leadership before altering evidence or deleting accounts.
Workflow and published-content dependencies
What to check: List reviewed files that collect responses, run automation, feed dashboards, publish web content, or authenticate an integration. Record the owner and service account or user context for each dependency.
What to do next: Move ownership or redesign the workflow so it does not depend on a departing person. Test with a real submission or refresh before changing the original permission.
Recovery and backup evidence
What to check: Record available restore windows, who can restore content, covered users and Shared drives, recent failed jobs, legal holds, and the result of representative file restores.
What to do next: Close coverage gaps, assign restore authority, and schedule recurring tests that include My Drive, Shared drives, and business-critical linked content.
Rank findings by data exposure and continuity impact
Treat public exposure, unknown external ownership, unexplained file movement, and imminent offboarding as urgent. Treat single-person ownership, missing backup evidence, and fragile automation as continuity risks. Naming and organization issues matter after the business can prove it controls the data and can recover it.
Priority 1: Exposure or loss in progress
Use this level for public sensitive files, unknown external owners, suspicious downloads or moves, deleted records without recovery, or a departing account that uniquely controls critical work. Preserve evidence and assign an owner immediately.
Priority 2: Fragile ownership and recovery
Use this level for one-person Shared drive management, important My Drive ownership, untested backups, unsupported external dependencies, and scripts or Forms tied to a person who may leave.
Priority 3: Organization and policy debt
Use this level for inconsistent names, excessive duplicate folders, undocumented exceptions, stale shortcuts, and access that should be consolidated through groups. Correct it after exposure and continuity risks are controlled.
Next task: check Gemini data and conversation controls; build the cross-product account and recovery register.
Frequently Asked Questions
How can a business find critical files still owned in My Drive?
Search for critical records owned by named users and reconcile the results with department inventories, Forms, scripts, and reports. Record the file ID and actual owner, not just the folder or shortcut containing it. Prioritize records that would stop work if that person left, then test an authorized move or other supported continuity arrangement before changing ownership at scale.
How many Managers should a critical Shared drive have?
Two independently usable, company-controlled Managers are a sensible continuity target for a critical shared drive, not a Google requirement to grant everyone elevated access. Choose accountable people, protect their sign-ins, and confirm each can perform the recovery task. Other collaborators should receive only the role needed for their work.
FAQ supporting documentation: [2]
What should be checked when reviewing Shared drive member roles?
Check each direct member and group, its role, approved purpose, and the effective access of a representative user. Manager, Content manager, Contributor, Commenter, and Viewer have different capabilities; folder-sharing restrictions can further change what a role may do. Review directly shared files and folders too, because the drive's membership list does not describe every nonmember share.
FAQ supporting documentation: [2]
How can administrators find Google Drive files shared outside the company?
Review current file/folder permissions for external principals, groups, visitor sharing, and broad links, using the reporting or investigation tools available to the organization's edition. Logs show events, while current permissions establish who can open an item now. Validate sensitive examples with an authorized external test account and record the specific permission route before removing it.
Why is transferring Drive files not enough during offboarding?
A file transfer does not by itself remove group membership, shared-drive roles, delegated access, connected applications, or automation tied to the departing identity. Apps Script installable triggers run as the user who created them. Reassign the supported business dependencies and prove that a Form submission, scheduled process, and report refresh still work before retiring the old account.
What should be done when an agency owns a critical Google Drive file?
First agree on a supported handover with the agency and verify who owns the actual file. Files owned outside your organization cannot simply be moved into your shared drive. An authorized copy or migration may be necessary and can change IDs, links, history, or integrations. Test those effects on a representative record before replacing the production dependency.
How should limited-access folders in Shared drives be reviewed?
Test the folder itself with an intended user and an ordinary drive member who should be excluded. Limited access is a folder exception to the drive's normal inherited visibility; managers retain access, and a visible folder name does not mean its contents can be opened. Check the complete parent hierarchy and current product rules before treating a membership export as proof of confidentiality.
Which Drive log events can reveal files leaving the organization?
Look for relevant sharing, download, copy, move, and ownership-change events, then inspect the affected item's present permissions and destination. Event availability and fields depend on the action, account, edition, and logging context. A download event is an investigation lead, not proof of malicious exfiltration, and absence of an event is not proof that no outside copy exists.
FAQ supporting documentation: [6]
How can a Drive review avoid breaking Forms and automated reports?
Map each important Form, response sheet, script, trigger, connector, and report credential to its executing identity before moving files or disabling users. Run a harmless labeled submission and follow it through the expected output. Recreate or reauthorize the supported automation under its intended owner where necessary, and keep the old route available until the new one is verified.
What recovery evidence should a Google Drive access review include?
Keep evidence that a backup Manager can administer the correct drive, authorized collaborators can open representative files, and the agreed restore process can recover a safe test item. Record what the test covered and the applicable recovery window. Shared-drive persistence after an employee leaves is useful, but it is not proof of a separate backup or recovery from every deletion scenario.
Sources
- Set up shared drives for a Google Workspace organization. Official administrator guidance for organization-owned shared drives, membership, migration, and sharing controls, with the planning steps on this page applying it to the work needed to audit Google Drive ownership, external sharing, and stale access. ↩
- How access works in Google shared drives. Official explanation of shared-drive roles, member and nonmember access, limited-access folders, and external sharing, with the configuration checks here applied to the controls needed to audit Google Drive ownership, external sharing, and stale access. ↩
- Google Workspace shared-drive overview. Official guidance on team ownership, persistence after employee departure, membership, restrictions, and file organization, with the review process on this page using that guidance to help the organization audit Google Drive ownership, external sharing, and stale access. ↩
- Transfer Drive files to a new owner as an admin. ↩ ↩ ↩ ↩ ↩
- Move files & folders into shared drives. ↩ ↩ ↩ ↩
- Drive log events. ↩ ↩
- Installable Triggers. ↩ ↩ ↩
- Learn about limited access to files and folders in Google Drive. ↩ ↩ ↩
Source 2 cited here: ↩ ↩ ↩ ↩ ↩
Source 3 cited here: ↩