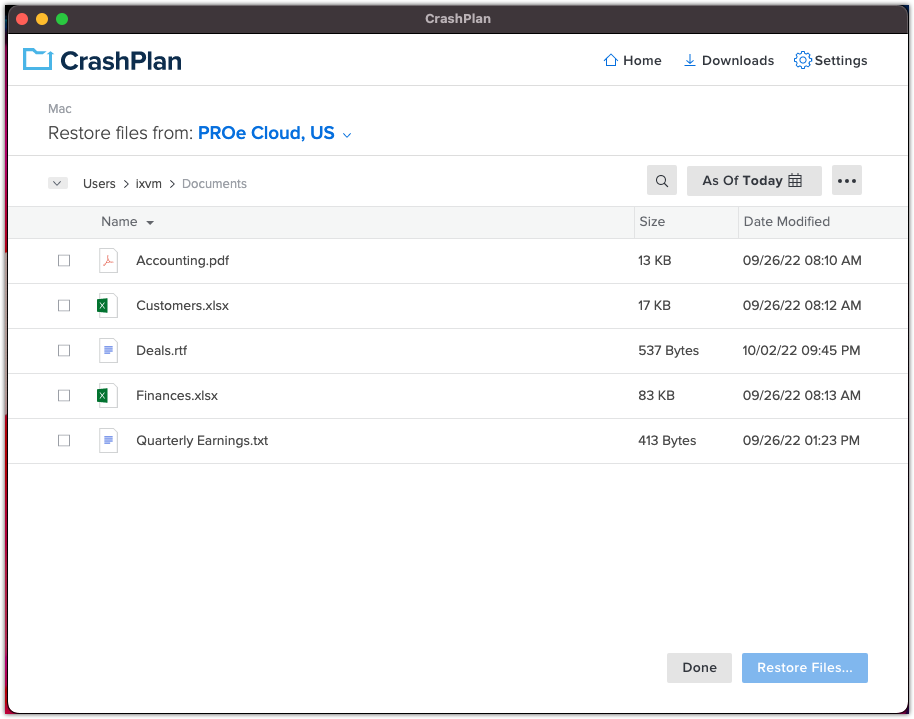
CrashPlan’s published Restore Files example shows archive browsing and the As Of date control. No files are selected and Restore Files is disabled. The historical sample dates illustrate the interface; they do not establish available retention or a completed restore in another environment.[8] View full-size image
When a user needs yesterday’s file, the useful test is whether an authorized operator can find the right version, restore it safely and open it with the required application and permissions. A 100 percent backup indicator does not prove those steps. Start with a known synthetic file in a clean target folder, then test the versions, file sizes and replacement scenarios that matter to the business.
This guide separates archive selection, target and conflict options, failed or slow restores, and device replacement. The worked drill counts authorization and validation time as well as transfer time. Its synthetic timings illustrate an acceptance decision; they are not a CrashPlan performance promise or a report of a client recovery.
This guide builds evidence from controlled sample restores and larger timed drills. It keeps customer filenames and archive details restricted, distinguishes CrashPlan app, console web, zip, and device push behavior where available, and treats backup status as an input rather than the final proof of recovery.
ALLMSP coordinates CrashPlan backup and recovery validation from Lawrenceville for clients in Suwanee, across Gwinnett County and Metro Atlanta, and throughout Georgia, through one accountable in-house workflow from discovery and correction through testing, training, and ongoing support.
Key decisions at a glance
- Define a CrashPlan restore matrix from business recovery needs, not a random download: include representative devices, destinations, file types, versions, deleted items, permissions, sizes, operating systems, and authorized roles.
- Use a controlled target path and the rename-existing option for the first test, original-location restore, cross-OS paths, ownership preservation, and overwrite behavior have constraints that can damage working data.
- Troubleshoot by state: destination connectivity, archive synchronization or maintenance, source selection, deleted-file visibility, target capacity, write permission, macOS Full Disk Access, queue size, network, and endpoint power all matter.
- CrashPlan reassembles, downloads, decompresses, and decrypts file blocks one file at a time, large interrupted files restart, so recovery timing must be measured with realistic data and stable power and connectivity.
- For device replacement, restore required files before linking the old archive, preserve username and drive-letter assumptions, and wait for verification and 100 percent completion before changing selections.
Build a Restore Matrix from Business Recovery Requirements
Start with a recovery catalog that maps each critical endpoint data set to its business owner, source device, CrashPlan user, organization, backup set, destination, inclusion path, exclusions, version and deleted-file retention, encryption-key policy, legal or privacy constraint, recovery-time objective, recovery-point objective, restore operator, approver, target location, application validation, and evidence owner. Store identities, filenames, GUIDs, archive sizes, target paths, organization details, and keys in restricted records. The public runbook should use synthetic examples. Confirm that endpoint backup is the appropriate protection method for each workload. Treat this as endpoint file recovery.
Open databases, virtual machines, server application state, cloud SaaS data, system images and boot recovery may require application-consistent exports or separate protection platforms. A downloaded raw file is not proof of a supported application or full-system recovery. Include the supported export or dump in the backup selection and test the application’s recovery procedure rather than validating only that a raw database file downloads. Create a matrix that samples Windows, macOS, and Linux where used, local and SSO identities, an ordinary user and an administrator-assisted restore, a current file, previous version, and deleted file, small documents and a large file, many small files, nested directories, external-drive data, long or unusual names, ACL-sensitive content, and a device-replacement scenario.
Include each configured destination and backup set because a file can exist in one archive view but not another. CrashPlan’s restore browser lets an operator choose the source device, destination, backup set, historical date, and available versions. Record those choices in the test case. Select the restore method according to authorization and size. The CrashPlan app can restore a user’s accessible archives. Console web or zip restore and device push restore require corresponding roles and organization settings. Push restore sends data through the target device’s CrashPlan app, requires that device to be online, and is not constrained by the organization’s web-restore size limit.
Do not infer availability from another tenant or plan, verify current product features, web-restore policy, encryption mode, and role permissions. Separate the tester from the approver for sensitive content. Use synthetic or owner-approved samples and minimize browsing of real filenames. A successful plan answers who may locate, decrypt, download, deliver, inspect, and delete restored data before the test begins.
The getting-started backup guide explains file-selection and destination basics; use the backup-policy considerations to decide whether the intended workload has the right protection design.[4][12] Archive browsing depends on the selected source, destination, backup set and date.[8] Push restore additionally requires the right permission and an online target.[5]
Choose Target, Conflict, Version, and Permission Options Safely
Use a clean controlled target folder for the first execution. In the CrashPlan app, Downloads is the default and Desktop or another selected folder can be used, Original location recreates the source path but is automatically disabled when the source and target operating systems differ. In a console device push restore, CrashPlan recommends an explicit Target Path, while Original Location is also available. Verify that the target device is online, that the path belongs to the approved test, and that enough free space exists. Do not use a production application folder as the first target merely to save a later copy step.
Pick conflict behavior deliberately. Rename existing and restore a copy is CrashPlan’s recommended choice when the operator is uncertain, it preserves the restored filename and renames the pre-existing file with an original-number prefix. Replace overwrites the current target and needs data-owner approval plus a rollback copy. App-only skip options can avoid restoring a duplicate or protect newer or older files by timestamp, but timestamps do not prove business correctness. Record the chosen behavior and create an intentional conflict in the test so the outcome is observed rather than assumed. Choose permissions based on the next operator.
Current, the recommended default, changes ownership to the user performing the restore and improves immediate access on a new device or profile. Original retains the backed-up ownership and permissions, which may be required for a controlled migration but can leave files inaccessible to the intended user on a different device or profile. Validate the result on the actual target filesystem instead of assuming that the permission option proves every cross-platform attribute was recreated. Confirm write permission before starting, and validate owner, group, ACL, extended attributes, executable state, and application access afterward where relevant. macOS recovery may require Full Disk Access for the CrashPlan app and permission to the target.
Select the correct time and version. Use the file’s version history to establish when it was backed up; a folder’s Date Modified value is not proof of its children’s backup time. Do not demonstrate only the newest file. Restore a known previous version and a deleted item within the configured retention window, verify the content against an expected hash or application check, and document the archive date. If an expected file is absent, confirm source device, destination, backup set, historical date, deleted-file visibility, file selection, exclusions, external drive connection at backup time, and whether a replacement operation marked the path deleted.
Validate the restore without opening untrusted active content on an ordinary workstation. Use an isolated or controlled analysis path for suspicious documents, scripts, executables, or ransomware-era files. Remove the test copy according to the approved evidence-retention rule after results are recorded.
Use the current restore-options reference for target, conflict and permission behavior.[1] Retention settings determine which historical or deleted-file versions can remain available; the sample browser’s dates do not establish another organization’s retention.[9]
Troubleshoot Restore State and Measure Real Performance
Classify the failure before changing settings. If the app is synchronizing with a destination, a cloud copy may still be available through the console. If a destination is offline or the device cannot connect, check service status, approved network path, proxy, DNS, firewall, endpoint time, TLS inspection, and the destination shown in the restore browser. Archive maintenance temporarily prevents restore from that destination, wait for the maintenance indicator to clear rather than repeatedly restarting the app. A generic problem message often points to target capacity or write permission. On macOS, verify current Full Disk Access.
If a restore remains at Preparing Files, CrashPlan recommends canceling queued downloads, selecting a small set, waiting for the size calculation, and testing Downloads with Rename and Current permissions. Use that small control to separate selection and archive issues from scale or target-path problems. When files are missing, verify the exact source device, destination, backup set, version date, and deleted-file display. A device replacement can mark data absent on the new device as deleted in the archive if files were not transferred first. A replaced drive name or letter can split history across paths.
Do not respond by immediately changing file selection, that can start archive deletion under retention rules. Record every diagnostic change and revert temporary settings. Measure restore performance from CrashPlan’s documented process. The app locates blocks in the archive index, reassembles them, downloads the file, then decompresses and decrypts it. Files are restored one at a time, and a large interrupted file restarts from the beginning rather than resuming from the interruption point. Network latency, shared bandwidth, ISP conditions, backup bandwidth limits, endpoint RAM and disk, target filesystem, wireless stability, sleep, security scanning, file size, and file count all affect results.
Prevent the device from sleeping, use stable approved connectivity, review CrashPlan bandwidth settings, and schedule large drills outside busy periods without granting uncontrolled network priority. Test at least three shapes: a small known file for functional proof, many small files for metadata and queue overhead, and a representative large file for sustained throughput and restart behavior. Record selected bytes, actual restored bytes, preparation time, transfer time, validation time, retries, effective rate, and bottleneck. Do not convert one office test into an organization-wide recovery promise. Use percentile ranges from repeated drills at relevant sites and define when an operator should split a restore, change target, escalate network issues, or contact CrashPlan support with a sanitized support bundle.
The troubleshooting guide supplies the small-file control for Preparing Files and the archive-maintenance boundary.[2] CrashPlan’s restore-process guide explains per-file processing and restart after interruption.[3] Console health and backup status are separate diagnostic inputs, not completed recovery tests.[10][11]
Worked recovery gate: a 24-minute transfer can still miss the objective
Hypothetical drill with synthetic files, an approved 60-minute recovery-time objective and a required version no older than the previous business day. Measure from the declared incident or request start used by that objective, not only from clicking Restore.
| Stage | Illustrative elapsed time | Acceptance evidence |
|---|---|---|
| Authorization and archive/version selection | 15 minutes | Correct user, source, destination, prior-day version and approval recorded. |
| Preparation and transfer | 24 minutes | Restore to the controlled folder completes without overwriting production files. |
| Integrity, permissions and application check | 28 minutes | Expected content opens for the intended user; validation is necessary recovery work. |
| Total and decision | 67 minutes: misses the 60-minute objective | Do not report a 24-minute recovery. Identify the actual delay, revise the runbook or recovery design, and retest before accepting the objective. |
Prove Device Replacement and Operational Recovery End to End
Treat replacement as a controlled recovery, not an installer shortcut. Before linking a new CrashPlan app to the old device identity, restore or otherwise transfer the old device’s required files. CrashPlan warns that files missing from the new endpoint can be marked deleted after replacement and then require deleted-file visibility to find. Where possible, preserve the exact username and Windows drive letters, on macOS grant Full Disk Access before beginning. If a custom archive key or archive-key password is in use, confirm authorized access before the maintenance window. For an administrator-driven replacement, perform the device restore to the new endpoint first, move validated content to its intended location, and then use Replace a Device.
The new app inherits the old archive and settings, the old device is deactivated, and a verification scan reconciles the new filesystem with the archive. Do not change the file selection until the verification scan and backup reach 100 percent. Deselecting paths too early can mark data for deletion. Validate that restored applications open, ownership is correct, the expected historical versions remain, backup resumes to the intended destination and alerts clear. CrashPlan documents that the old device is deactivated and signed out after replacement; if it is offline, it receives the command when it next connects.
Separately apply the organization’s device-security controls, because a pending CrashPlan command does not erase local files or prove that an offline computer is already secured. Build recurring recovery drills with four levels. Choose a drill schedule from risk, recovery objectives, change rate and contractual needs. One example is a monthly small-file check, quarterly representative endpoint recovery, a less frequent large-data or replacement exercise and an operational scenario covering identity outage and administrator succession. These are planning examples, not vendor-mandated intervals; increase frequency where the required recovery assurance calls for it.
Each drill should have a change record, approved source, synthetic or owner-approved data, start time, RTO and RPO target, operator, approver, restore method, target, options, actual duration, integrity result, permission result, application test, issues, cleanup, and corrective actions. Separate backup-health metrics from recovery assurance. Last connection, last backup activity, completion percentage, selected bytes, archive size, and alerts show collection state. Restore success rate, time to authorize, time to locate a version, time to first usable file, total recovery time, integrity, permission correctness, and application acceptance show recovery capability. Report both without publishing device or user details.
Track failed or overdue drills as service risk with an owner and deadline. A backup program is operationally ready when a different authorized technician can follow the current runbook, recover the approved data within the measured objective, explain every destructive choice, and return the target to a secure supported state.
The administrator console replacement procedure and app replacement wizard both require care with required files, identity and selection. Follow the procedure appropriate to the operator; an offline old device receives its replacement command only when it reconnects.[6][7]
If the expected file never entered the archive, return to the deployment and coverage gates rather than repeatedly changing restore options. If a valid archive is inaccessible to the operator, use the role, authentication and recovery-policy review to resolve the permitted path without granting blanket administrative access.
Official product documentation and ALLMSP resources
Frequently Asked Questions
Does a 100 percent CrashPlan backup prove files can be restored?
No. The indicator describes the selected data and destination. Test a known file and required historical version with the actual authorized operator, then check content, permissions and application use. Measure authorization, version discovery, preparation, transfer and validation against the declared recovery objective; a short download can still be a failed business recovery.
Where should the first CrashPlan test restore be saved?
Use an empty controlled folder with enough free space, not the production application’s original path. The app defaults to Downloads; a console device restore recommends an explicit Target Path and requires an online target. Record the conflict and permission options, verify the restored sample, and obtain approval before moving it into a working location.
Which CrashPlan file-conflict option is safest for a test?
CrashPlan recommends Rename existing and restore a copy when the operator is unsure. It keeps the restored filename and renames the existing file with an original-number prefix. Replacing the target can destroy useful current work, so require owner approval and a rollback copy before choosing that behavior.
Should a CrashPlan restore keep current or original permissions?
Current is the recommended default and changes ownership to the person performing the restore, improving immediate access. Original preserves prior ownership and permissions but may leave data inaccessible on a new device or profile. Test the required mode and validate owner, ACL, attributes, and application access afterward.
Why is Original location unavailable for some CrashPlan restores?
The CrashPlan app disables Original location when restoring to a different operating system from the source because the original path cannot be mapped safely. Use Downloads, Desktop, or another controlled folder, then validate and place the data using an approved migration procedure for the target platform.
What should be checked when CrashPlan cannot start a restore?
Use the reported state to choose the next check. Archive maintenance must finish; an offline destination or push target needs its connection restored. For a Preparing Files stall, follow CrashPlan’s small-file control: cancel queued restores, wait for size calculation, then use Downloads, Rename and Current permissions. If it fails, retain the exact error and check space, write access and macOS Full Disk Access before escalating.
Why can a large CrashPlan restore take longer than a normal download?
CrashPlan locates archive blocks, reassembles the file, downloads it, then decompresses and decrypts it. Files are processed one at a time, and an interrupted large file restarts from the beginning. Stable connectivity, adequate resources, no sleep, and realistic timing tests are therefore important.
What can make files appear missing after CrashPlan device replacement?
Files not transferred before replacement can be treated as deleted when the new device takes over the archive. Check the correct source, destination, backup set, historical date and deleted-file view. Do not immediately deselect the old paths. Once required files are recovered, complete the documented replacement and verification process before changing selection or retiring data.
When should file selection change after replacing a CrashPlan device?
Wait until the new endpoint completes its file verification scan and reaches 100 percent backed up. Changing or deselecting paths earlier can mark archive data for deletion before CrashPlan finishes reconciling the new filesystem. Validate versions, destination, application access, and resumed backup before cleanup.
What evidence should a CrashPlan recovery drill retain?
Keep the approved source and version, target, operator, authorization, restore method, conflict and permission choices, and integrity and application results. Record authorization, preparation, transfer and validation times separately and compare the complete interval with the declared objective. Store real paths, filenames, archive identifiers and restored content privately; publish only sanitized findings, owners and corrective deadlines.
Sources
- CrashPlan: Understanding restore file options ↩
- CrashPlan: Unable to restore ↩
- CrashPlan: File restore process and restore speeds ↩
- CrashPlan: Get started with CrashPlan backups ↩
- CrashPlan: Pushing a device restore from the console ↩
- CrashPlan: Replace a device from the console ↩
- CrashPlan: Replacing your device ↩
- CrashPlan: View your backed-up files ↩
- CrashPlan: Specify version, frequency, and retention settings ↩
- CrashPlan: Monitoring device health in the console ↩
- CrashPlan: Check the status of your backup ↩
- CrashPlan: Considerations for defining backup policies ↩